
Malware · 4h ago
Self‑Restoring WordPress Malware Recreates Deleted Backdoor in Seconds
A newly identified WordPress threat, labeled the SC family because of the "SC_" strings it embeds in compromised code,…
Trojans, stealers, loaders and backdoors.
A newly identified WordPress threat, labeled the SC family because of the "SC_" strings it embeds in compromised code,…

The U.S. Treasury Department’s Office of Foreign Assets Control (OFAC) announced sanctions against ten individuals and…
Security researchers have identified a new wave of malicious campaigns that exploit custom versions of OpenAI's…
Security researchers have observed a significant upgrade to the command‑and‑control (C2) infrastructure used by the…
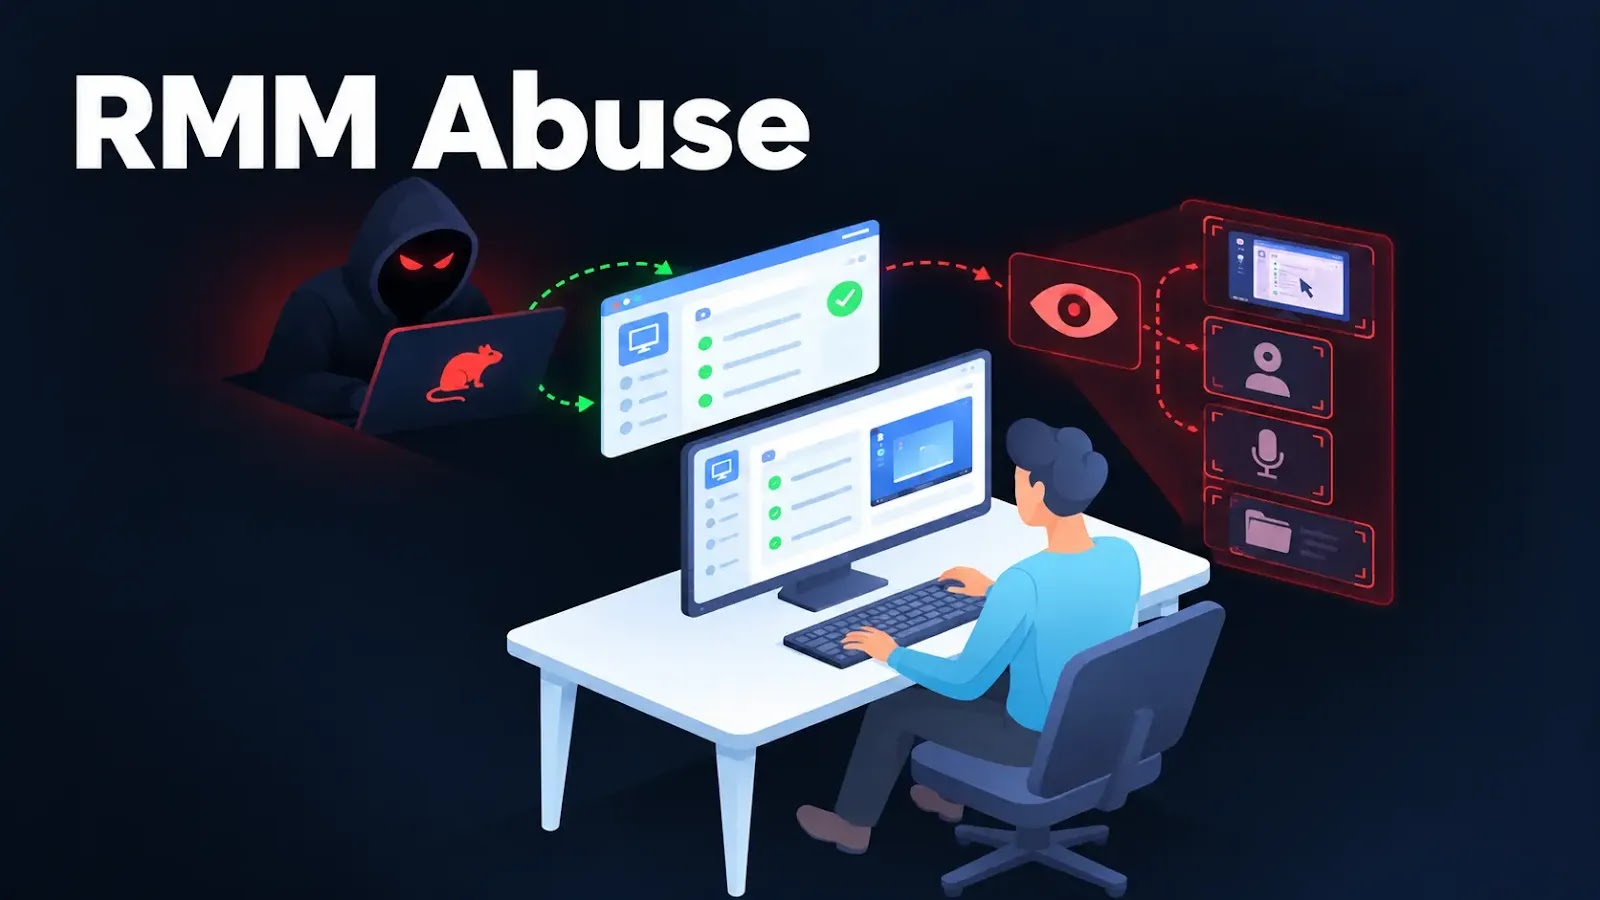
Security researchers have identified a new campaign in which threat actors leverage trusted remote monitoring and…

Security firm Cleafy has identified a new operational model for the RatHat Android banking trojan, which is being…

Two GitHub Actions that were hijacked during the May 2026 Mini Shai‑Hulud campaign resurfaced last week, prompting the…

A fresh variant of the MacSync trojan has been observed leveraging publicly shared iCloud calendar events as a covert…

A new Android threat dubbed RemControl has emerged as a malware‑as‑a‑service (MaaS) platform, delivering…
Security researchers have confirmed that the MovieReaper malware is being distributed through compromised files on the…
A newly identified Windows backdoor, dubbed TASK#STOMP, has been found to combine PowerShell scripts, scheduled tasks,…

Cybersecurity researchers have uncovered a new wave of malicious software being distributed through torrent files for…