Fake AI Chat Apps Disguised as ChatGPT and Claude Deploy Yoba Cryptominer via Signed GitHub Executables
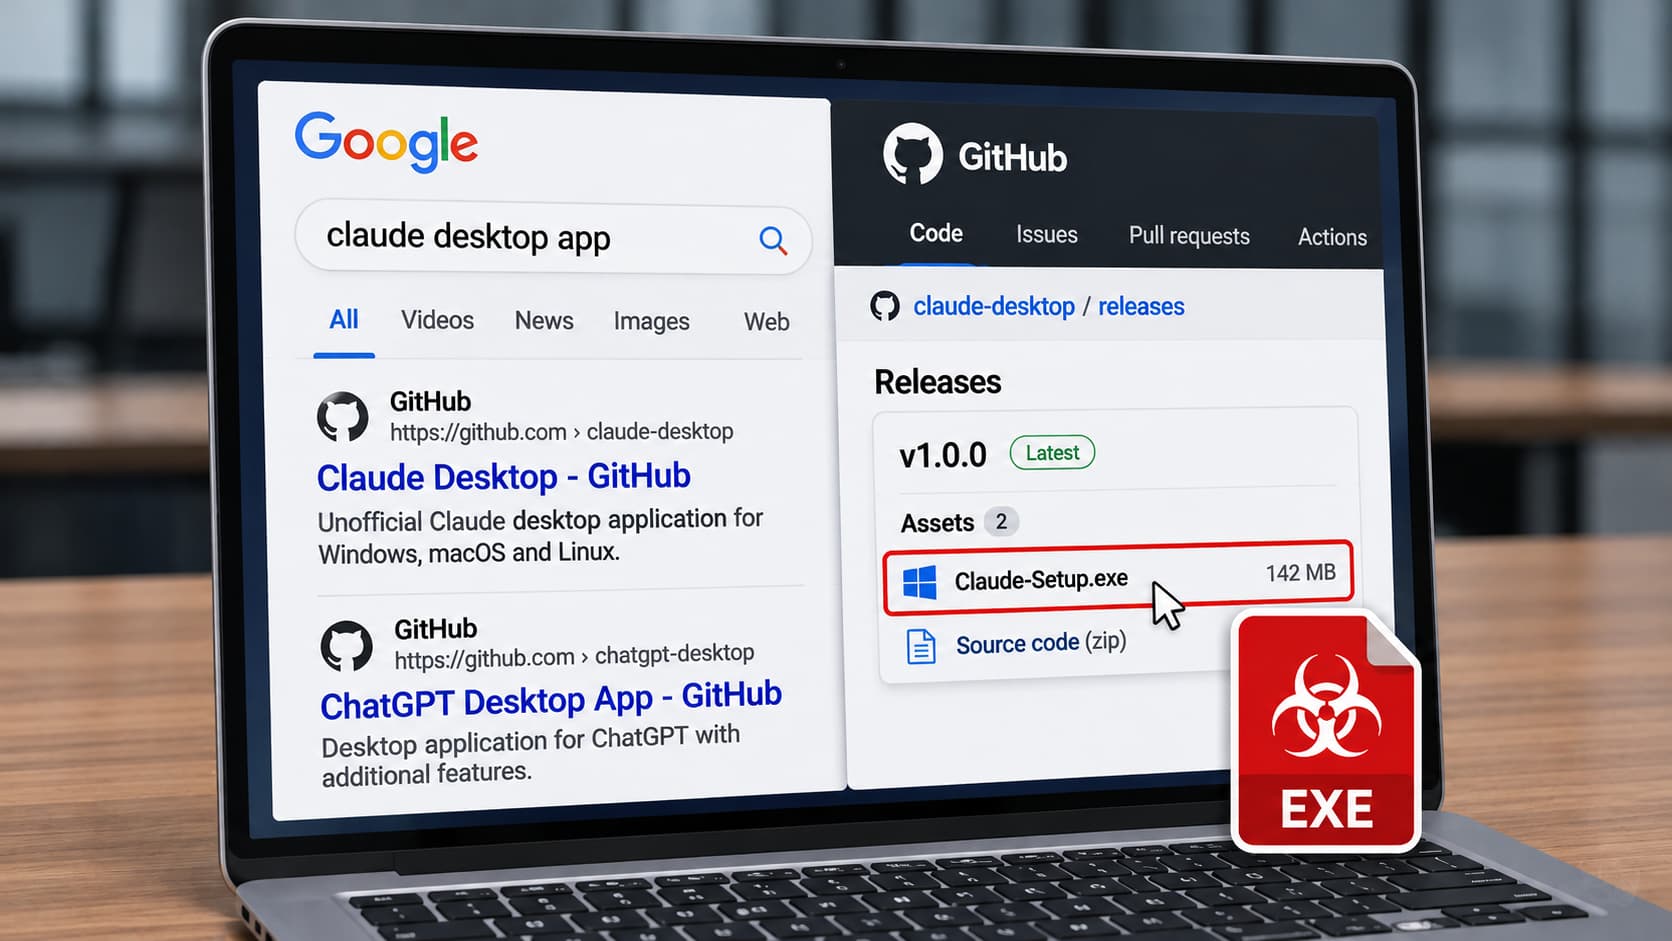
Security researchers have identified a campaign that uses counterfeit desktop applications masquerading as popular AI chat services to spread Yoba malware, a cryptomining trojan. The malicious packages are hosted on GitHub and are signed with legitimate certificates, allowing them to bypass many standard Windows warnings and entice unsuspecting users to install them.
The attackers publish what appear to be official Windows installers for "ChatGPT" and "Claude" on public GitHub repositories. Each installer is digitally signed, a tactic that gives the file an appearance of authenticity and reduces friction during the download‑and‑run process. Once executed, the program extracts the Yoba payload, which then begins mining cryptocurrency on the infected machine without the user’s knowledge.
Yoba is an open‑source cryptominer that has been repurposed by threat actors to monetize compromised systems. After installation, it typically hijacks CPU or GPU resources to mine coins such as Monero, and it can also serve as a dropper for additional malicious components. Because the miner runs in the background, victims often notice only a gradual slowdown or increased power consumption.
The use of signed executables is significant because many endpoint protection solutions give lower priority to files that carry a valid digital signature. This lowers the chances of detection and increases the likelihood that casual users will trust the download, especially when the file name references well‑known AI tools that have seen a surge in popularity.
Experts recommend that users obtain AI applications only from the official providers’ websites or trusted app stores, verify the publisher information in the file properties, and keep security software up to date. GitHub has been notified of the offending repositories and is expected to take down the malicious content, while Microsoft’s Windows Defender team is monitoring for related signatures. Ongoing vigilance is essential as threat actors continue to exploit the hype around generative AI to distribute malware.

Comments (0)
Be the first to comment.
Join the discussion