CVE & Exploits · Sep 21, 2026
New WordPress Core CSRF Bug ‘Click2Shell’ Enables Remote PHP Execution
A critical cross‑site request forgery (CSRF) flaw dubbed “Click2Shell” has been disclosed in the core of WordPress, the…
Rakesh tracks CVEs, zero-days, and exploit disclosures as they break, translating advisories into plain-language impact analysis. Background in vulnerability research, follows NVD and vendor bulletins closely.
251 stories filed
A critical cross‑site request forgery (CSRF) flaw dubbed “Click2Shell” has been disclosed in the core of WordPress, the…
A BYD Shark 6 sedan was demonstrated to be vulnerable to a remote intrusion that gave an attacker control over the…

A newly identified Windows‑based infostealer known as Remus has begun exfiltrating authentication tokens used with…

The latest edition of the Security Affairs Malware Newsletter, round 115, has been published, offering a curated…

The Security Affairs blog rolled out the latest edition of its weekly newsletter, marking the 595th issue and expanding…
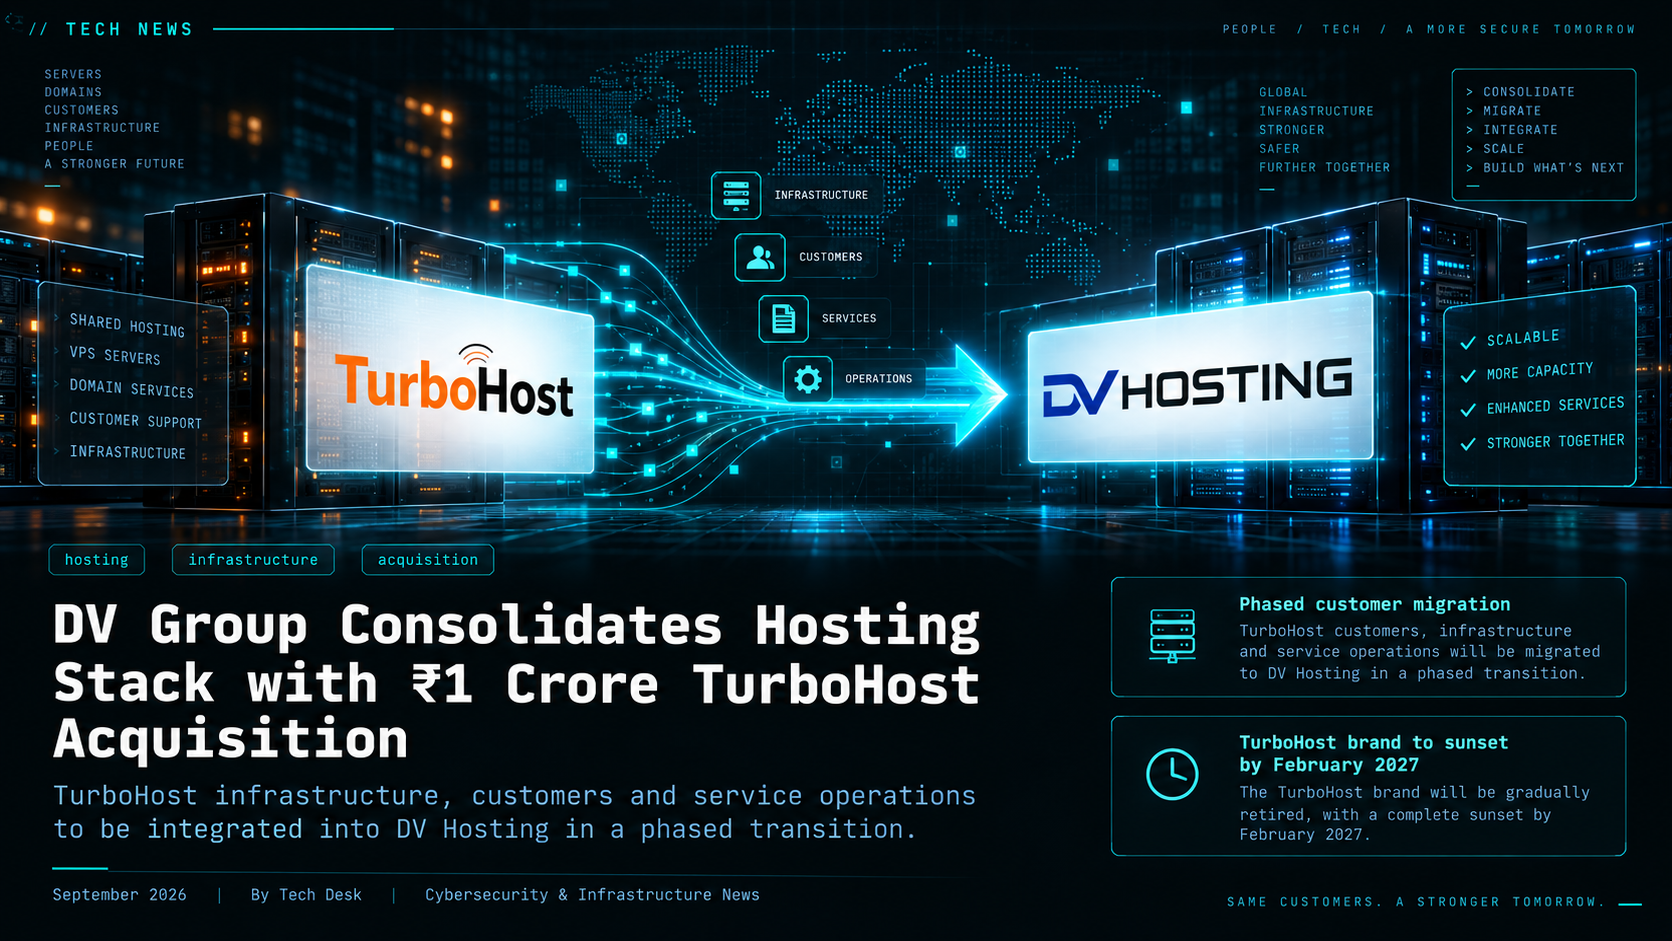
DV Group has acquired TurboHost in a ₹1 crore deal and will integrate its customers and hosting operations into DV…

Cyber‑security startup TigerByte Cyber announced it has moved out of stealth mode after raising a $3 million funding…
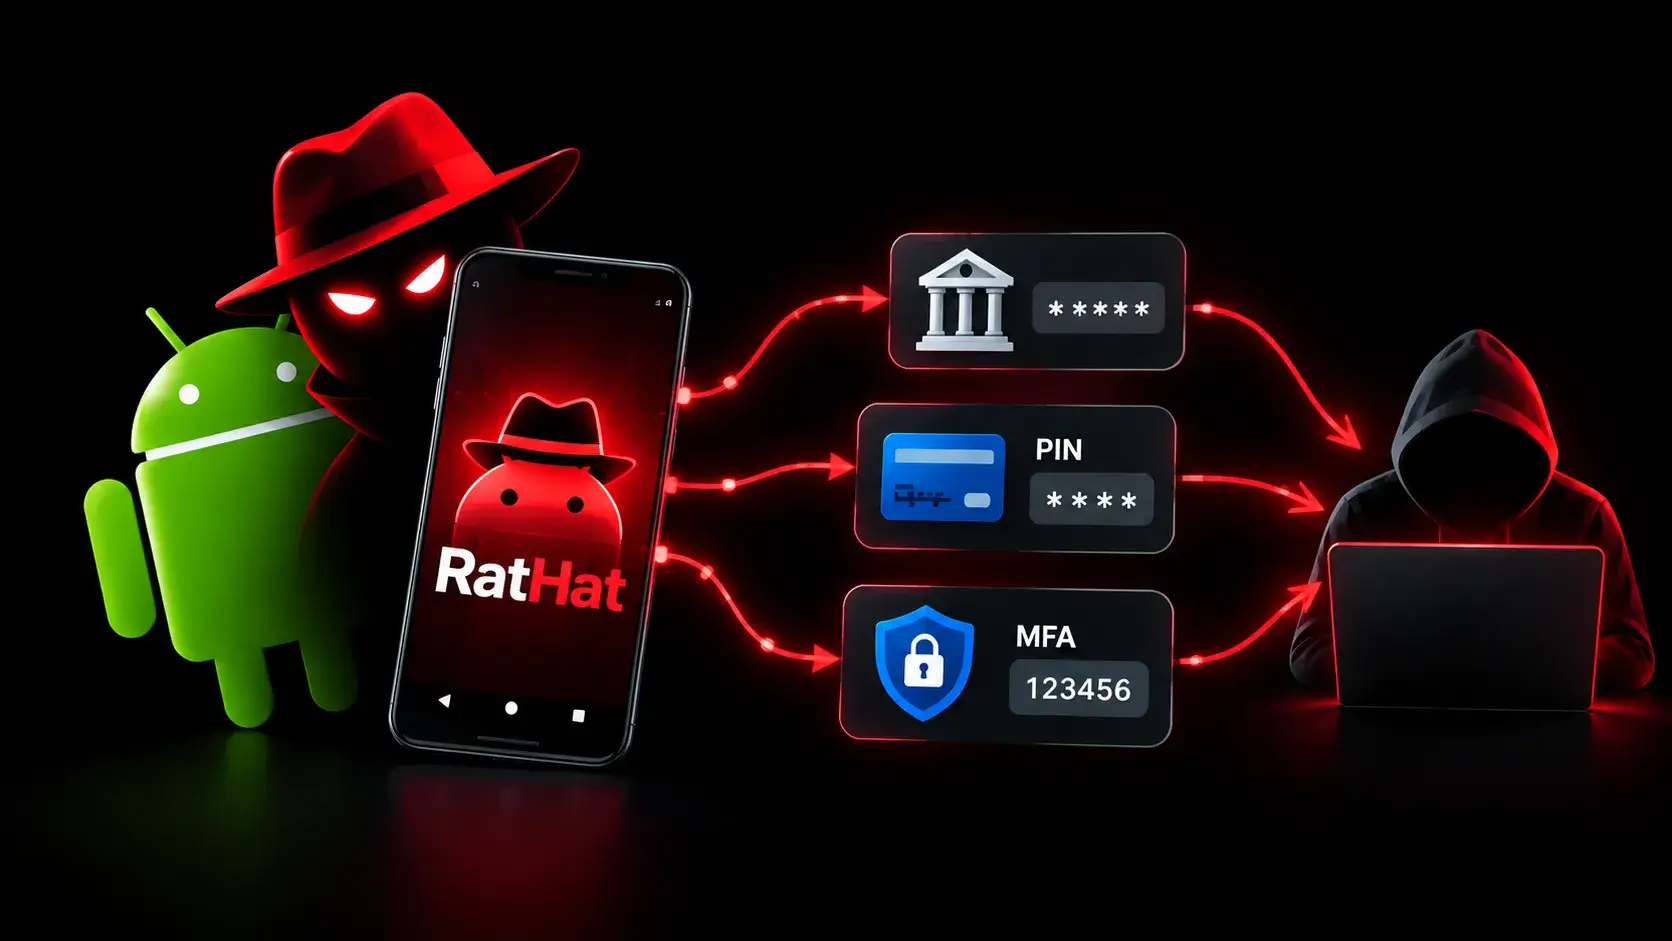
Security researchers have uncovered a novel Android banking Trojan named RatHat that leverages artificial‑intelligence…

French cybersecurity firm CrowdSec disclosed on September 18 that an attacker exfiltrated roughly 170 of its private…

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) announced on Friday that it has placed three recently…

Vectra AI announced the launch of Ascent, a new partner‑focused initiative designed to equip security firms and service…

A 24-year-old Texas resident, Ahmed Hossam Eldin Elbadawy, entered a guilty plea on federal charges Tuesday, admitting…