Malicious macOS Tool Masquerading as Zoom Installer Harvests Passwords via CloudSyncD Backdoor
A new macOS backdoor identified as CloudSyncD is distributing itself through a counterfeit Zoom installer, allowing…
Trojans, stealers, loaders and backdoors.
A new macOS backdoor identified as CloudSyncD is distributing itself through a counterfeit Zoom installer, allowing…
Security researchers have identified a fresh macOS threat that masquerades as a Zoom installer, using the popular…
A previously unknown Windows backdoor, dubbed Antino, has been used by a China-affiliated cyber‑espionage group to…
A newly identified macOS trojan, dubbed CloudSyncD, has been discovered concealing stolen credentials within a…
A newly identified WordPress threat, labeled the SC family because of the "SC_" strings it embeds in compromised code,…
Security analysts have identified a new Windows‑focused malware loader, dubbed 2CLoader, that employs a suite of…
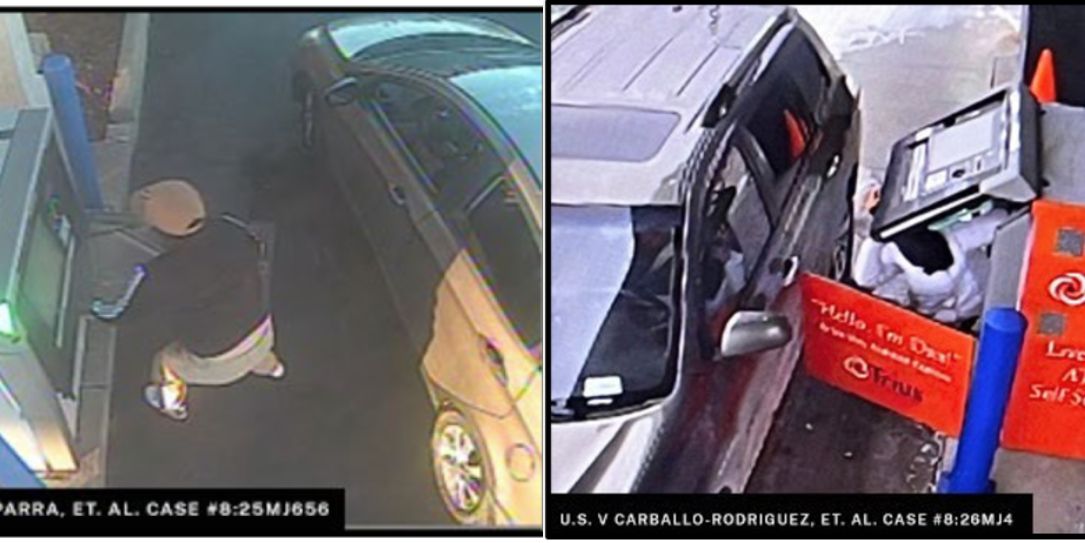
The U.S. Treasury Department’s Office of Foreign Assets Control (OFAC) announced sanctions against ten individuals and…
Security researchers have identified a new wave of malicious campaigns that exploit custom versions of OpenAI's…
Security researchers have observed a significant upgrade to the command‑and‑control (C2) infrastructure used by the…
Security researchers have identified a new campaign in which threat actors leverage trusted remote monitoring and…
Security firm Cleafy has identified a new operational model for the RatHat Android banking trojan, which is being…
Two GitHub Actions that were hijacked during the May 2026 Mini Shai‑Hulud campaign resurfaced last week, prompting the…