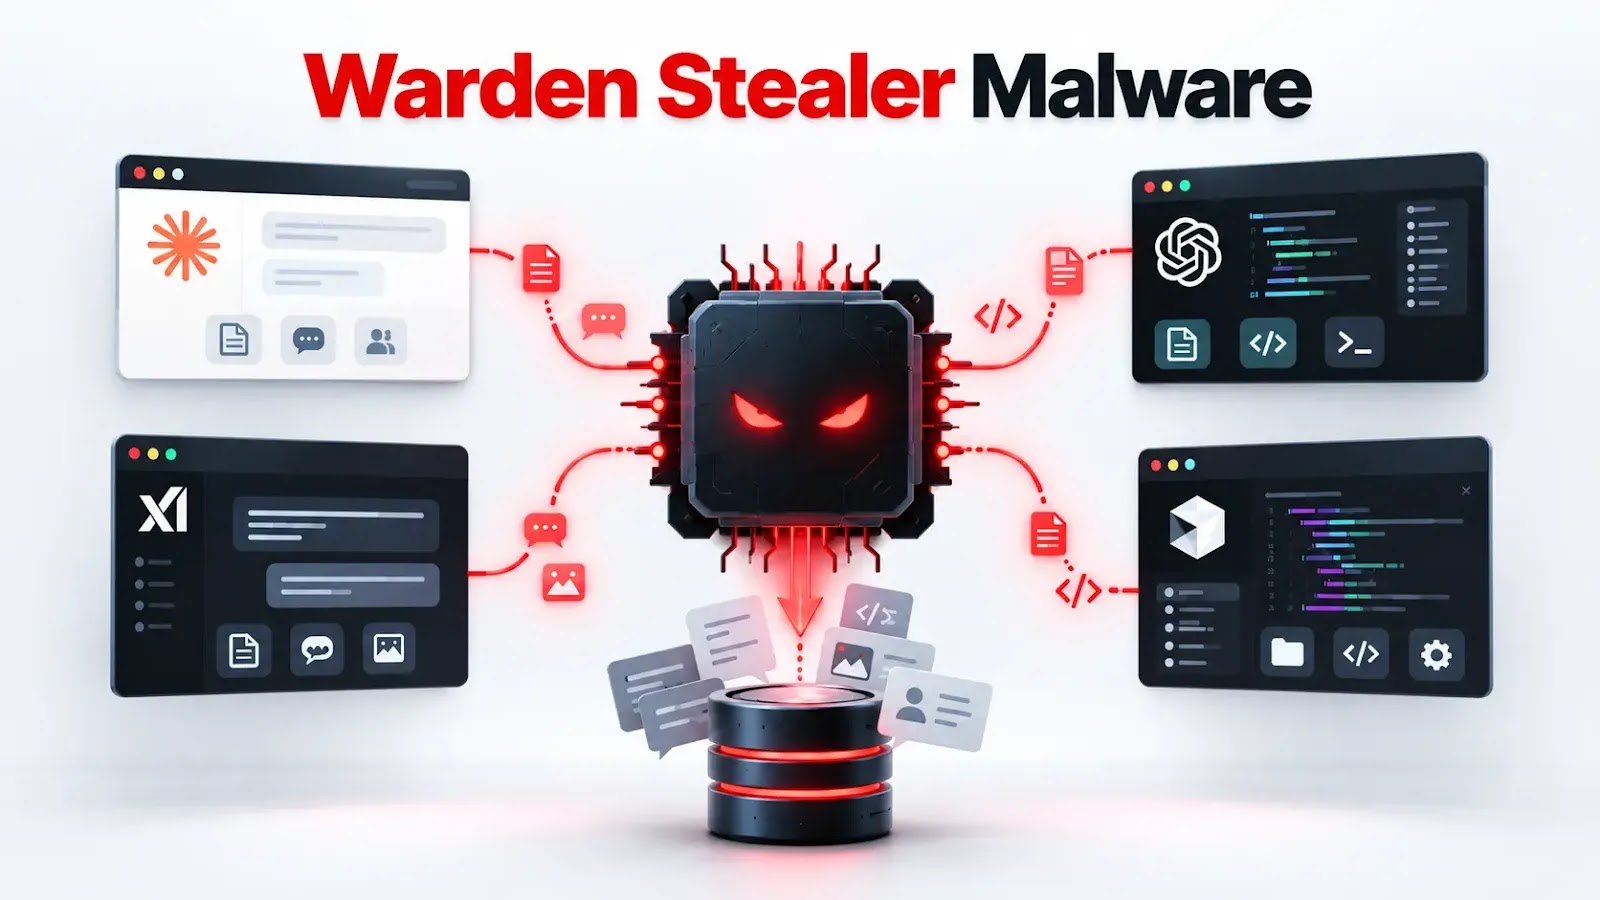
Rust‑Based ‘Warden Stealer’ Malware Hijacks AI Coding Assistants to Exfiltrate User Data
A newly identified malware family dubbed "Warden Stealer" is rapidly expanding its operations by targeting data stored…
Trojans, stealers, loaders and backdoors.
A newly identified malware family dubbed "Warden Stealer" is rapidly expanding its operations by targeting data stored…
Security researchers have uncovered a widespread campaign, dubbed "Midnight Mimosa," that embeds malicious code…
The Federal Bureau of Investigation announced this week that a Venezuelan cybercriminal has become the first hacker to…
The FakeGit operation has reemerged, this time populating more than 17,600 counterfeit repositories on GitHub with the…
Security researchers have identified a new wave of preinstalled malicious code, dubbed "Midnight Mimosa," on…
Security researchers have uncovered a new wave of Linux-based backdoors that are targeting telecom and network…
Security firm Rapid7 has identified a trio of previously unseen Linux-based backdoor families—BPFDoor, BPF Rekoobe and…
A federal judge in California has dismissed a lawsuit brought by a group of reporters from El Faro, the independent…
Security researchers have identified a fresh cyber‑espionage operation that leverages Microsoft Outlook and OneDrive as…
Security researchers have uncovered three previously unknown Linux-based backdoors that disguise themselves as…
Google announced a new security restriction for Android devices that activates when a user enables Advanced Protection,…
The U.S. Treasury Department announced on September 30 that it has placed sanctions on a financial network tied to the…