Rust‑Based ‘Warden Stealer’ Malware Hijacks AI Coding Assistants to Exfiltrate User Data
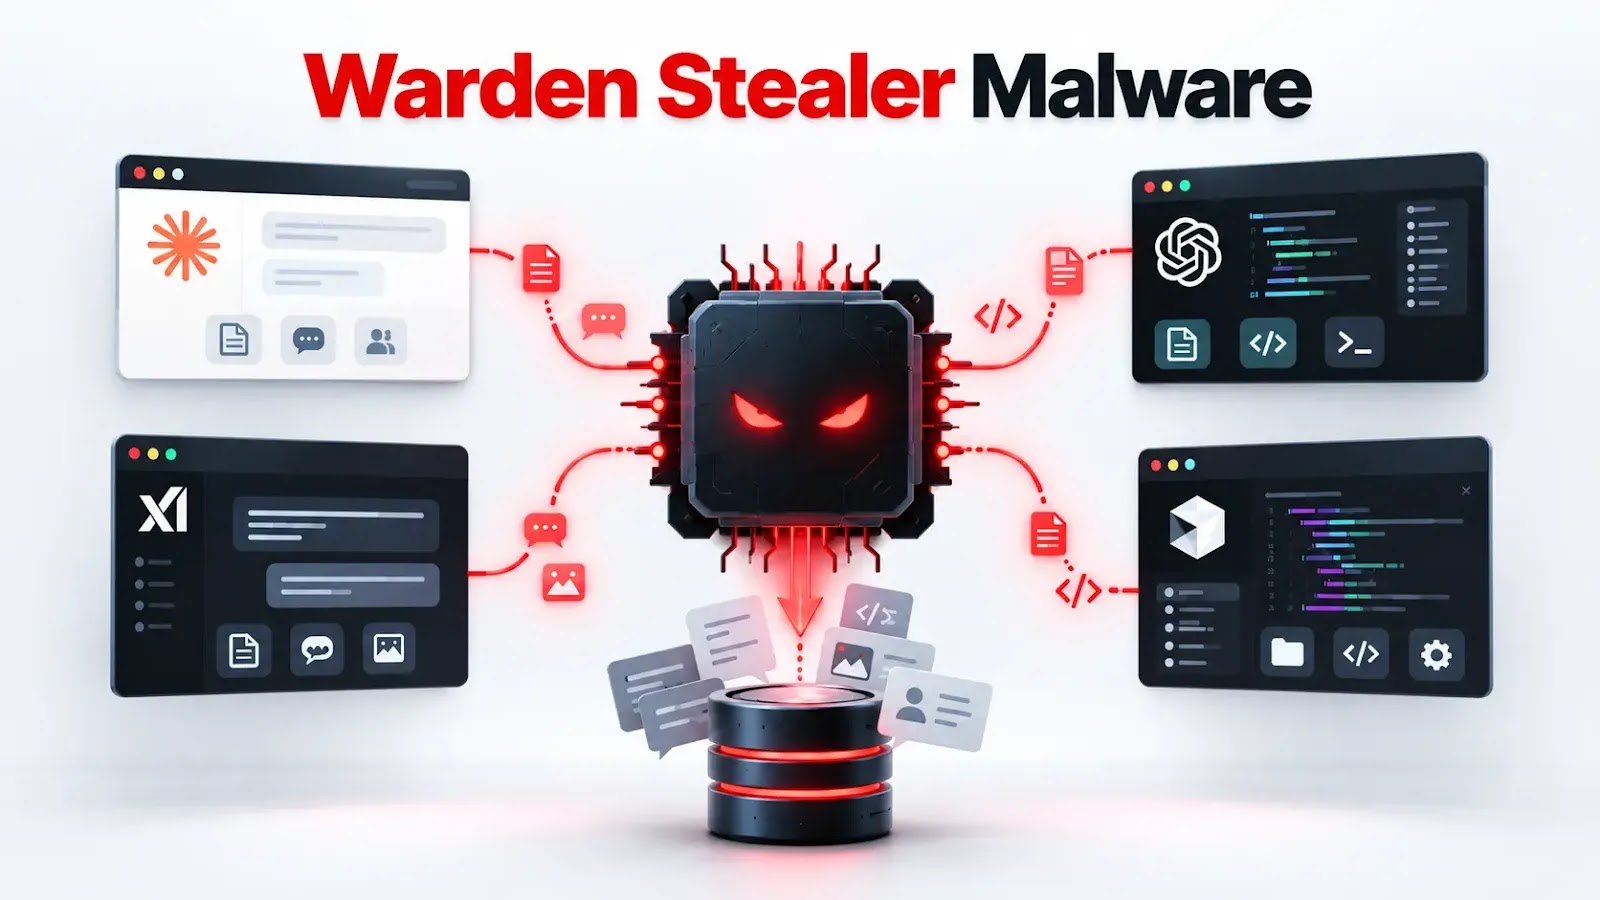
A newly identified malware family dubbed "Warden Stealer" is rapidly expanding its operations by targeting data stored in popular AI‑driven coding assistants such as Claude, Codex, Grok and Cursor. The threat, which is offered as a malware‑as‑a‑service platform, is built in Rust and functions as an infostealer that specifically harvests information generated by these AI agents.
Security researchers first observed the Rust‑based code in early 2024, noting its modular design that allows operators to customize payloads for different AI platforms. By intercepting API calls and local configuration files, the stealer can extract prompts, code snippets, and proprietary project details that users have fed into the assistants. The stolen data is then routed through encrypted channels to command‑and‑control servers operated by the malware service.
Analysts say the focus on AI coding tools reflects a shift in cybercriminal economics. As developers increasingly rely on large language models to write and debug software, the intellectual property embedded in prompts and generated code becomes a valuable commodity. The ability to siphon such material offers attackers a direct line to trade secrets, proprietary algorithms, and even unpublished source code.
Warden Stealer’s distribution model resembles other “malware‑as‑a‑service” offerings, where affiliates purchase access to the tool and receive updates that keep pace with evolving AI platforms. The Rust language provides performance advantages and resistance to some traditional detection methods, making the malware harder for conventional antivirus solutions to spot. Early victims have reported the presence of the stealer after noticing unexplained network traffic to foreign IP addresses and a slowdown in IDE performance.
Cybersecurity firms are warning that the threat landscape surrounding AI assistants is still nascent. While the core functionality of the assistants remains secure, the ecosystems surrounding them—such as local development environments, plugin extensions, and API keys—present attack surfaces that can be exploited. Users are advised to adopt strict credential hygiene, limit API key exposure, and monitor outbound traffic for anomalies.
Law enforcement agencies have yet to identify the operators behind the Warden Stealer service, but the rapid adoption by multiple criminal groups suggests a well‑organized infrastructure. Researchers continue to track the malware’s evolution, noting that future variants may expand beyond coding assistants to target other AI‑driven applications, including content creation and data analysis tools.
As AI continues to embed itself in software development workflows, experts stress the importance of integrating security considerations early in the adoption process. Regular updates, sandboxed execution of AI plugins, and robust monitoring can mitigate the risk posed by emerging threats like Warden Stealer, which exemplifies how cybercriminals are adapting to the newest technological frontiers.

Comments (0)
Be the first to comment.
Join the discussion