
Threats · 1h ago
Enterprise Security Calls for a Dedicated Threat Model for Mobile Device Management
As businesses increasingly rely on employees' personal smartphones to access corporate resources, security teams are…
Rakesh tracks CVEs, zero-days, and exploit disclosures as they break, translating advisories into plain-language impact analysis. Background in vulnerability research, follows NVD and vendor bulletins closely.
248 stories filed
As businesses increasingly rely on employees' personal smartphones to access corporate resources, security teams are…

Security researchers have identified a fresh macOS threat that masquerades as a Zoom installer, using the popular…
MetaMask, the popular cryptocurrency wallet service, confirmed on Thursday that it is dealing with an active security…

Cryptocurrency exchange Bitget announced on Wednesday that the $387.5 million theft reported last week was enabled by a…
Washington, D.C. – The Internet Society announced the launch of a new Global Online Trust and Safety Hub on September…

New research from cybersecurity firm Swimlane reveals a striking split in the impact of artificial intelligence on…
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued an emergency alert about a newly discovered…
Russian cyber‑espionage unit known as Star Blizzard has introduced a fresh phishing approach dubbed “RedFlick,” which…
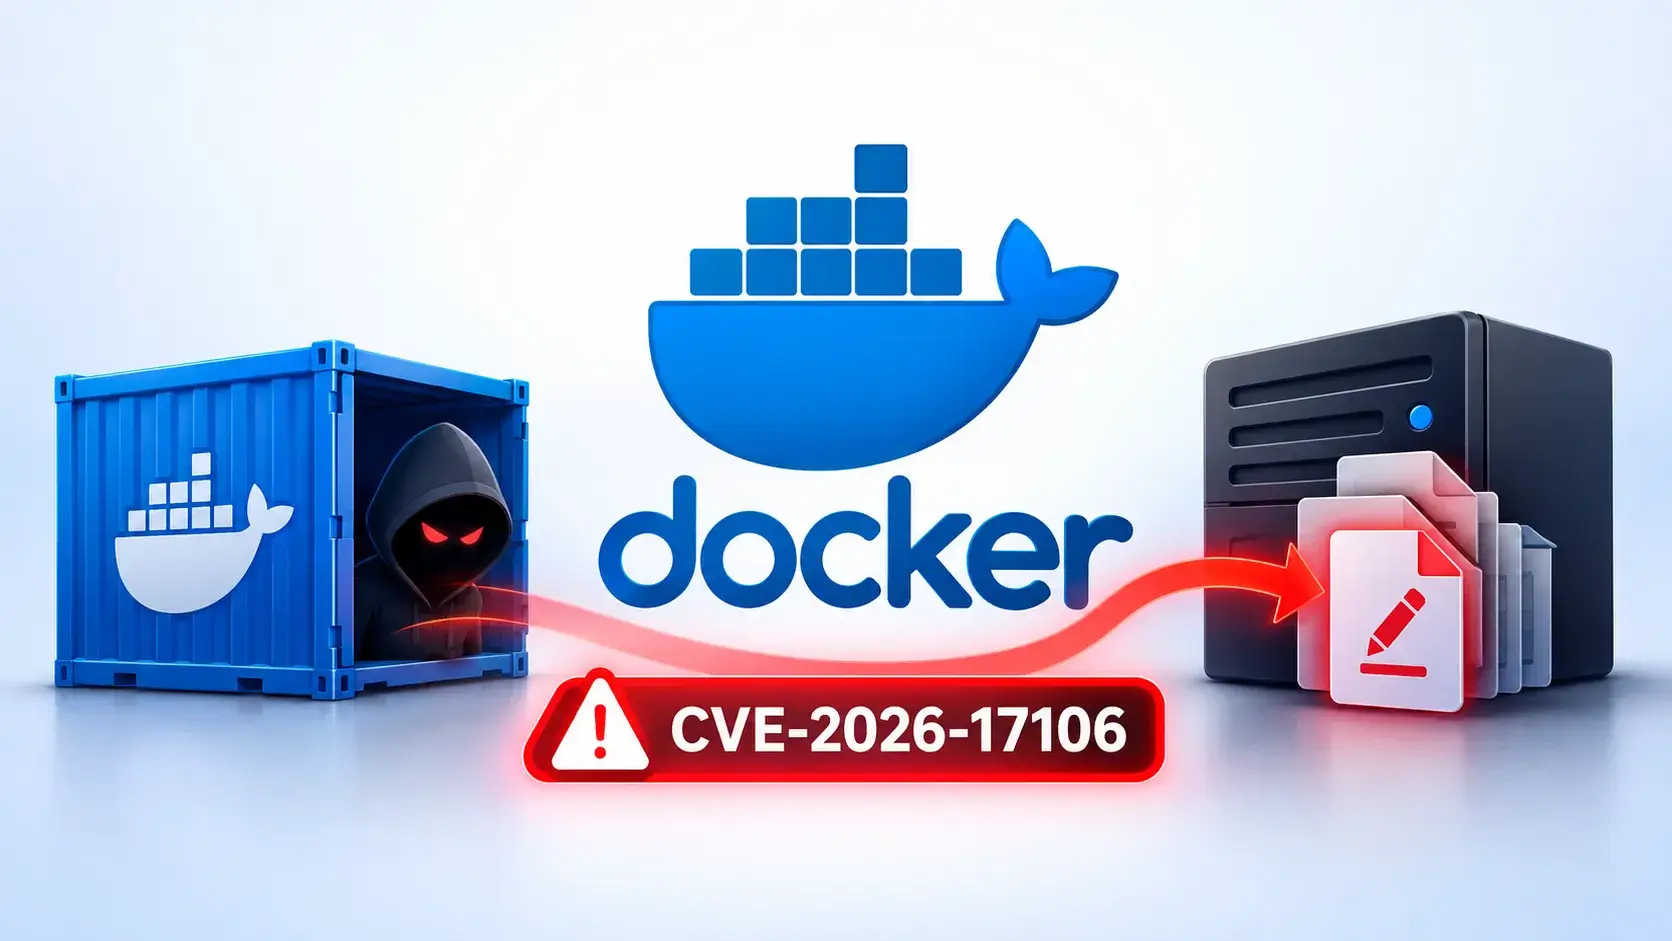
A newly disclosed vulnerability in Docker, catalogued as CVE-2026-17106 and dubbed “CopyEscape,” enables a malicious…
A newly disclosed vulnerability in the Linux kernel, cataloged as CVE-2026-72018, enables a local attacker who already…

Security researchers have uncovered a coordinated campaign that compromised more than 5,700 Microsoft 365 accounts…
Microsoft announced that its Windows Subsystem for Linux (WSL) now includes a generally available feature called WSL…