Zyxel patches critical zero‑day flaw after global breach of GS1900 switches
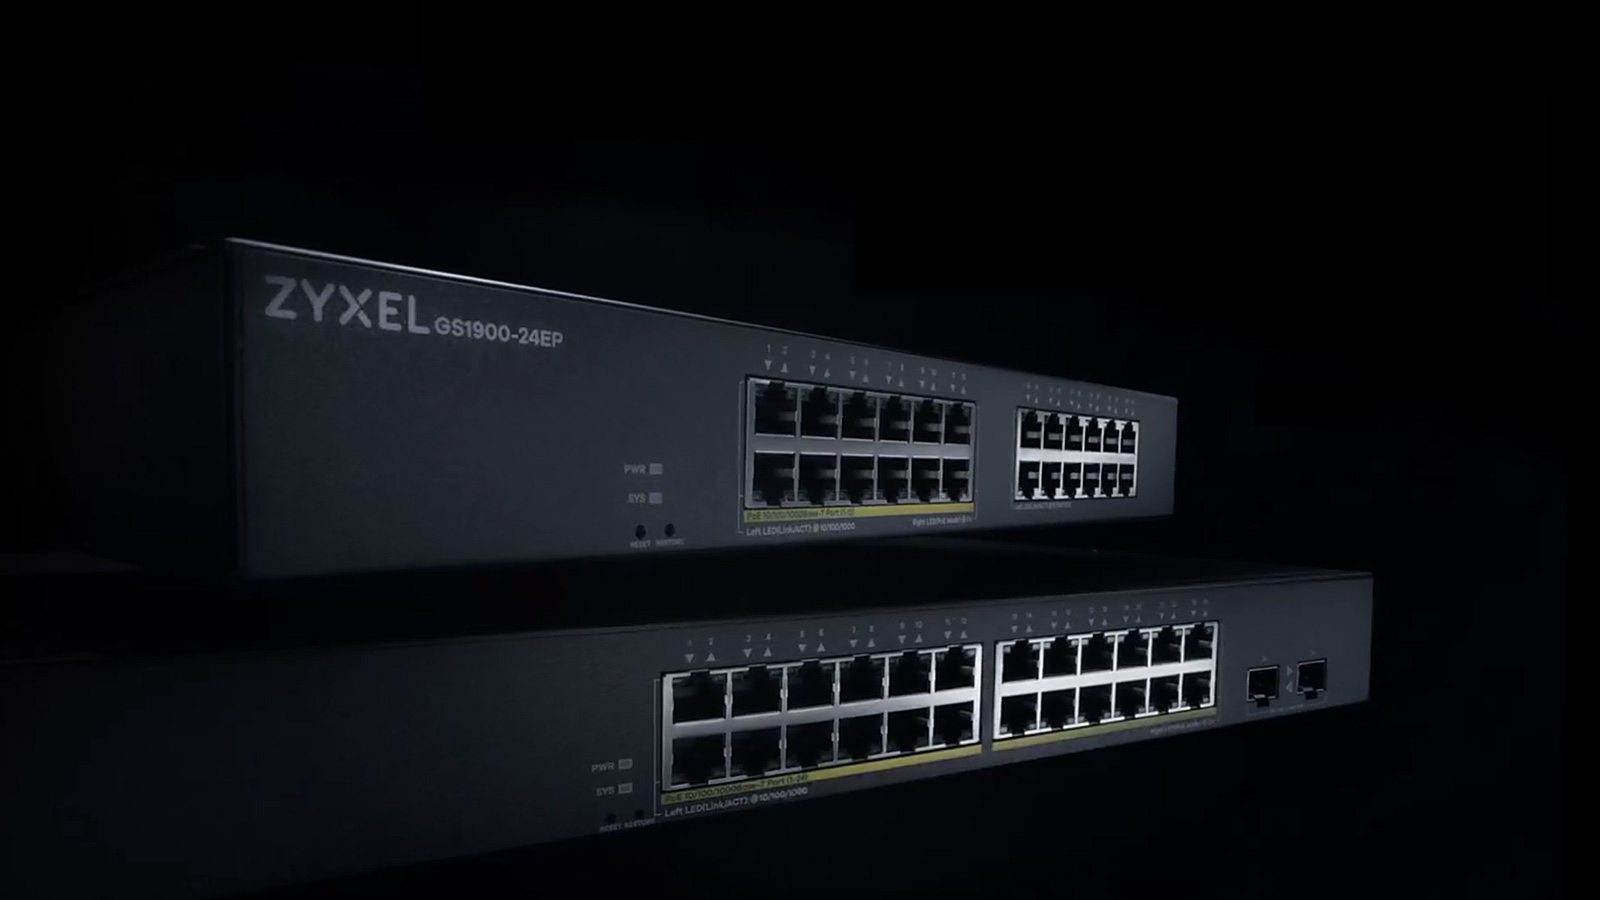
Zyxel announced a security update for its GS1900 line of network switches after a zero‑day vulnerability was leveraged by threat actors to infiltrate almost a thousand devices worldwide, gaining access to configuration files and login credentials.
The flaw, which resided in the switch firmware, allowed unauthenticated attackers to execute arbitrary commands on the management interface. By exploiting this weakness, malicious actors were able to download sensitive configuration data and harvest stored credentials, effectively opening a backdoor into corporate networks that relied on the affected hardware.
Security researchers first observed the abuse of the vulnerability in early 2024, noting that the compromised switches spanned a range of industries and geographic regions. The breach demonstrated how a single unpatched component in a network can cascade into broader exposure, as the stolen credentials could be reused to access other systems beyond the switches themselves.
In response, Zyxel released a firmware patch that addresses the root cause of the exploit and issued guidance urging customers to apply the update immediately. The company also recommended that administrators review logs for signs of unauthorized access and rotate any credentials that may have been exposed. Organizations that have not yet upgraded their GS1900 devices are advised to do so without delay to mitigate further risk.
The incident underscores the growing focus on supply‑chain and infrastructure security, reminding enterprises that network hardware, often perceived as a static asset, can be a lucrative target for attackers. Analysts say that timely patch management and regular auditing of network device configurations are essential defenses against similar zero‑day threats. As the cybersecurity community continues to monitor the situation, the Zyxel patch serves as a reminder that even well‑established vendors must stay vigilant against emerging vulnerabilities.
Comments (0)
Be the first to comment.
Join the discussion