Overlord RAT Deploys Bogus Brazilian Legal Notices to Target Windows PCs in New Malware Campaign
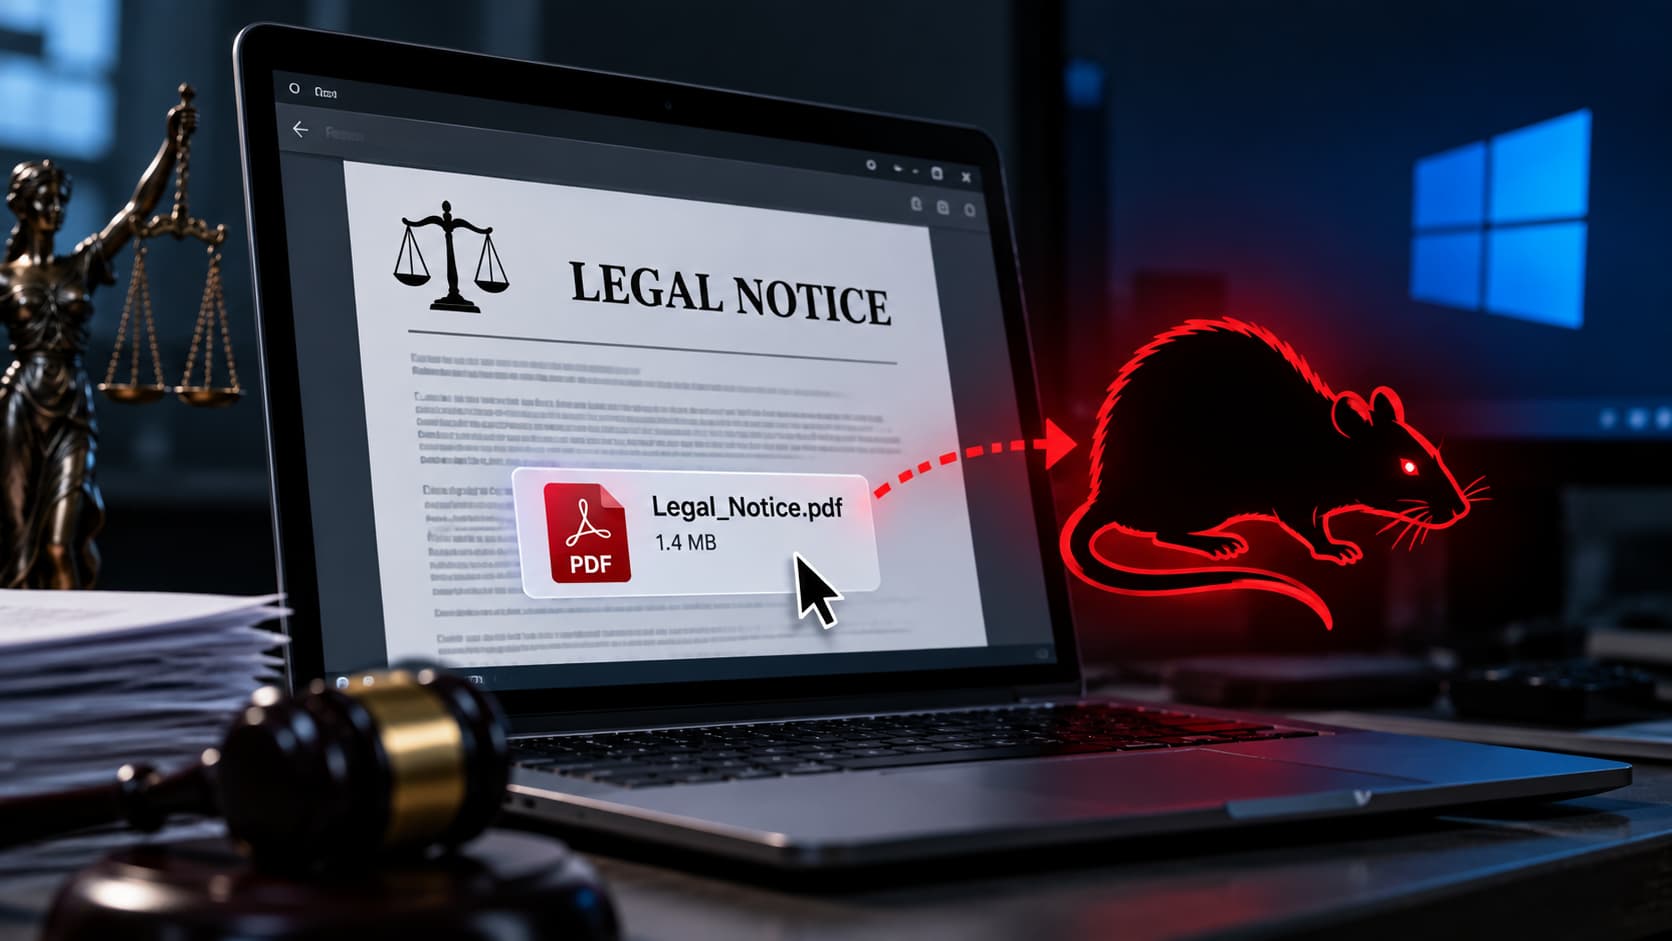
WatchGuard has identified a fresh wave of attacks in which the Overlord remote‑access trojan is distributed through counterfeit legal notices that appear to originate from Brazilian authorities.
The deceptive documents are delivered as email attachments or links that claim users must review or acknowledge a legal ruling. When opened, the files execute a loader that installs the Overlord RAT on Windows computers, granting attackers full control over the infected system.
In parallel with the Overlord campaign, security researchers observed the presence of the Lampion malware family and a separate remote‑access tool being dropped onto the same hosts, suggesting a multi‑payload strategy designed to maximize persistence and data exfiltration.
Overlord RAT is not new to the threat landscape, but its use of official‑looking Brazilian legal notices marks a shift toward more region‑specific social‑engineering tactics. Such lures exploit the public’s familiarity with government communications, increasing the likelihood that recipients will bypass security warnings.
The attacks target Windows PCs, which remain the dominant platform for both personal and enterprise use. By gaining remote access, adversaries can move laterally across networks, harvest credentials, and deploy additional payloads such as ransomware or espionage tools.
Security experts advise users and administrators to verify the authenticity of any legal correspondence received via email, avoid opening unexpected attachments, and keep operating systems and security software up to date. Email filtering solutions that detect spoofed sender domains can also reduce exposure.
WatchGuard’s report indicates that the campaign is ongoing, and analysts expect attackers to refine their lures as awareness grows. Continuous monitoring and user education will be essential to mitigate the risk posed by Overlord RAT and its accompanying malware components.

Comments (0)
Be the first to comment.
Join the discussion