Vanderbilt University Shuts Down Networks After Ransomware Claim
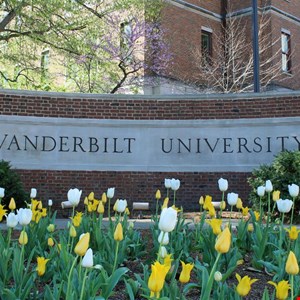
Vanderbilt University announced that it has taken its computer systems offline following a cyberattack that the BYOD ransomware group says has compromised the school’s databases and exfiltrated sensitive information.
The university’s IT department confirmed the shutdown on Friday, stating that the move was necessary to contain the breach and protect the integrity of its data. Officials declined to detail which specific systems were affected, but the decision to suspend network access aligns with standard practice after a ransomware incident.
BYOD, a ransomware collective that has previously targeted educational institutions, posted a message online asserting that it had encrypted Vanderbilt’s data and obtained confidential files. The group did not disclose the exact nature of the stolen material, nor did it provide a ransom demand in the initial claim.
Higher‑education campuses have become frequent targets for ransomware groups in recent years, drawn by the large volumes of personal, research and financial data they store. Security experts note that the open‑network policies often employed by universities can make them vulnerable to phishing, credential theft and the deployment of malicious software.
Vanderbilt’s response follows a broader trend of universities opting to isolate networks while forensic teams investigate. Law enforcement agencies, including the FBI, are typically notified in such cases, and the institution is expected to cooperate with any ongoing investigations.
University administrators have indicated that they are working to assess the scope of the breach and to restore services as quickly and safely as possible. They emphasized that protecting student and staff information remains a top priority and that affected individuals will be notified in accordance with applicable data‑privacy regulations.
The incident underscores the growing challenges that academic institutions face in defending against sophisticated cyber threats. As the investigation proceeds, observers will be watching how Vanderbilt balances rapid system recovery with the need for thorough security reviews, and whether the university will consider additional measures such as enhanced multi‑factor authentication, network segmentation, and regular ransomware‑response drills.


Comments (0)
Be the first to comment.
Join the discussion