DOJ Reveals Gootloader Linked to 44 Ransomware Attacks Causing $29 Million in Losses Since 2018
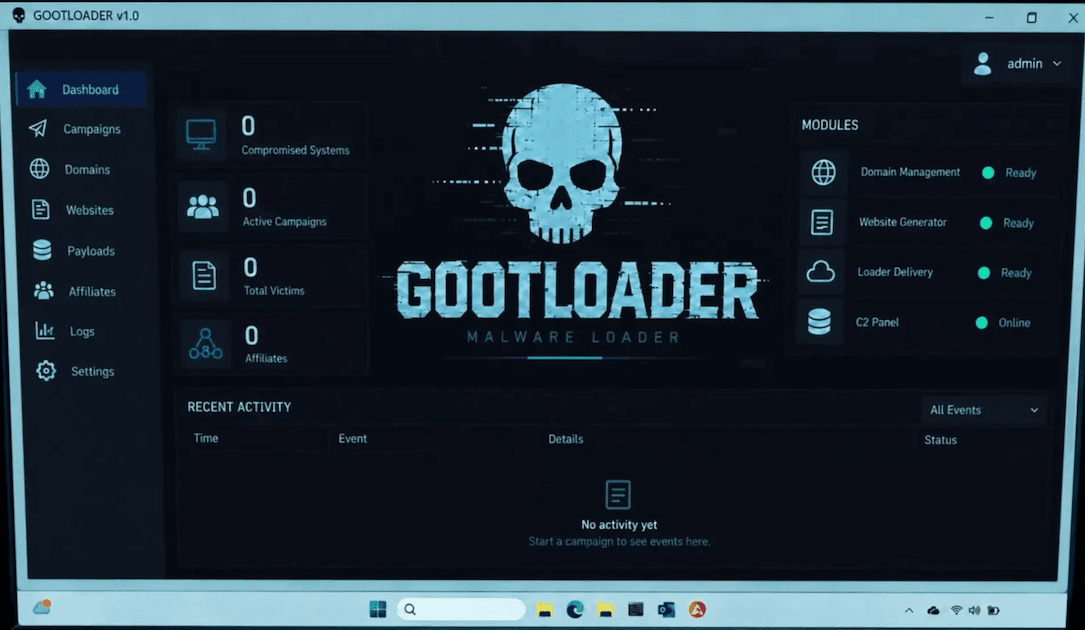
The U.S. Department of Justice disclosed that the malicious loader known as Gootloader has been employed in at least 44 ransomware incidents, collectively generating roughly $29 million in illicit proceeds since it first appeared in 2018. The announcement came during a briefing that coincided with European officials unveiling a coordinated anti‑malware operation aimed at disrupting similar cyber‑crime infrastructure.
According to DOJ officials, Gootloader functions as a dropper that first infiltrates a victim's network, then fetches and installs ransomware payloads such as REvil, LockBit or Conti. Its modular design allows threat actors to swap out the final ransomware component, making detection and attribution more challenging for defenders.
Law enforcement analysts traced the 44 confirmed incidents to a mix of small‑to‑medium enterprises and municipal entities across the United States. Victims reported downtime, data encryption and demands for payment in cryptocurrency, with total ransom requests adding up to the $29 million figure cited by the department.
The DOJ briefing highlighted that the Gootloader campaign has evolved alongside broader ransomware trends, exploiting common vulnerabilities in remote‑desktop services and unpatched software. By leveraging publicly available exploit kits and phishing emails, the loader can gain footholds with relatively low technical overhead, a factor that has contributed to its widespread adoption among ransomware groups.
European partners, who announced a joint operation targeting the same ecosystem of loaders and ransomware distributors, emphasized the cross‑border nature of the threat. Coordinated takedowns of command‑and‑control servers and arrests of key operators are expected to reduce the immediate risk, though experts warn that the underlying code can be repurposed by other actors.
Officials said the investigation remains open and that additional incidents may emerge as more victims come forward. The department urged organizations to adopt robust backup practices, timely patching, and multi‑factor authentication to mitigate the risk of Gootloader and similar tools. Continued collaboration between U.S. and European law‑enforcement agencies is positioned as a critical component of the broader strategy to curb ransomware activity worldwide.


Comments (0)
Be the first to comment.
Join the discussion