UK police detain two suspects after Microsoft shuts down AI‑powered cybercrime bot on Telegram
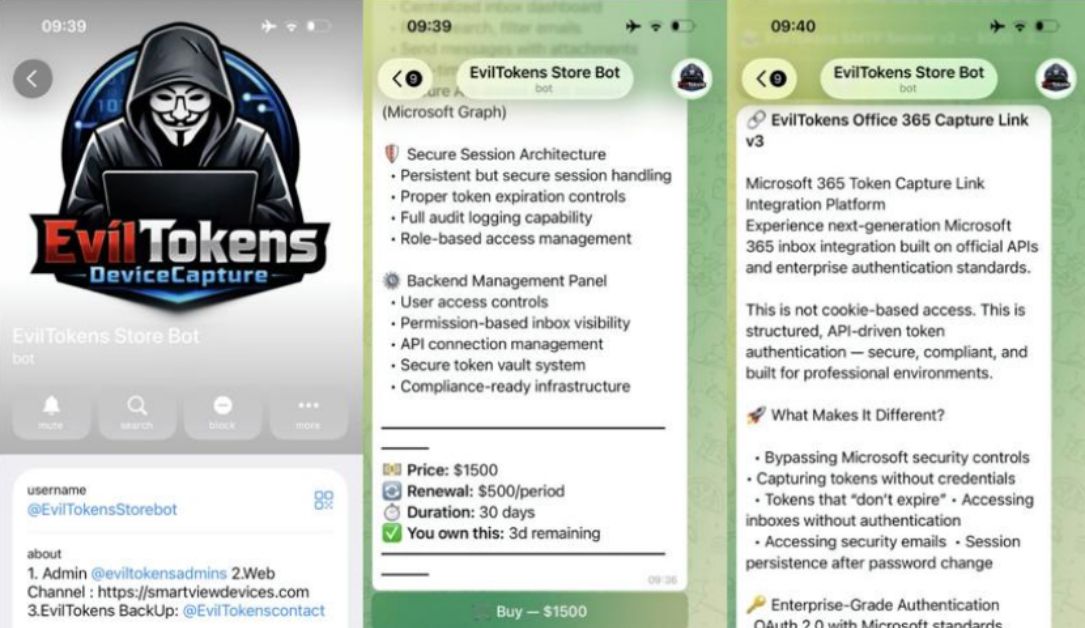
British authorities announced the arrest of two individuals following a coordinated effort with Microsoft to dismantle "EvilTokens," an artificial‑intelligence chatbot that was being marketed to cybercriminals on the Telegram messaging platform.
The service, which required a $1,500 upfront fee and a recurring $500 subscription, promised subscribers a suite of AI‑driven capabilities designed to breach user accounts, sift through compromised email inboxes and identify the most profitable ways to exploit stolen data. By automating these steps, the bot lowered the technical barrier for low‑skill operators to launch sophisticated attacks.
Microsoft’s Digital Crimes Unit flagged the operation after detecting suspicious traffic linked to the bot’s infrastructure. Working with UK law‑enforcement agencies, the tech giant issued takedown requests that led to the removal of the Telegram channel and the seizure of associated servers. The subsequent investigation resulted in the apprehension of the two individuals believed to be responsible for running the service.
The case highlights a growing trend where artificial‑intelligence tools are being packaged as subscription services for illicit use. Similar “crime‑as‑a‑service” platforms have emerged in recent years, leveraging the rapid advances in machine learning to automate tasks such as password cracking, phishing content generation and data exfiltration. This evolution presents a challenge for defenders, who must now contend with adversaries that can scale attacks with minimal manual effort.
While the arrests represent a tangible disruption of the EvilTokens operation, experts caution that the model is likely to reappear in new forms. Ongoing collaboration between technology firms and law‑enforcement bodies will be essential to track and neutralize such AI‑enabled threats before they mature into larger criminal enterprises. The incident serves as a reminder that the misuse of emerging technologies can quickly translate into real‑world harm, prompting calls for stronger oversight and rapid response mechanisms.



Comments (0)
Be the first to comment.
Join the discussion