Russian APT28 Deploys New HOOKEDGE Backdoor in European Spy Campaigns
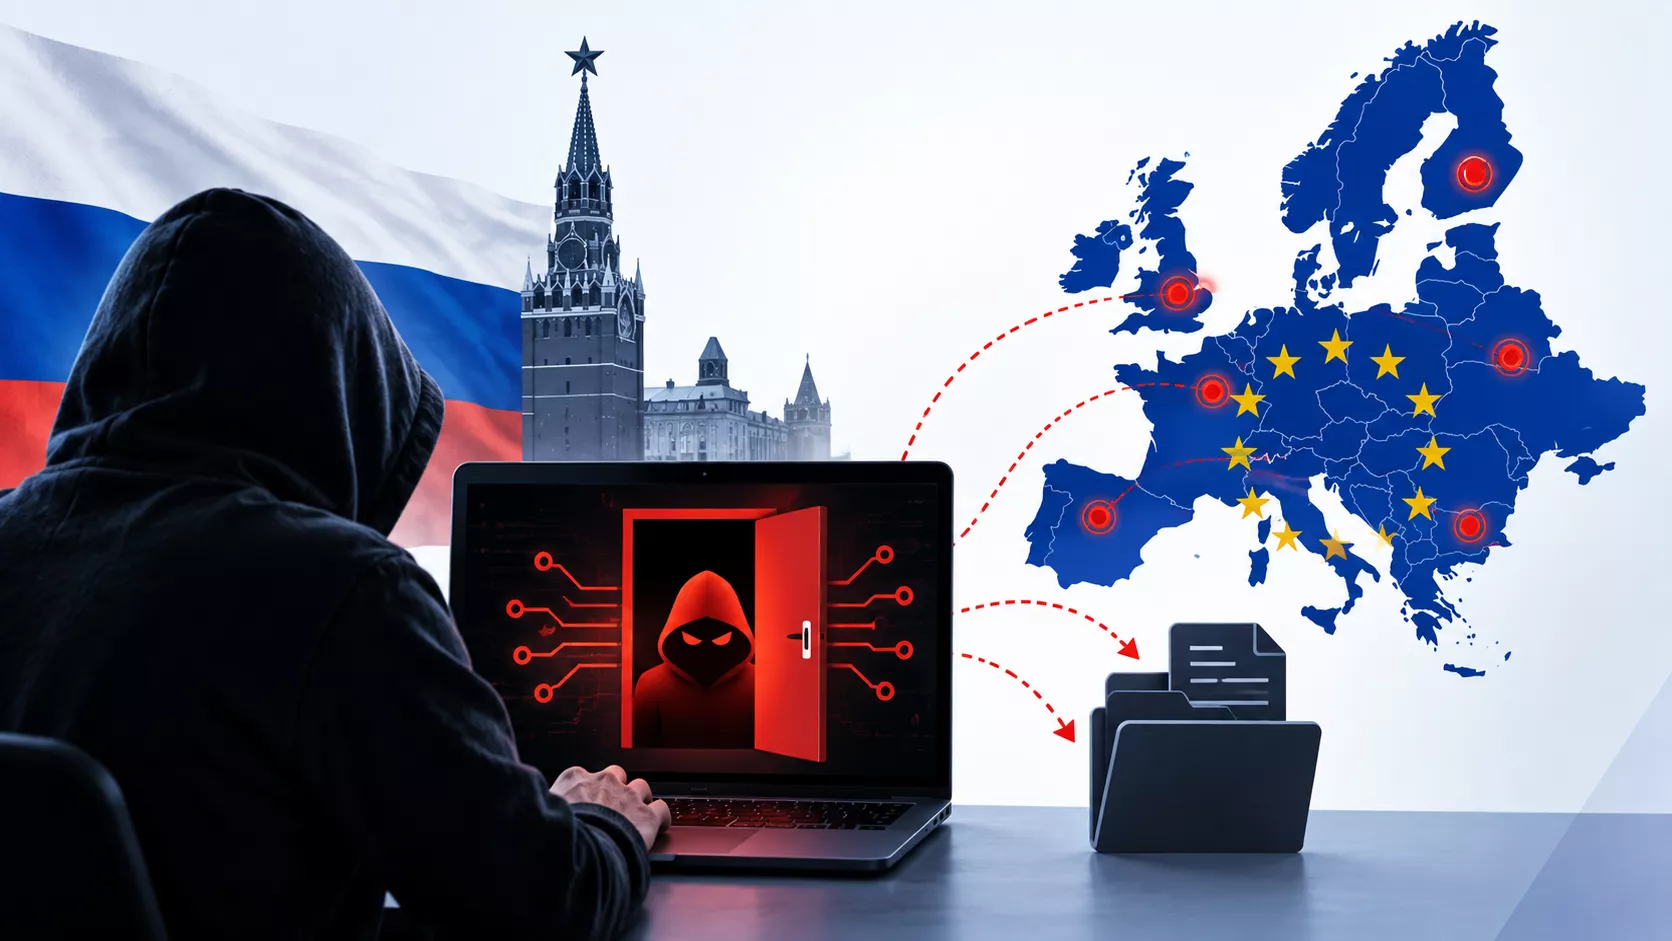
Security researchers have identified a fresh Windows-based backdoor, dubbed HOOKEDGE, being used by the Russian state‑linked group known as BlueDelta—also referred to as APT28, Fancy Bear, or Forest Blizzard—in ongoing espionage operations aimed at government, diplomatic and defence‑manufacturing entities throughout Europe.
The tool, described as lightweight and modular, appears to have been rolled out in a series of coordinated intrusions over the past several months. Analysts say its design focuses on stealth and rapid data exfiltration, allowing operators to maintain persistence on compromised networks while evading many conventional detection mechanisms.
BlueDelta has a long history of targeting political and military institutions across the continent, often leveraging custom malware to harvest sensitive communications and technical documents. The emergence of HOOKEDGE follows a pattern of the group adapting its toolkit to circumvent evolving security measures, a tactic observed in earlier campaigns that employed malware such as X-Agent and Sofacy.
European cyber‑defence agencies, including the EU Agency for Cybersecurity (ENISA) and national Computer Emergency Response Teams, have issued alerts urging organisations to review their Windows endpoint security configurations. Recommendations emphasize applying the latest patches, enforcing multi‑factor authentication, and monitoring for unusual network traffic that could indicate the presence of the new backdoor.
While no public attribution of specific incidents has been made, the detection of HOOKEDGE underscores the persistent threat posed by state‑backed actors in the region. Experts suggest that heightened vigilance, information sharing among allies, and investment in advanced threat‑hunting capabilities will be essential to mitigate further compromise as the cyber‑espionage landscape continues to evolve.



Comments (0)
Be the first to comment.
Join the discussion