Malicious Chrome VPN Add‑Ons Redirect Users to Hidden Proxy Network
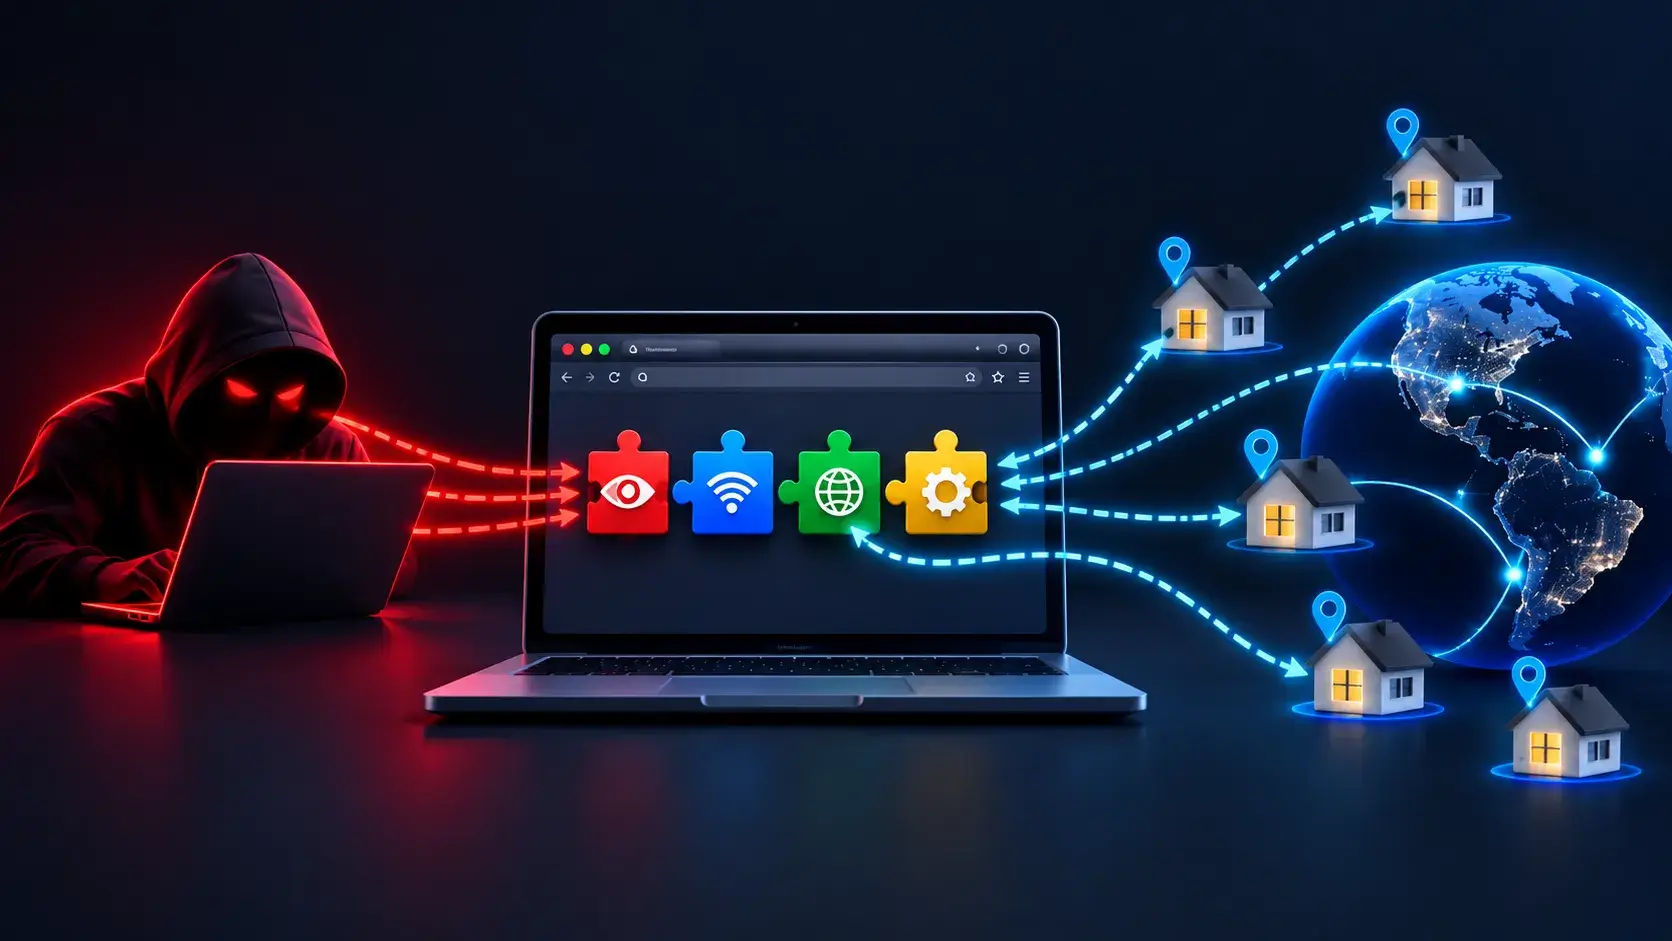
A security investigation has uncovered a coordinated operation involving 31 Russian‑language Chrome extensions that masquerade as free VPN services. Rather than protecting privacy, the extensions silently funnel users' web traffic through a remote proxy infrastructure controlled by the attackers, effectively turning ordinary browsers into nodes of a residential proxy network.
The extensions, marketed under generic names such as “VPN for You” or “VPN for Chrome,” share a common codebase that was first identified by security researchers on September 19, 2026. Analysis shows the code intercepts all outgoing HTTP and HTTPS requests, rewrites them to pass through servers operated by the threat actors, and then returns the content to the victim’s browser without any indication of the redirection.
Because the traffic is relayed through residential‑IP addresses, the malicious network can be used to bypass geo‑restrictions, conduct fraud, or mask the origin of illicit activity. Users who install the extensions believing they are enhancing their online security unwittingly contribute to a larger proxy pool that can be rented out to cybercriminals.
The campaign appears to be centrally managed, with the same back‑end command‑and‑control (C2) endpoints serving all 31 extensions. This level of reuse suggests a single group is behind the operation, leveraging the popularity of free VPN tools to achieve scale. Researchers note that the extensions are distributed through unofficial channels and, in some cases, through the Chrome Web Store before being removed after the malicious behavior was reported.
Experts warn that the threat is not limited to Russian speakers. The extensions are packaged with English‑language descriptions and screenshots, making them attractive to a global audience seeking free VPN solutions. The deceptive nature of the add‑ons underscores a broader trend where attackers exploit the trust users place in browser extensions to gain persistent network access.
Google has responded by revoking the extensions’ listings and issuing a security advisory urging users to uninstall any VPN‑styled add‑ons that were not obtained from verified sources. The company also pledged to tighten its review process for extensions that claim to provide privacy or security functions.
Cybersecurity analysts recommend that users rely on reputable VPN providers that employ transparent, audited infrastructure and that they regularly audit the extensions installed in their browsers. Network administrators are advised to monitor outbound traffic for unusual proxy patterns that could indicate compromised browsers within an organization.
The discovery highlights the ongoing challenge of policing the ecosystem of browser extensions, where malicious code can be hidden behind legitimate‑sounding functionality. As the market for free privacy tools continues to grow, security researchers say vigilance and user education remain essential to prevent similar abuse in the future.



Comments (0)
Be the first to comment.
Join the discussion