npm Supply‑Chain Attack Named MALFEX Targets Windows Users with Credential‑Stealing Malware
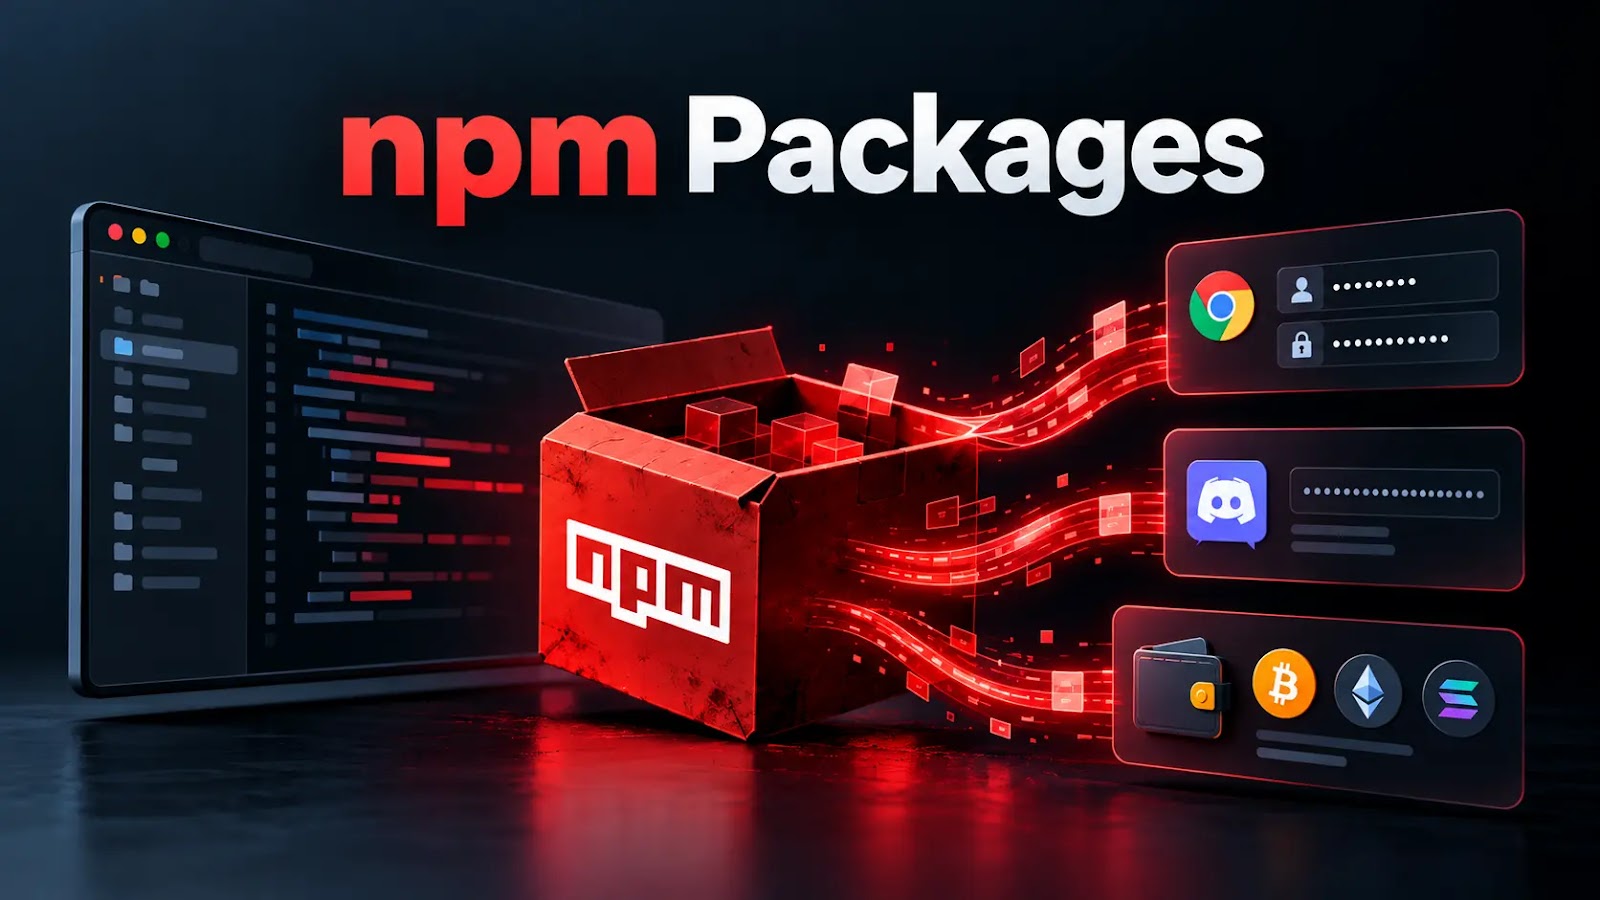
Security researchers have identified a new supply‑chain campaign on the npm registry, labeled MALFEX, that distributes Windows‑focused malware through eight compromised packages. The malicious modules are designed to harvest browser passwords, Discord authentication tokens and cryptocurrency wallet credentials, then exfiltrate the data to remote servers.
npm, the default package manager for JavaScript, powers millions of projects worldwide. Because developers routinely add third‑party libraries with a single command, a compromised package can quickly reach a large user base. Supply‑chain attacks exploit this trust relationship, inserting harmful code into otherwise legitimate software distributions.
According to the investigation, the MALFEX operation has been active since August 2023 and appears to be run by a single individual or tightly coordinated group. The campaign deploys several payloads, including the Overlord remote‑access trojan, a custom information‑stealer dubbed “movinlike,” and a separate downloader that fetches additional malicious components after initial infection.
When a victim installs one of the tainted npm packages on a Windows machine, the embedded script silently drops a binary executable. The payload then scans installed browsers for saved login data, extracts Discord tokens stored by the desktop client, and scans for cryptocurrency wallet files or extensions. Collected data is packaged and sent to command‑and‑control servers controlled by the attacker.
The breach poses a direct risk to developers and end‑users alike. Stolen credentials can enable account takeover, while compromised crypto wallets may result in financial loss. The incident also underscores the broader vulnerability of open‑source ecosystems, where a single malicious contribution can ripple across thousands of downstream projects.
GBHackers first reported the campaign, prompting npm to remove the offending packages and issue warnings to users. Security experts recommend that developers verify package integrity, employ npm’s audit feature, lock dependencies to known‑good versions, and consider two‑factor authentication for publishing accounts. Ongoing monitoring by the research community aims to track the operator’s activity and prevent further distribution of the malicious modules.

Comments (0)
Be the first to comment.
Join the discussion