International Task Force Dismantles KillSec Ransomware Network, Arrests Teen Suspect
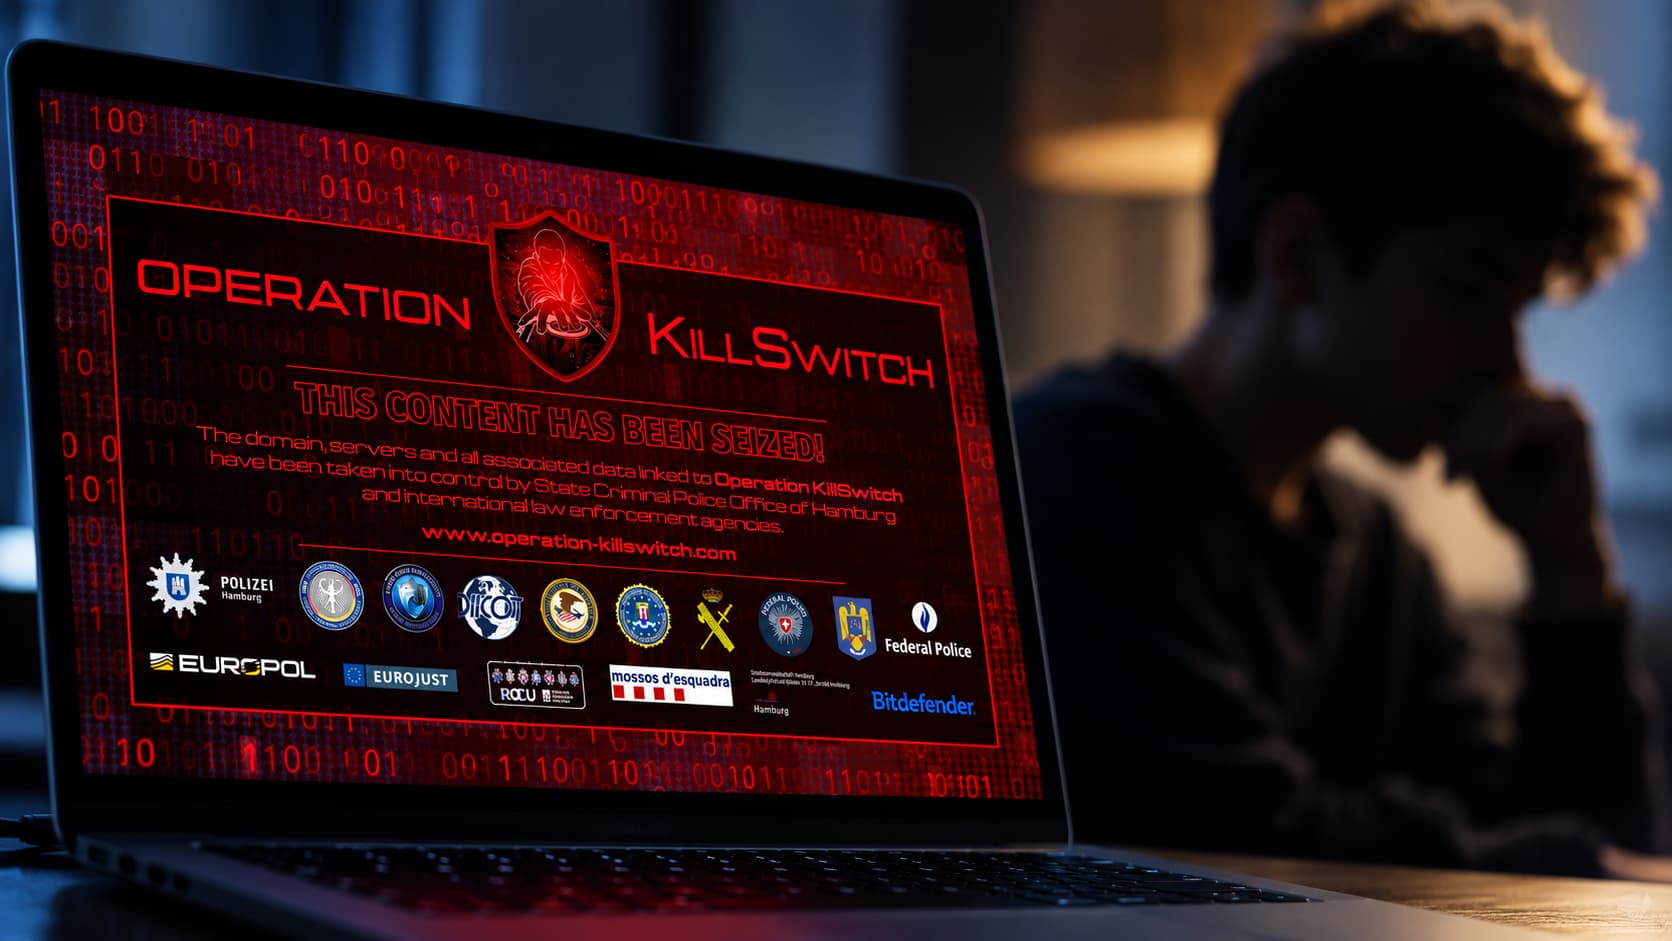
An international police operation announced today has effectively dismantled the KillSec ransomware syndicate, resulting in the arrest of three individuals and the seizure of five of the group’s servers.
KillSec, which emerged in the early 2020s, was known for encrypting victim data and demanding payment in cryptocurrency. The gang targeted a range of sectors, from small businesses to municipal services, leveraging sophisticated phishing campaigns and exploit kits to gain initial access.
Law‑enforcement agencies from several jurisdictions collaborated on the raid, tracing digital footprints across multiple command‑and‑control servers. The coordinated effort culminated in the confiscation of five servers that were believed to host the ransomware’s encryption tools and negotiation portals.
Among those taken into custody is a 16‑year‑old identified as a suspected administrator of the network. The teenager’s involvement highlights a growing trend of younger individuals participating in cyber‑crime, often attracted by the lucrative payouts associated with ransomware attacks. Legal experts note that the case will likely test how juvenile offenders are treated under cyber‑crime statutes.
Authorities say the disruption will temporarily impede KillSec’s ability to launch new attacks, offering relief to organizations that have been targeted in recent months. Victims may also benefit from the potential recovery of decryption keys stored on the seized servers, though officials caution that full remediation will take time.
The takedown follows a series of high‑profile ransomware busts worldwide, reflecting intensified global cooperation against cyber extortion. Agencies such as Europol, the FBI, and national cyber‑crime units have increasingly shared intelligence to trace illicit cryptocurrency flows and identify hidden infrastructure.
Investigators indicate that the operation is part of a broader campaign to dismantle ransomware ecosystems. Further arrests are anticipated as analysts continue to map the network of affiliates and money‑laundering channels linked to KillSec. The case also underscores the importance of robust cybersecurity hygiene for organizations seeking to defend against evolving ransomware threats.


Comments (0)
Be the first to comment.
Join the discussion