iRhythm alerts states to summer breach affecting hundreds of thousands of patients
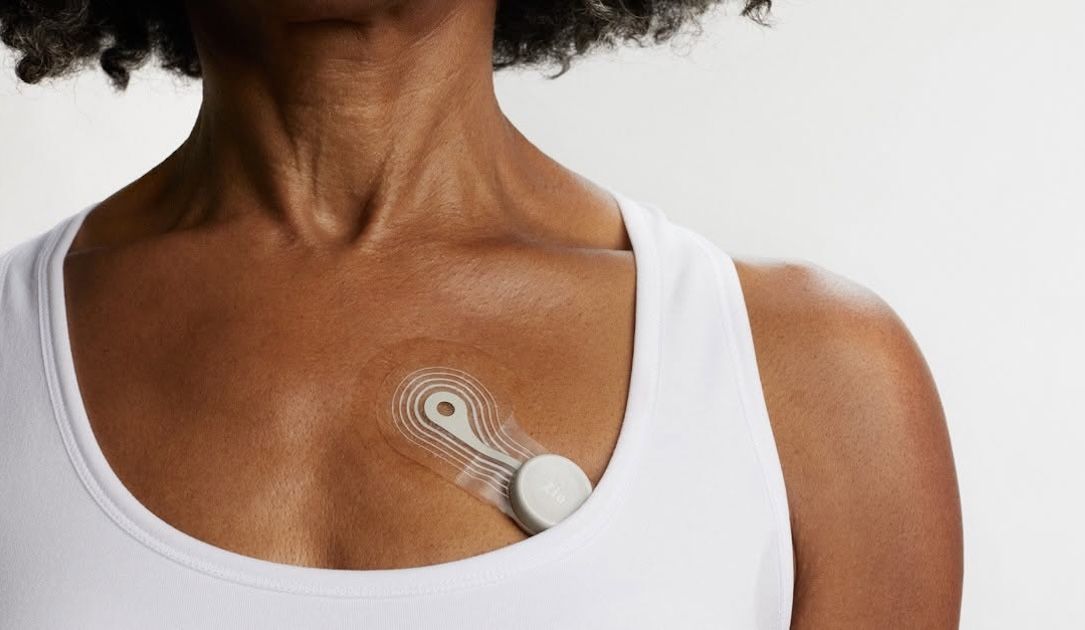
iRhythm, a company that produces wearable cardiac monitoring devices, has begun notifying state regulators that a cyber intrusion during the summer exposed the personal health information of hundreds of thousands of individuals.
The firm, best known for its long‑term ECG patch technology used to diagnose arrhythmias, collects detailed medical data from patients who wear the sensors for up to two weeks. That information is transmitted to iRhythm’s cloud platform for analysis by clinicians.
According to the notification, the breach involved data typically gathered for cardiac monitoring, including electrocardiogram recordings, demographic details and contact information. While the exact scope of the compromised files has not been disclosed, the company indicated that the breach could affect a sizable portion of its user base.
In compliance with U.S. health‑privacy law, iRhythm is informing state health departments and is expected to file breach notices with the Department of Health and Human Services. Regulators may launch investigations to determine whether the incident violated HIPAA security standards.
The company said it is working with cybersecurity experts to assess the incident, strengthen its defenses, and provide assistance to affected individuals. Patients who received the notice have been urged to monitor their accounts for any suspicious activity and to consider steps such as changing passwords or enrolling in identity‑theft protection services.
The episode highlights a growing trend of cyberattacks targeting health‑technology firms, where large volumes of sensitive biometric data are stored online. Industry analysts warn that as remote monitoring expands, firms must prioritize robust encryption and rapid response protocols to safeguard patient privacy and maintain trust.

Comments (0)
Be the first to comment.
Join the discussion