Supply‑Chain Intrusions Hijack Trusted Updates to Harvest Credentials
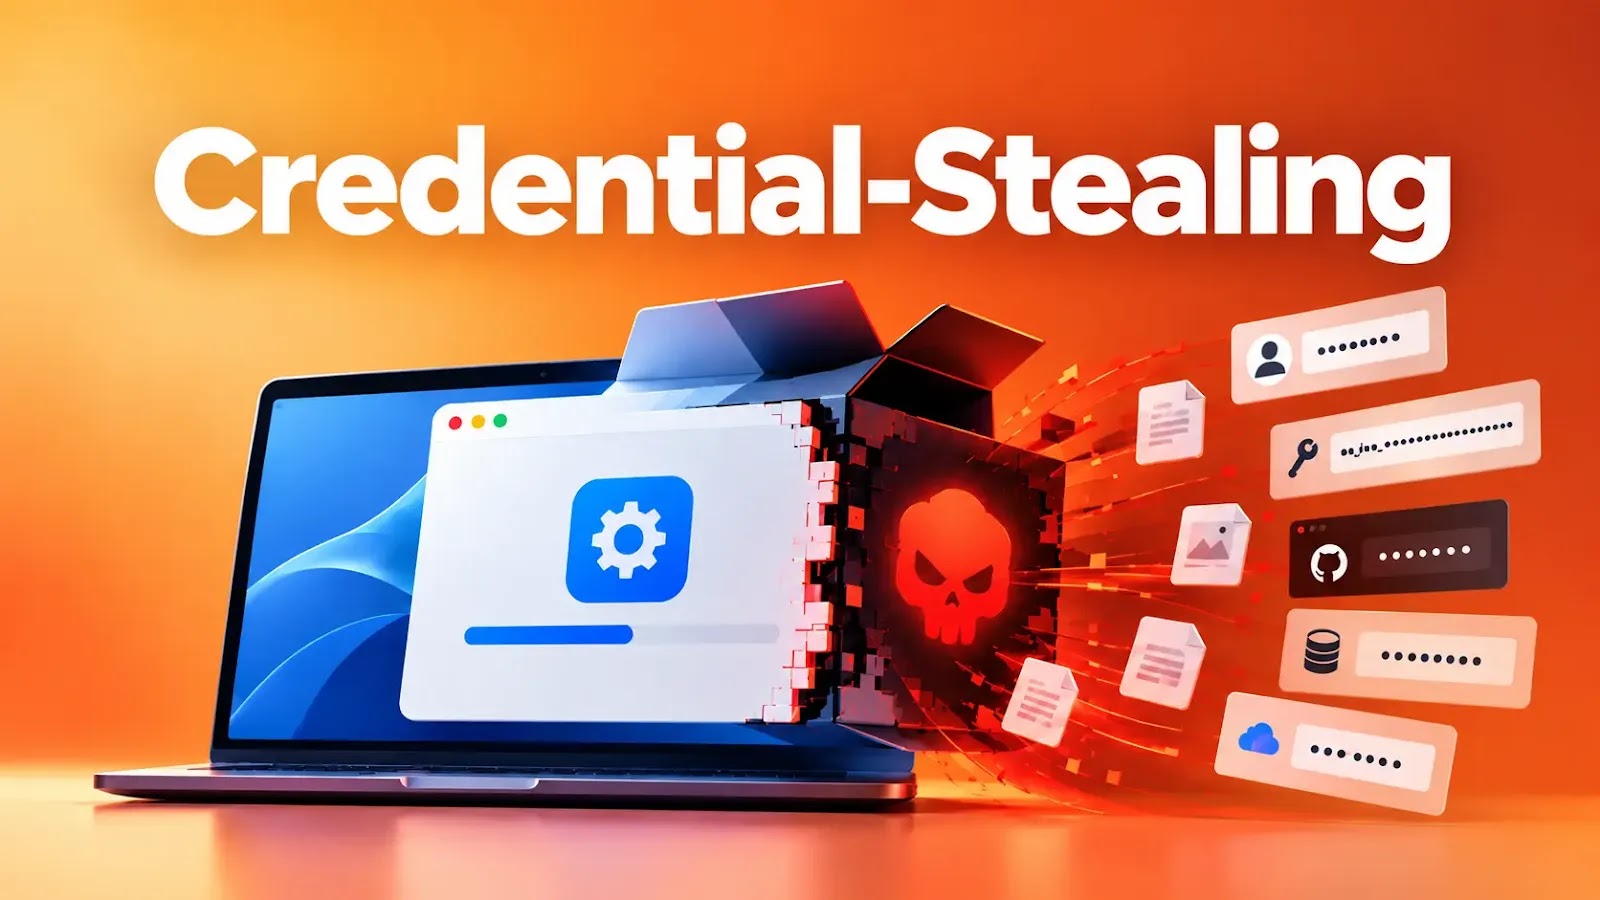
Security researchers have documented a surge in supply‑chain attacks that weaponize legitimate software updates, injecting credential‑stealing code into widely used open‑source packages.
In the latest cases, attackers compromised the source repositories of popular development tools, repackaged the software with malicious payloads, and pushed the tainted versions through the same distribution channels that developers trust for routine upgrades.
The strategy flips the traditional notion of update mechanisms as a defensive shield. By exploiting the trust placed in package managers and official release pipelines, threat actors can deliver malware directly to both individual programmers and the enterprises that rely on those tools, often without raising immediate suspicion.
Analysts note that the compromised packages are typically small utilities that integrate into larger build processes. Once installed, the hidden components harvest authentication tokens, API keys, and other credentials stored on the host machine, then exfiltrate the data to command‑and‑control servers operated by the attackers.
These incidents underscore a broader trend in cybercrime: targeting the software supply chain to achieve scale and persistence. Open‑source ecosystems, while fostering rapid innovation, often lack the rigorous code‑signing and verification practices found in proprietary software, making them attractive vectors for malicious actors.
Experts advise organizations to adopt stricter validation of third‑party dependencies, implement reproducible builds, and monitor network traffic for anomalous credential‑related activity. As the community rallies to improve provenance tracking, the episode serves as a reminder that even routine updates can become a conduit for espionage if supply‑chain integrity is not rigorously defended.

Comments (0)
Be the first to comment.
Join the discussion