International Crackdown Dismantles Gootloader Botnet, Affects 25,000 Infected Machines
Law enforcement agencies across several countries announced a coordinated operation that has effectively crippled the Gootloader malware network, which had compromised an estimated 25,000 computers worldwide. The effort, led by the U.S. Department of Justice, resulted in the seizure of dozens of domain names and the takedown of more than 100 servers used to host the malicious code.
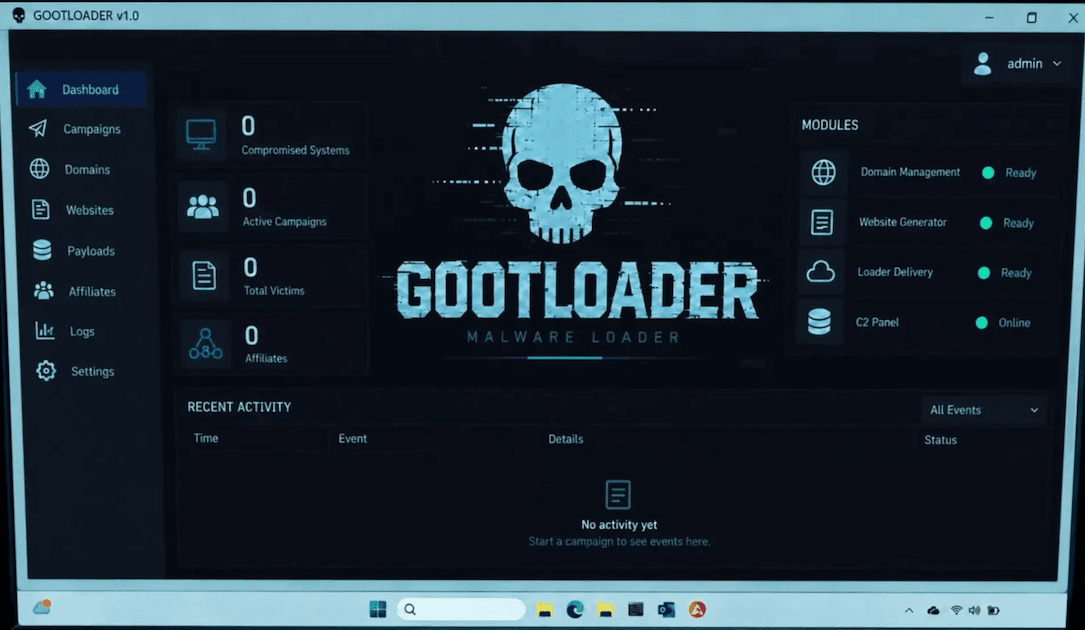
Gootloader, first identified by security researchers in 2020, functions as a downloader that delivers a range of ransomware and other malicious payloads to vulnerable systems. Its modular design and ability to evade detection made it a popular tool among cybercriminal groups seeking to monetize compromised devices through ransomware‑as‑a‑service arrangements.
The recent operation targeted the infrastructure that enabled the loader to reach victims. Investigators seized a series of domain registrations linked to the campaign and shut down over one hundred servers that were either directly hosting the loader or acting as command‑and‑control relays. According to the Justice Department, the removals have eliminated the active presence of Gootloader on those servers, cutting off a primary infection vector for the affected computers.
Authorities estimate that the disruption will impact roughly 25,000 compromised endpoints, many of which were part of corporate networks, educational institutions, and small businesses. While the seizure does not automatically cleanse infected devices, it removes the ability of the malware to receive updates or download additional payloads, substantially reducing the risk of further exploitation.
Cybersecurity experts note that the takedown underscores the importance of international collaboration in confronting transnational cybercrime. The operation involved coordination between U.S. agencies, European law‑enforcement partners, and private security firms that provided technical intelligence on the botnet’s architecture.
Officials cautioned that the removal of Gootloader’s infrastructure is a significant but not final step. Victims are urged to conduct thorough system scans, apply pending security patches, and monitor for any residual activity. The Justice Department indicated that ongoing investigations will continue to pursue the individuals behind the operation, with additional indictments expected as evidence is further analyzed.


Comments (0)
Be the first to comment.
Join the discussion