Hackers' Staging Server Exposes SQL Attack Kit Tied to Viva Aerobus Network
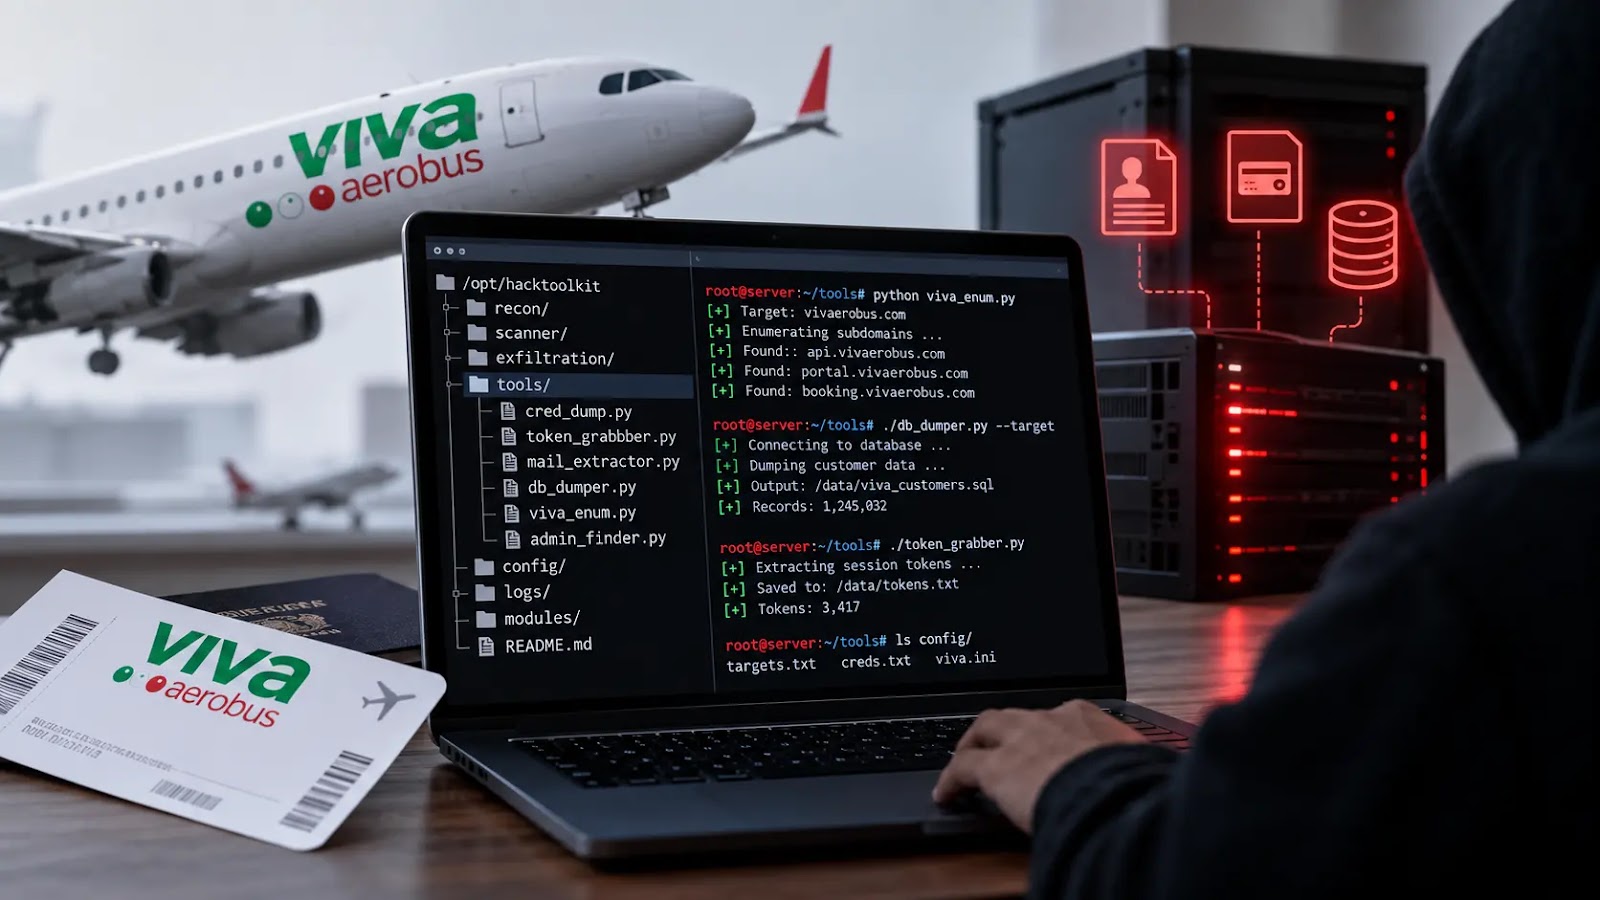
Security analysts have traced a publicly accessible server at the IP address 151.243.232.123 to a sophisticated intrusion campaign that targeted systems associated with the Mexican low‑cost carrier Viva Aerobus. The server, which was inadvertently left exposed on the internet, functioned both as a delivery point for malicious tools and as a repository for data exfiltrated from compromised databases.
Investigators discovered that the compromised infrastructure was centered on a Microsoft SQL Server exploit kit. The toolkit, stored on the staging server, contained scripts and binaries designed to gain privileged access to SQL instances, extract sensitive tables, and establish persistence within the victim environment. By using the exposed server as a drop site, the attackers could quickly update their payloads and retrieve stolen data without alerting defenders.
Microsoft SQL Server remains a frequent target for cybercriminals because it often houses critical business information such as customer records, financial transactions, and operational logs. The kit observed on the server leveraged known vulnerabilities in outdated SQL configurations, combined with custom scripts that automated privilege escalation and data dumping. Once the attackers secured a foothold, they could move laterally across the airline’s network, potentially accessing reservation systems, employee credentials, and other proprietary assets.
Viva Aerobus, which operates an extensive domestic and international route network, has previously been mentioned in cybersecurity briefings as part of broader supply‑chain concerns affecting the aviation sector. While the airline has not publicly confirmed a breach, the linkage of the staging server to a “Viva Aerobus‑side environment” suggests that at least one of its partners or internal systems was used as a foothold. Aviation companies are increasingly scrutinized for their cyber hygiene, given the sector’s reliance on complex IT ecosystems and the high stakes of service disruption.
The exposure of the attacker’s staging server provides a rare glimpse into the operational workflow of a targeted intrusion. Researchers recommend that organizations review their exposure on public IP ranges, enforce strict patching cycles for SQL Server installations, and employ network segmentation to limit the blast radius of a compromised database. Law enforcement and industry information‑sharing groups have been alerted, and further forensic analysis is expected to determine the full extent of any data loss and to identify additional compromised assets.

Comments (0)
Be the first to comment.
Join the discussion