European Police Dismantle KillSec Ransomware Service, Detain Teen Suspected Leader
Law enforcement agencies across Europe announced this week that they have effectively shut down the KillSec ransomware‑as‑a‑service operation and taken into custody a teenager believed to have headed the criminal network.
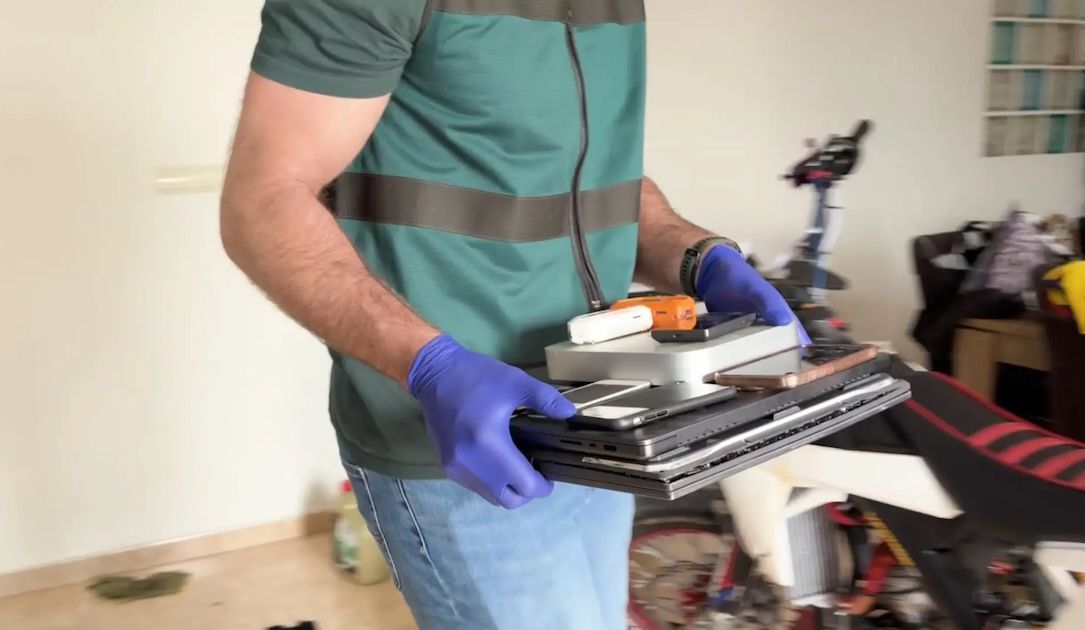
The coordinated raids, carried out in multiple EU member states, targeted the digital infrastructure that supported the ransomware platform, including command‑and‑control servers and cryptocurrency wallets used to collect payments from victims.
KillSec, which emerged in the cyber‑crime landscape a few years ago, offered malicious actors a ready‑made toolkit to encrypt data on compromised computers and demand ransom in cryptocurrency. The service operated on a subscription model, allowing affiliates to launch attacks while the operators collected a share of the proceeds.
Authorities highlighted the youth of the alleged leader as a sign of the growing involvement of teenage hackers in sophisticated cyber‑crime enterprises. While the exact age was not disclosed, investigators said the suspect demonstrated a high level of technical skill and an ability to manage a transnational illicit business.
Victims of KillSec have reported loss of access to critical files, disruption of business operations, and costly recovery efforts. By dismantling the service, police aim to reduce the immediate threat to organizations that have been targeted and to send a deterrent signal to other ransomware operators.
Officials indicated that the investigation remains ongoing, with additional arrests possible as the network’s broader connections are examined. The case underscores a renewed focus by European authorities on dismantling ransomware‑as‑a‑service ecosystems, which they view as a major security challenge for both private and public sectors.


Comments (0)
Be the first to comment.
Join the discussion