Warlock Ransomware Leverages Old SharePoint Bugs to Target Global Critical Services
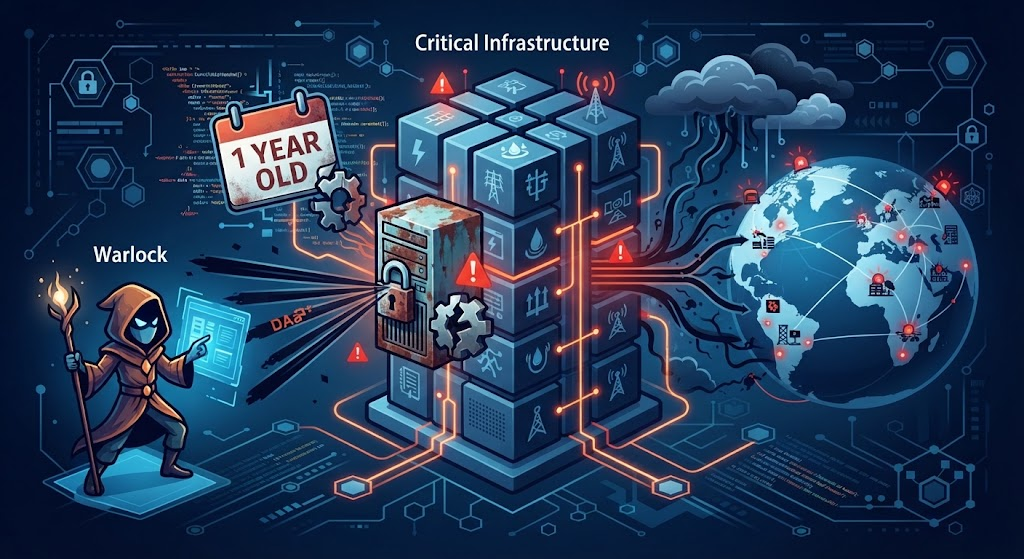
Warlock ransomware has resurfaced as a persistent threat, exploiting vulnerabilities in Microsoft SharePoint that have been publicly known for more than a year. Security researchers report that the malware continues to infiltrate water utilities, telecommunications firms, government agencies, and higher‑education institutions across several continents, underscoring the danger of unpatched legacy flaws in widely deployed software.
The attack chain relies on a set of SharePoint zero‑day exploits collectively labeled "ToolShell" when they first emerged in mid‑2025. Those exploits grant attackers low‑level access to SharePoint servers, which they then use to drop the Warlock payload. Although Microsoft issued patches for the underlying flaws shortly after their disclosure, the ransomware operators have adapted their tools to target systems that remain unpatched, effectively recycling the same vulnerability chain.
Victims reported in recent weeks include a municipal water provider in the United States, a regional telecom carrier in Europe, a provincial government office in Asia, and a university research network in South America. In each case, the attackers leveraged the SharePoint breach to move laterally within the network, encrypting data and demanding payment in cryptocurrency. The incidents have forced service disruptions, raised concerns about the integrity of essential public services, and highlighted the interconnected nature of modern IT environments.
Analysts attribute the continued success of Warlock to a combination of factors: the sheer number of SharePoint installations worldwide, the difficulty many organizations face in applying patches promptly, and the low cost of reusing an existing exploit kit. Legacy systems, limited staffing, and the operational risk of downtime during updates often lead administrators to defer critical security updates, creating a fertile ground for ransomware groups that specialize in low‑effort, high‑impact intrusions.
Microsoft has reiterated the importance of applying the latest SharePoint updates and has issued additional hardening guidance for organizations that cannot immediately upgrade. Security firms are also urging entities to conduct thorough inventory checks, segment network traffic, and implement multi‑factor authentication for administrative accounts. The renewed activity of Warlock serves as a reminder that the threat landscape evolves not only through new vulnerabilities but also through the exploitation of known weaknesses that remain unaddressed.
Going forward, experts expect ransomware operators to continue scanning for unpatched SharePoint instances, especially as supply‑chain attacks and automated scanning tools become more sophisticated. Stakeholders are advised to prioritize patch management, adopt zero‑trust principles, and maintain regular backups isolated from production networks. While no single solution can eliminate the risk, coordinated effort between software vendors, cybersecurity teams, and policy makers will be essential to curb the resurgence of threats that thrive on outdated software.


Comments (0)
Be the first to comment.
Join the discussion