US Takes Down Chinese APT Tools Targeting Critical Infrastructure
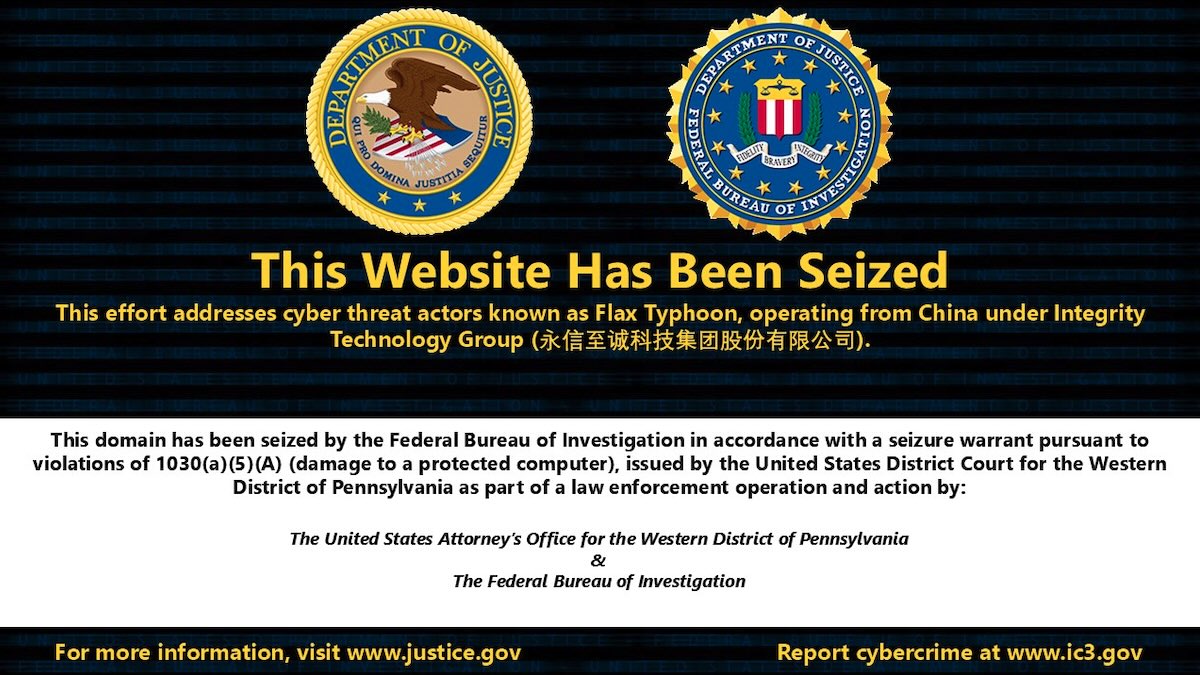
The United States government announced this week that it has successfully disrupted a suite of hacking utilities linked to Chinese state-sponsored actors, halting their use against both domestic and foreign critical infrastructure.
According to the report, the tools—identified as MicroScan and FishHub—were employed by the advanced persistent threat (APT) group known as Flax Typhoon, among others, to conduct reconnaissance and gain unauthorized access to networks that support utilities, transportation, and other essential services. The intrusion attempts were detected across a range of sectors, prompting a coordinated response from U.S. cyber‑defense agencies.
Cybersecurity analysts say the discovery underscores a broader pattern of Chinese cyber operations that focus on stealthy, long‑term infiltration of high‑value targets. While the specific technical details of the disruption remain classified, officials indicated that the takedown involved disabling command‑and‑control servers and issuing remediation guidance to affected organizations.
The move follows a series of high‑profile incidents attributed to Chinese APT groups over the past few years, including the 2020 SolarWinds supply‑chain breach and multiple campaigns aimed at telecommunications and energy firms. By neutralizing the tools used in these latest attacks, U.S. authorities hope to raise the cost and complexity for adversaries seeking to exploit similar pathways.
Industry stakeholders have been urged to review their security postures, apply recommended patches, and conduct thorough audits of network segments that may have been scanned by MicroScan. The Department of Homeland Security’s Cybersecurity and Infrastructure Security Agency (CISA) is expected to release further advisories to help organizations detect remnants of the compromised software.
Experts caution that while the immediate threat has been mitigated, the underlying geopolitical tension driving state‑backed cyber activity is unlikely to wane. Continued vigilance, public‑private collaboration, and investment in threat‑intelligence sharing will be essential to defend critical infrastructure from future incursions.


Comments (0)
Be the first to comment.
Join the discussion