U.S. Offers $10 Million Reward for Leads on Chinese Hacker Linked to Hafnium Breach
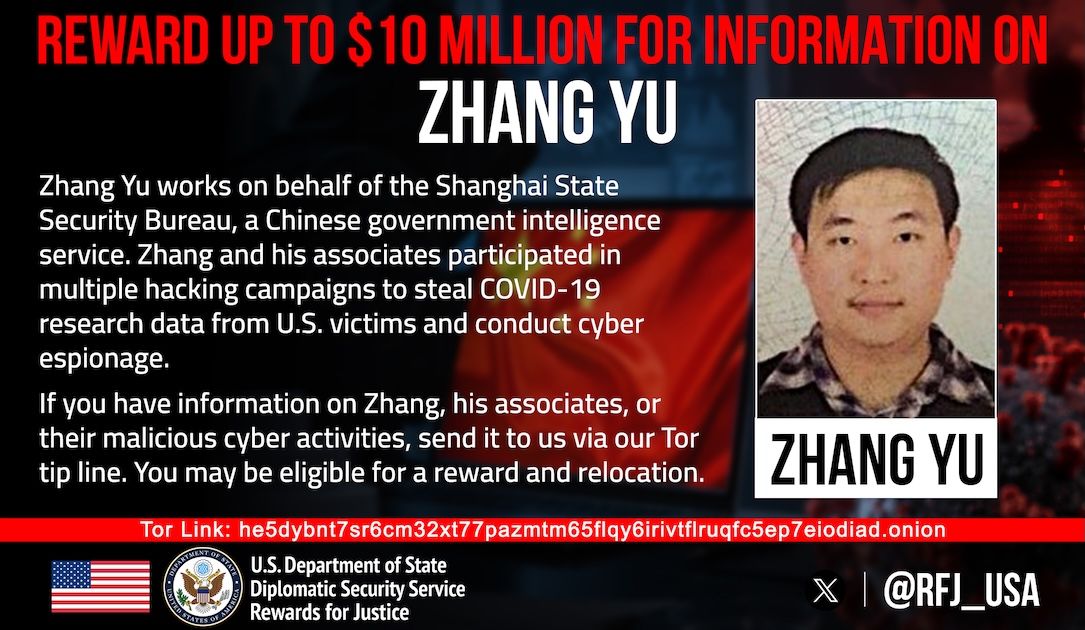
The United States announced a $10 million bounty for information that could lead to the arrest or conviction of Zhang Yu, a Chinese national identified by officials as a senior operative in the Hafnium cyber‑espionage campaign.
According to the Justice Department, Zhang is alleged to have played a pivotal role in planning and executing the attacks that compromised tens of thousands of computers worldwide. The reward reflects the government's determination to hold accountable individuals who facilitate large‑scale intrusion operations.
Hafnium, a group widely believed to be backed by the Chinese government, exploited vulnerabilities in Microsoft Exchange Server in early 2021. The breach gave attackers remote access to email systems, allowing them to exfiltrate sensitive documents, intellectual property, and personal data from a broad spectrum of entities, including corporations, universities and local governments.
The fallout from the Exchange exploit was significant: organizations reported operational disruptions, costly remediation efforts, and heightened concerns over supply‑chain security. While the exact volume of stolen material remains classified, officials have described the haul as “substantial,” underscoring the campaign’s reach and the strategic value of the information obtained.
Offering a monetary reward is part of a broader strategy to deter state‑sponsored hacking and to encourage whistleblowers or insiders to come forward. Similar incentives have been used in past cases involving ransomware operators and other foreign intelligence services, signaling that the U.S. will employ financial inducements alongside diplomatic pressure.
Law‑enforcement agencies say the bounty will remain open until a credible lead results in a prosecution. The announcement also serves as a reminder to private sector entities of the importance of patching critical software and maintaining robust cyber‑hygiene, especially as nation‑state actors continue to target widely deployed platforms.


Comments (0)
Be the first to comment.
Join the discussion