U.S. Agencies Issue Advisory to Secure Refrigeration Controllers After European Cyberattacks
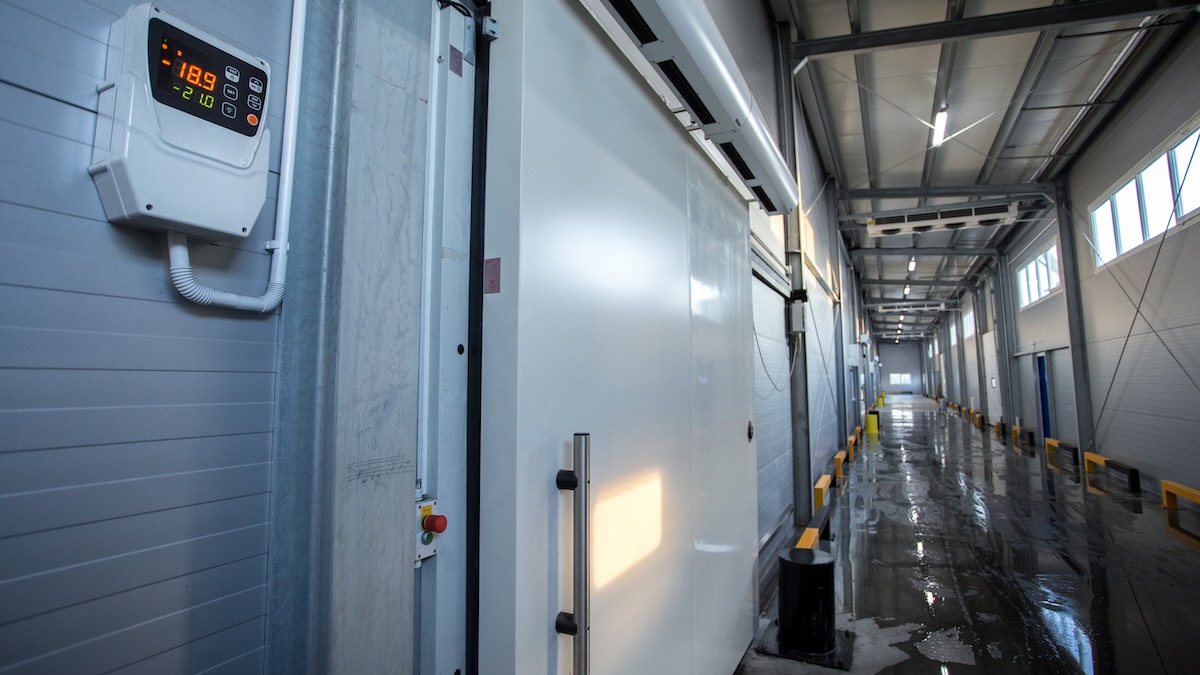
U.S. agencies have issued a new advisory urging businesses and healthcare providers to strengthen the security of refrigeration controllers following a series of cyberattacks in Europe that targeted supermarket freezers and blood‑bank chillers.
The attacks, reported earlier this year, involved threat actors gaining remote access to the programmable logic controllers that regulate temperature, allowing them to change set points or shut systems down. In several cases the incidents led to loss of perishable food and compromised the integrity of stored blood products, raising public‑health concerns.
Officials say the same technical weaknesses are present in many American facilities that rely on comparable off‑the‑shelf controllers, many of which were not built with strong authentication or encryption. The advisory notes that the tools used in the European incidents are widely available on underground forums, indicating that the risk is not confined to a single nation‑state or criminal group.
Key recommendations include applying vendor security patches promptly, isolating refrigeration networks from corporate IT environments, enforcing strong passwords or multi‑factor authentication for remote access, and deploying continuous monitoring to flag anomalous commands. Agencies also advise organizations to conduct risk assessments that map critical refrigeration assets and evaluate the potential impact of a compromise.
The guidance is part of a broader effort by U.S. authorities to harden industrial control systems that support essential services such as food supply chains, healthcare and energy. In recent years, ransomware and sabotage campaigns have increasingly targeted operational technology, prompting regulators to roll out sector‑specific security frameworks.
Analysts expect the advisory will prompt many retailers, hospitals and logistics firms to review their control‑system architectures. Coordination with European counterparts is likely to increase, as the cross‑border nature of supply‑chain equipment means a vulnerability exploited abroad can quickly become a domestic risk. Organizations that delay remediation may face regulatory scrutiny or liability if a breach leads to product spoilage or patient harm.
The advisory also signals that Congress may consider legislation requiring mandatory cybersecurity standards for commercial refrigeration equipment. Potential measures could mandate baseline security features such as signed firmware and regular vulnerability disclosures, mirroring requirements already in place for medical devices and critical infrastructure.



Comments (0)
Be the first to comment.
Join the discussion