UK Moves to Service‑Centred Cyber Governance After Audit Uncovers Strategy Shortfalls
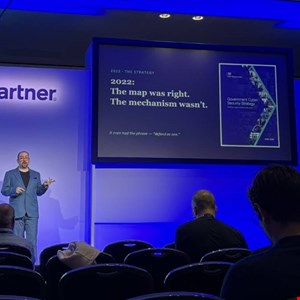
Whitehall announced a major pivot in its cyber‑security oversight, replacing the previously mandated control framework with a service‑led governance model. The change follows a scathing audit that highlighted systemic gaps in the government's 2022 cyber strategy, prompting senior officials to rethink how digital risk is managed across departments.
The audit, released earlier this month, detailed a series of implementation failures, including inconsistent application of security standards, inadequate monitoring of third‑party services, and a lack of clear accountability for cyber incidents. Analysts said the findings underscored the limitations of a one‑size‑fits‑all control regime, which had struggled to keep pace with the rapid evolution of threats and the growing reliance on cloud‑based services.
In response, the Cabinet Office outlined a new approach that treats cyber‑security as an integral service offered to all government bodies rather than a set of prescriptive rules. Under the service‑led model, specialised cyber teams will provide guidance, tools, and continuous monitoring to ministries and agencies, allowing them to focus on mission‑critical functions while benefiting from consistent expertise and shared resources.
Officials emphasized that the shift does not abandon standards altogether; instead, it embeds them within the service delivery process. By centralising capabilities such as threat intelligence, incident response, and vulnerability management, the government aims to achieve faster remediation times and more uniform protection across the public sector.
Experts note that the move aligns with broader trends in both the private and public sectors, where organisations increasingly adopt managed security services to address talent shortages and the complexity of modern attack vectors. However, they caution that success will depend on clear governance structures, transparent reporting, and sustained investment in the underlying service platforms.
The upcoming months will see the rollout of pilot programs in selected departments, with performance metrics to be reviewed by an independent oversight board. If the service‑led model proves effective, it could become the template for future cyber policy, marking a decisive step away from the fragmented, control‑centric approach that previously defined the UK's digital defence posture.



Comments (0)
Be the first to comment.
Join the discussion