TIKTOUK Toolkit Enables Automated Theft of WordPress‑Linked Cloud and Email Credentials
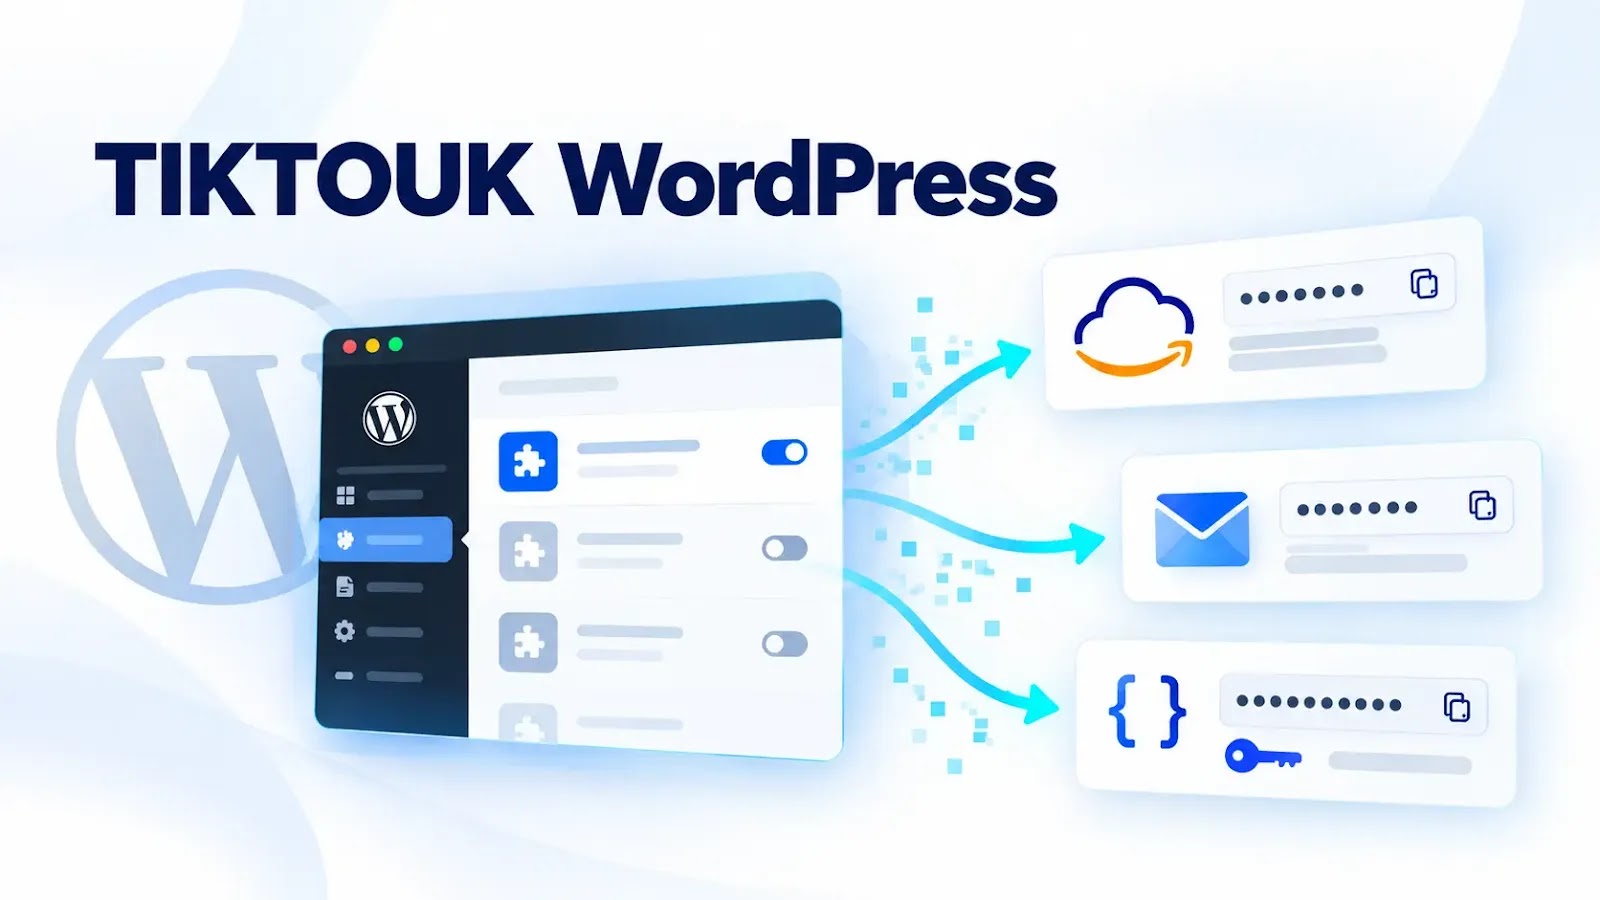
Security researchers have identified a new open‑source toolkit, dubbed TIKTOUK, that streamlines the collection of AWS, SMTP and other API credentials from vulnerable WordPress installations. The package combines reconnaissance, file harvesting, decryption of stored plugin passwords and JavaScript secret scanning into a single automated workflow, raising concerns for administrators of both small blogs and larger commercial sites.
The toolkit is comprised of two Python scripts—wp2s_poll.py and wp2s_crack.py—paired with a lightweight Go binary stripped of non‑essential components. The polling script scans the internet for WordPress sites, gathers publicly exposed files such as wp‑config.php, and enumerates installed plugins. The cracking script then attempts to decrypt credentials stored by popular plugins, while the Go component parses client‑side JavaScript for hard‑coded keys.
By chaining these steps, TIKTOUK can move from simple site discovery to the extraction of high‑value secrets without manual intervention. It first identifies sites with misconfigured servers that expose configuration files, then leverages known weaknesses in plugin encryption routines to reveal database passwords, API tokens and SMTP login data. Finally, the JavaScript scanner looks for embedded keys used by third‑party services, turning a compromised site into a gateway for broader network infiltration.
The implications are significant because the harvested credentials often grant direct access to cloud resources, email gateways and other services that organizations rely on for daily operations. An attacker who obtains an AWS access key, for example, can spin up instances, exfiltrate data or incur costly usage charges. Similarly, SMTP credentials enable phishing campaigns or spam distribution that can damage a brand’s reputation.
Experts advise site owners to harden WordPress deployments as a first line of defense. This includes keeping the core software, themes and plugins up to date, disabling directory listings, restricting access to configuration files via proper server permissions, and employing secret‑management solutions that avoid storing credentials in plain text. Monitoring for unusual API calls or outbound traffic from newly created cloud resources can also help detect exploitation attempts.
The emergence of TIKTOUK reflects a broader trend toward modular, automated weaponization of common web platforms. As attackers continue to package multiple reconnaissance and exploitation techniques into single tools, defenders must adopt equally integrated security practices, combining vulnerability scanning, file integrity monitoring and threat‑intel feeds to stay ahead of evolving threats.
Comments (0)
Be the first to comment.
Join the discussion