Beyond the Ransom: How Business Continuity Plans Cut the True Cost of Cyber Extortion
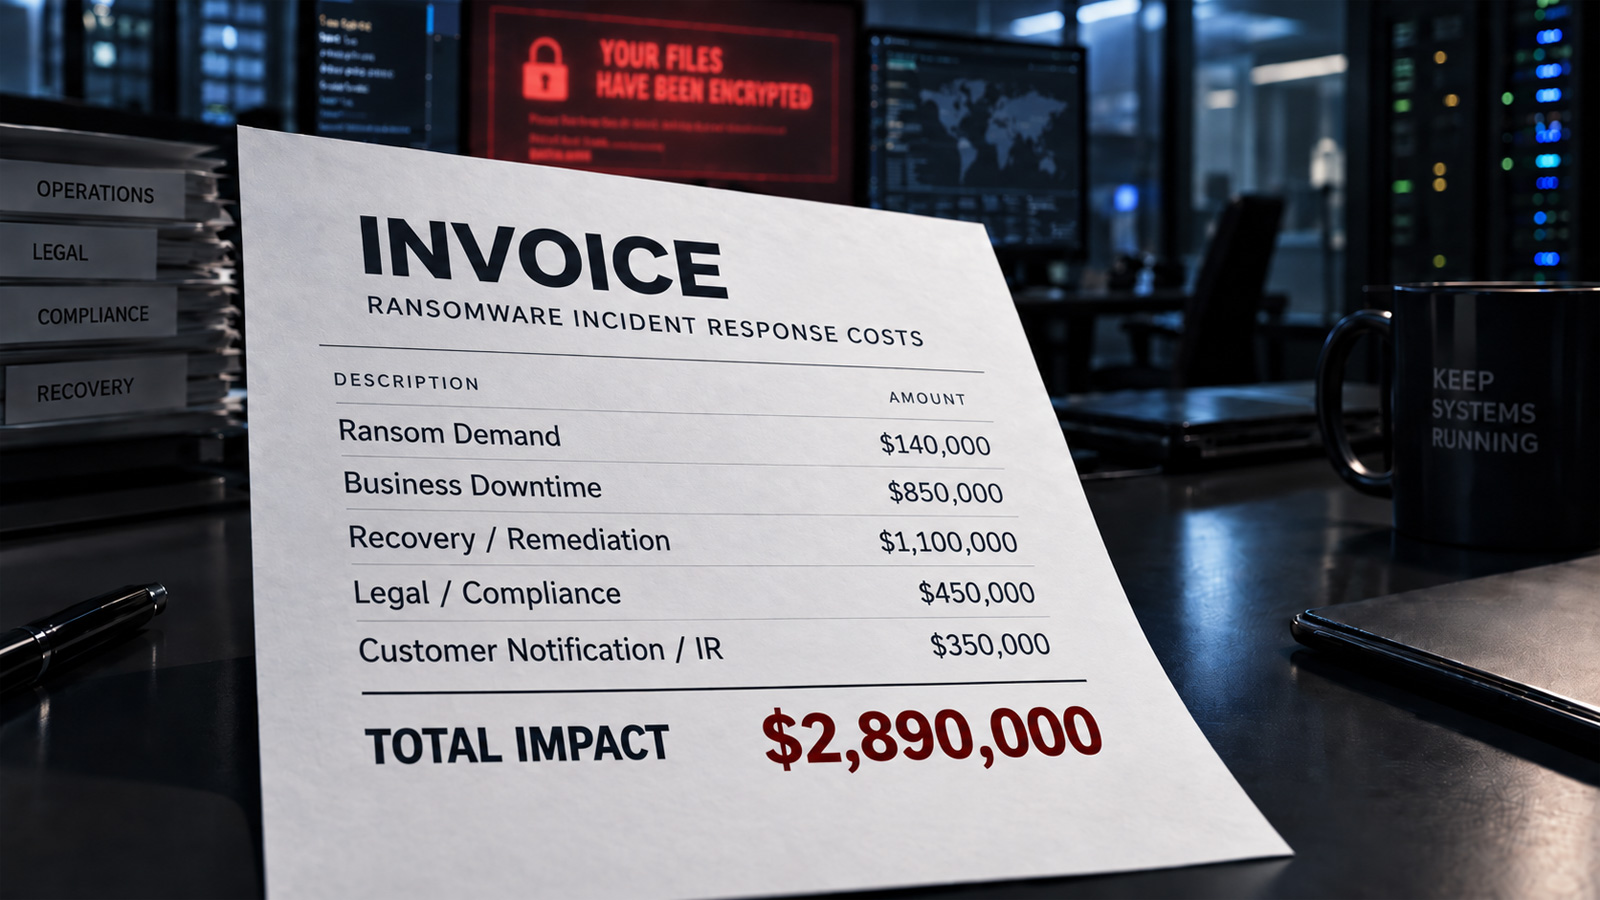
When a ransomware group breaches a network, the headline‑grabbing payment often represents only a small slice of the overall financial hit. Companies that fall victim must also grapple with extended downtime, costly data recovery efforts, remediation of compromised systems, and a suite of legal and regulatory obligations that can push the total bill into the millions.
Industry analysts note that the direct ransom demand may be a few hundred thousand dollars, but the indirect costs—lost revenue while systems are offline, expenses for forensic investigations, and the need to rebuild or replace affected infrastructure—frequently dwarf the headline figure. In many cases, the downtime alone can erode profit margins, especially for businesses that rely on continuous access to digital services.
Datto, a provider of backup and disaster‑recovery solutions, argues that a mature Business Continuity and Disaster Recovery (BCDR) strategy can dramatically curtail these hidden expenses. By maintaining up‑to‑date, immutable backups and automating failover to standby environments, organizations can restore operations in hours rather than days, limiting revenue loss and reducing the pressure to negotiate with attackers.
The benefits of a robust BCDR plan extend beyond speed. Predictable recovery timelines give executives clearer insight into financial exposure, allowing them to allocate resources more efficiently and meet compliance requirements tied to data protection laws. Moreover, having a tested restoration process can mitigate legal risk, as regulators often scrutinize an organization’s preparedness and response to cyber incidents.
Experts caution that while BCDR can lower the total cost of a ransomware event, it is not a silver bullet. Companies must still invest in preventive measures such as employee training, patch management, and network segmentation to reduce the likelihood of an initial breach. As ransomware tactics evolve, the combination of proactive defenses and a resilient recovery framework will become increasingly essential for limiting the true, often hidden, price tag of cyber extortion.



Comments (0)
Be the first to comment.
Join the discussion