Linux Bot ‘Tengu’ Poses as Kernel Worker to Power DDoS and Proxy Networks
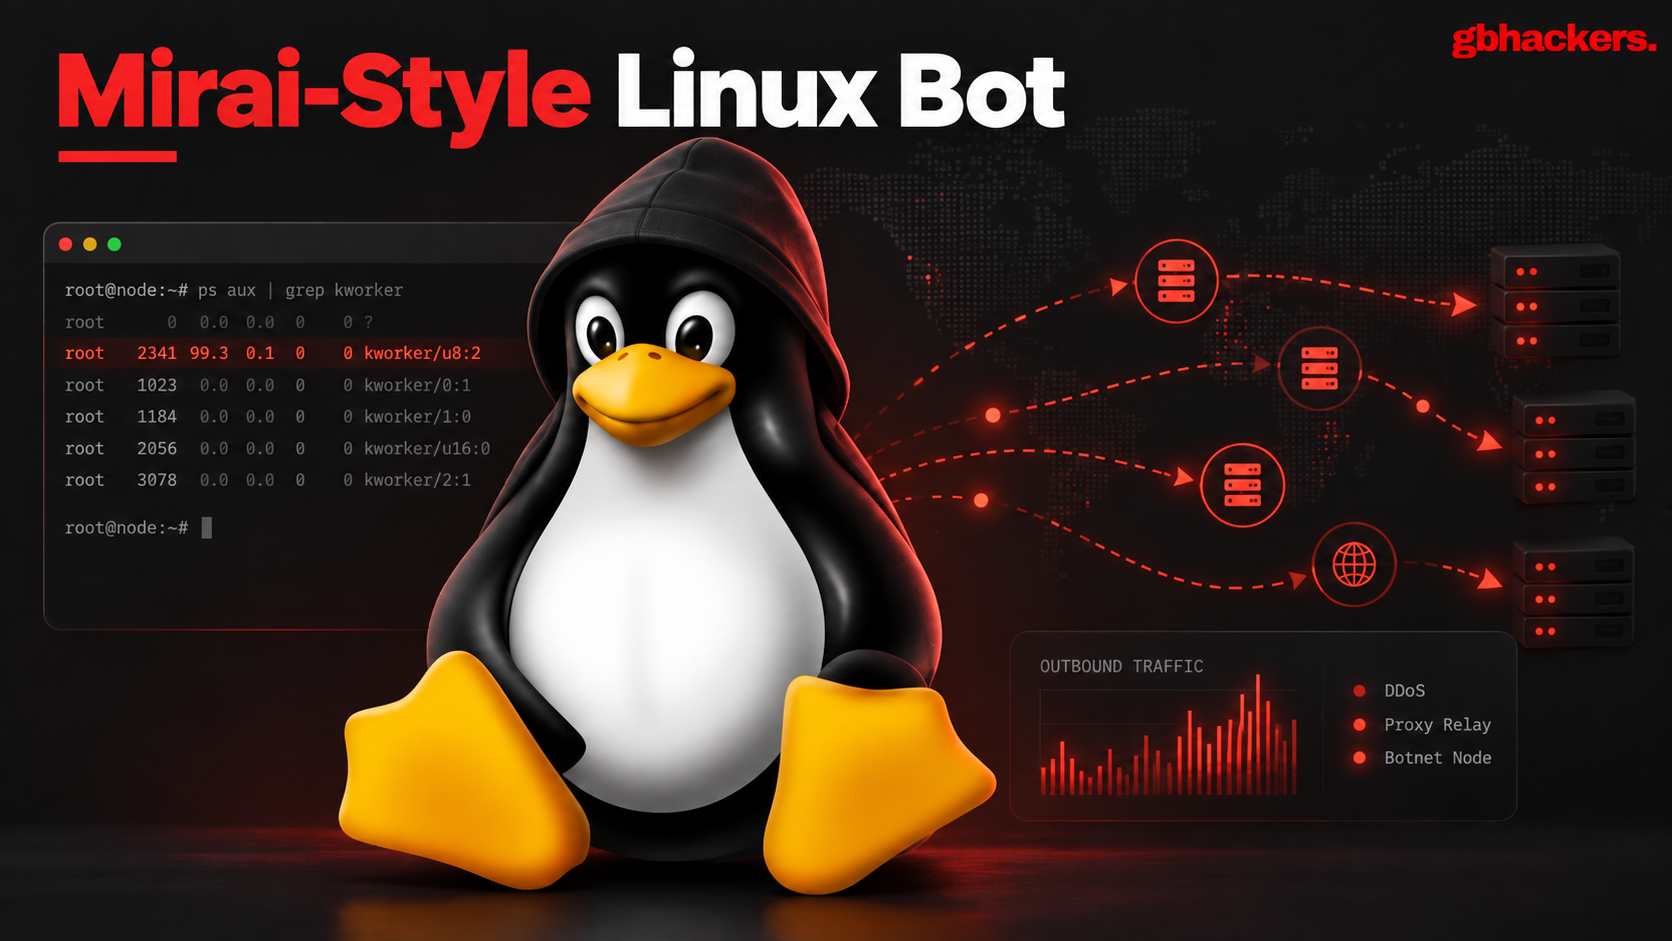
A new Linux malware strain identified as Tengu has been found masquerading as a legitimate kernel worker process while mounting large‑scale distributed denial‑of‑service (DDoS) attacks and operating as a proxy server. Security analysts say the 32‑bit ELF binary blends the familiar Mirai botnet approach with advanced persistence techniques, allowing it to remain hidden on compromised machines for extended periods.
The sample, first disclosed by the GBHackers research collective, targets a wide range of Linux‑based platforms, from cloud servers to embedded devices such as routers and IoT appliances. By presenting itself as a kernel worker, Tengu evades basic process‑monitoring tools, making detection difficult for administrators who rely on conventional signatures.
Beyond DDoS capabilities, the malware conducts systematic SSH probing, attempting to brute‑force login credentials on other hosts. Successful intrusions expand the botnet’s reach, while the built‑in proxy function enables attackers to route traffic through infected nodes, obscuring the origin of malicious activity and facilitating further exploitation.
Researchers note that Tengu’s persistence mechanisms are notably robust. The code embeds itself in multiple system locations, modifies startup scripts, and can reinstall itself if removed, mirroring tactics seen in more sophisticated Linux threats. Its reliance on open‑source tools and publicly available Mirai code suggests a hybrid development model that leverages existing botnet infrastructure while adding custom modules for stealth.
The emergence of Tengu underscores growing concerns about the security of Linux environments that were once considered relatively safe from mass‑infection campaigns. As enterprises increasingly deploy Linux containers and edge devices, the attack surface expands, providing adversaries with more footholds. Analysts recommend hardening SSH access, employing behavior‑based monitoring, and regularly auditing running processes for anomalies that could indicate kernel‑worker impersonation.
While the full impact of Tengu remains under investigation, its blend of Mirai‑style botnet tactics with deeper system integration signals a shift toward more versatile Linux threats. Ongoing collaboration between independent researchers and security firms will be critical to develop detection signatures and mitigation strategies before the botnet can be leveraged for larger, coordinated attacks.

Comments (0)
Be the first to comment.
Join the discussion