Critical TeamViewer Flaw Could Let Hackers Hijack Support Technicians' Machines
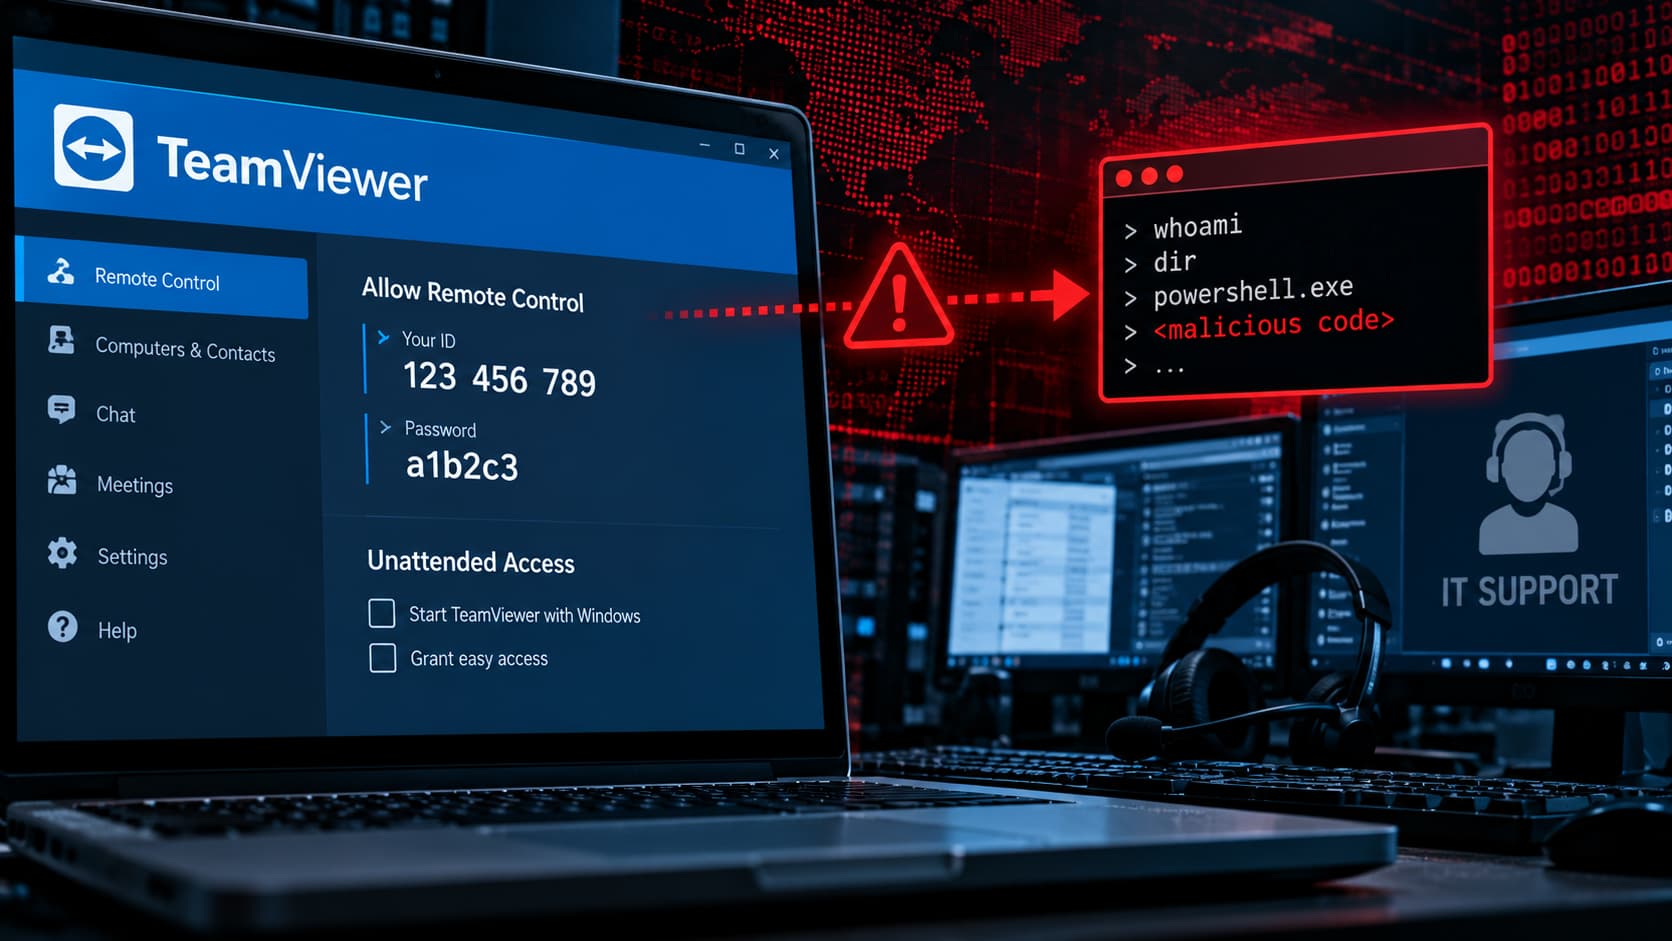
A newly disclosed vulnerability in the popular remote‑access program TeamViewer could enable threat actors to execute arbitrary code on the computers of IT support staff who use the tool to assist clients, security researchers warned.
The flaw stems from how TeamViewer handles incoming connection requests. By crafting a specially designed payload, an attacker can trick a support technician’s client into running malicious code without the need for the technician to click any link or download a file. Once the code runs, the attacker gains the same privileges as the support user, potentially allowing full control of the workstation and access to any network resources it can see.
Remote‑support applications like TeamViewer are widely deployed in corporate environments because they simplify troubleshooting across geographically dispersed locations. The convenience, however, also makes them attractive targets for exploitation. Security experts note that similar vulnerabilities have surfaced in other remote‑desktop solutions in the past, underscoring the importance of rigorous security reviews for software that bridges external networks and internal systems.
TeamViewer’s developers have acknowledged the issue and are preparing an out‑of‑band patch. In a statement, the company urged customers to apply the forthcoming update as soon as it becomes available and recommended that administrators enforce the principle of least privilege for support accounts. Until the patch is released, experts advise organizations to limit the use of unattended access, enable two‑factor authentication, and monitor logs for suspicious connection attempts.
The vulnerability was initially reported by the cybersecurity outlet Hackread, which provided technical details that allowed researchers to reproduce the exploit in a controlled environment. While no public incidents have been confirmed, the potential impact is significant given the tool’s prevalence in sectors ranging from finance to healthcare.
Analysts say the episode highlights a broader challenge: balancing ease of remote assistance with robust security controls. As remote work continues to expand, companies are urged to regularly audit the software they rely on, keep systems up to date, and train support personnel to recognize anomalous behavior during remote sessions.
TeamViewer is expected to release the security fix within the next few days. In the meantime, organizations are encouraged to review their remote‑support policies, restrict administrative rights where possible, and stay alert for any signs of exploitation linked to this newly disclosed weakness.


Comments (0)
Be the first to comment.
Join the discussion