Microsoft Disrupts Storm-3168 Campaign After Hackers Wreck Azure Environments
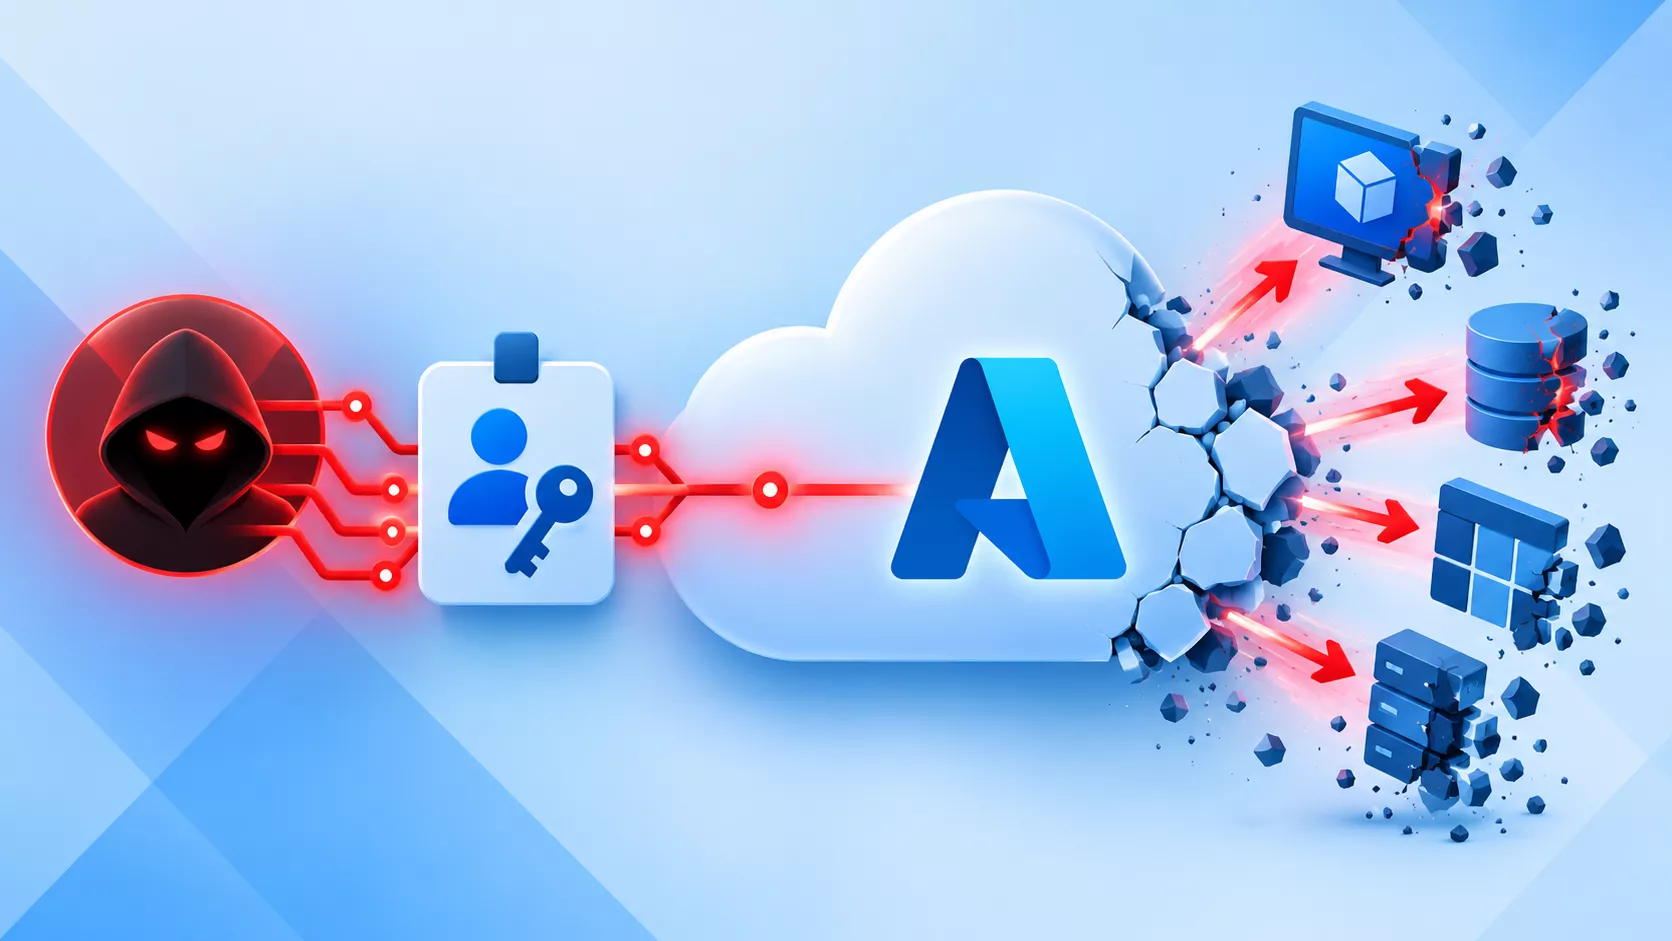
Microsoft announced on Tuesday that it has dismantled a sophisticated attack campaign targeting Azure customers, a operation that security researchers have labeled Storm-3168 or JADEPUFFER. The intrusion leveraged compromised Azure service principals—a type of identity used by applications and automation scripts—to gain a foothold inside victim clouds, systematically map resources, and then erase critical workloads.
According to the company, the threat actors first obtained service‑principal credentials through phishing or credential‑dumping techniques. Once in possession of these privileged identities, they could enumerate virtual machines, databases, and networking configurations across the tenant. The attackers then issued delete commands against key services, effectively rendering applications inoperable and forcing organizations to scramble for backups.
Beyond outright destruction, the group also pursued a secondary objective: undermining recovery mechanisms. By targeting snapshots, Azure Backup vaults, and other safeguard configurations, the perpetrators aimed to make data restoration more difficult, increasing the pressure on victims to pay ransoms or negotiate. In parallel, the actors harvested storage‑account keys, granting them read‑only access to blobs and files that could contain sensitive corporate information.
Microsoft’s internal security teams detected the malicious activity through anomalous API calls and unusual patterns of resource deletion. Rapid response actions included revoking the compromised service principals, restoring affected services from immutable snapshots, and issuing guidance to customers on tightening identity‑management practices. The company also shared indicators of compromise with the broader security community to help other organizations spot similar behavior.
The incident underscores a growing trend in cloud‑focused threat actors who prefer abusing legitimate identities rather than exploiting software vulnerabilities. Service principals, while essential for automation, often lack the same monitoring rigor applied to user accounts, making them attractive targets. Experts note that the rapid scalability of cloud platforms can amplify the impact of a single compromised credential, turning a localized breach into a widespread outage.
While Microsoft has not disclosed the number of affected customers, the agency warned that any organization running workloads on Azure should review its identity‑access policies, enforce least‑privilege principles, and enable multi‑factor authentication for service‑principal operations where possible. The incident also serves as a reminder that cloud security is a shared responsibility, requiring both provider safeguards and diligent tenant‑side governance to prevent similar campaigns from succeeding in the future.



Comments (0)
Be the first to comment.
Join the discussion