StealC Malware Re-emerges as Stadia RAT After Global Takedown
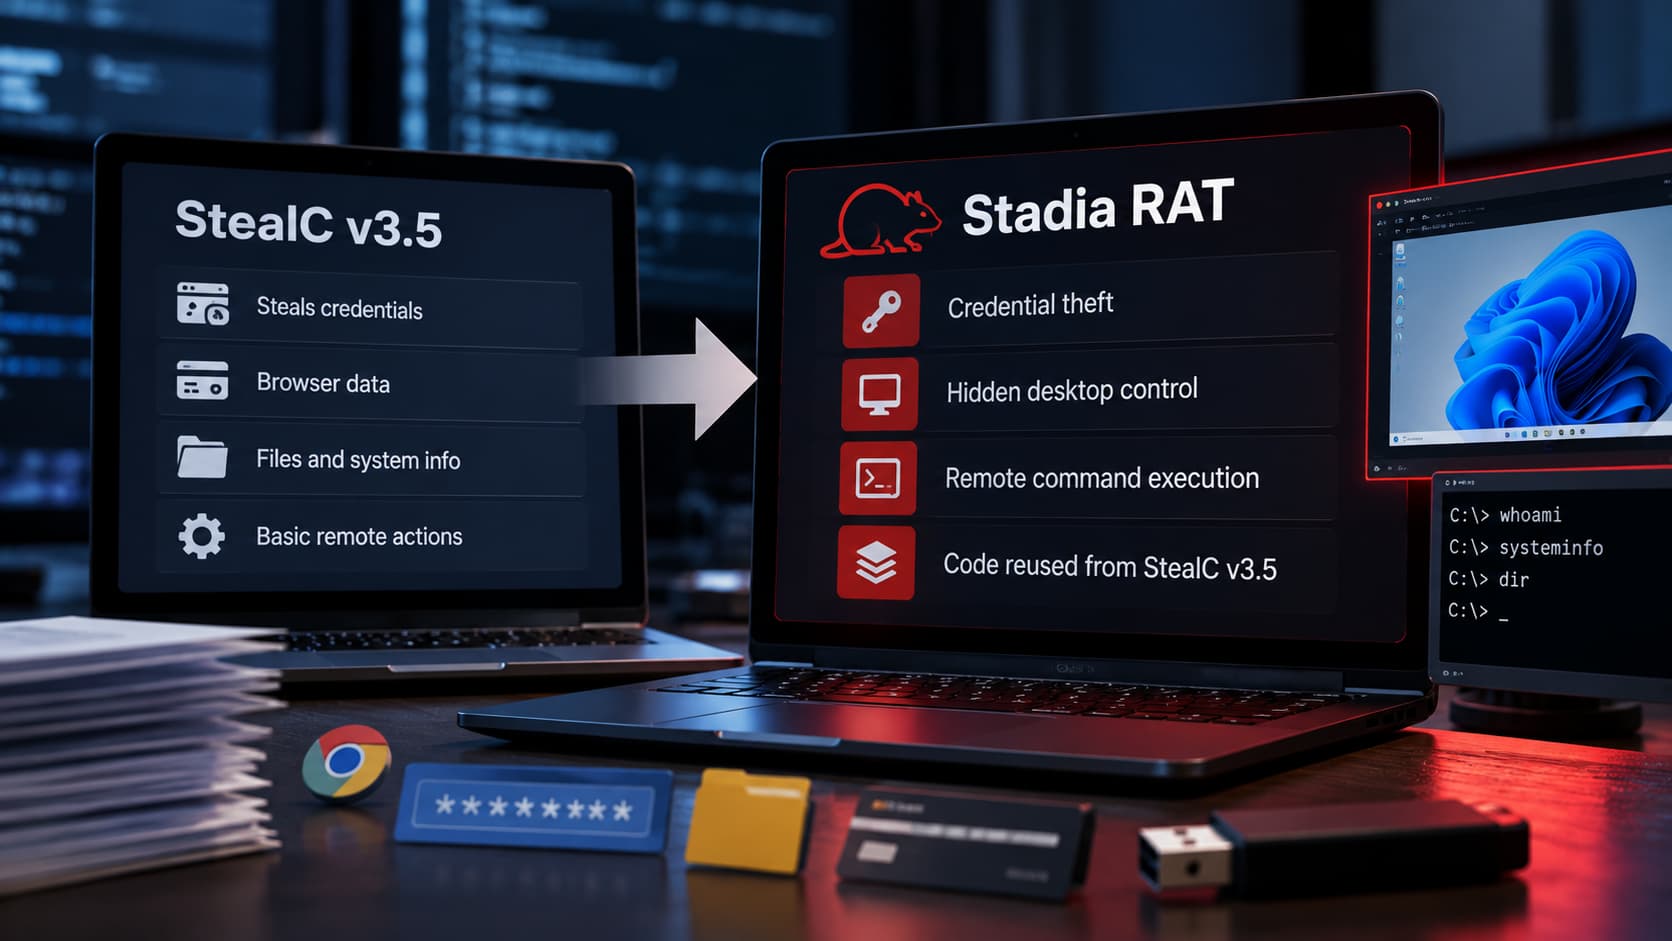
The cyber‑crime community has witnessed the return of the StealC threat, now operating under the name Stadia RAT, just weeks after the multinational Operation Endgame dismantled its primary distribution network.
Stadia RAT blends several capabilities that made its predecessor notorious: it harvests login credentials, silently captures the victim's desktop, and accepts remote commands from its operators. Security researchers note that the malware embeds a hidden remote access tool, allowing attackers to navigate infected machines as if they were sitting in front of them, while simultaneously siphoning passwords and other sensitive data.
Operation Endgame, a coordinated effort led by law‑enforcement agencies across Europe and North America, targeted the infrastructure used to sell and distribute StealC. The crackdown resulted in the seizure of servers, the arrest of key figures, and the disruption of online marketplaces that facilitated the malware’s spread. Yet, within days of the takedown, a new vendor surfaced offering Stadia RAT, indicating that the underlying codebase remained in circulation among underground actors.
Analysts at several cybersecurity firms say the rebranding reflects a broader trend of resilience among ransomware‑as‑a‑service platforms. When one distribution channel is closed, operators quickly repurpose the same tools, often adding minor tweaks to evade detection. The rapid emergence of Stadia RAT underscores the challenges faced by investigators who must not only dismantle existing networks but also anticipate the adaptive strategies of cybercriminals.
Experts emphasize the importance of robust defensive measures for organizations of all sizes. Regular patching, multi‑factor authentication, and network segmentation can limit the impact of credential‑stealing modules, while endpoint detection and response solutions are essential for spotting the stealthy desktop‑control components of RATs. As law‑enforcement agencies continue to pursue the individuals behind the original StealC operation, the cybersecurity community is urging businesses to stay vigilant against the evolving threat landscape.
The next steps for authorities likely involve tracking the new vendor’s infrastructure, collaborating with hosting providers, and possibly launching a follow‑up operation to disrupt the Stadia RAT supply chain before it gains wider foothold. Meanwhile, security teams are advised to monitor threat intelligence feeds for indicators of compromise associated with the new malware variant.



Comments (0)
Be the first to comment.
Join the discussion