Spring Ring Exploits Microsoft Teams to Deploy PowerShell RAT and NTLM Relay in Wide‑Scale Vishing Campaign
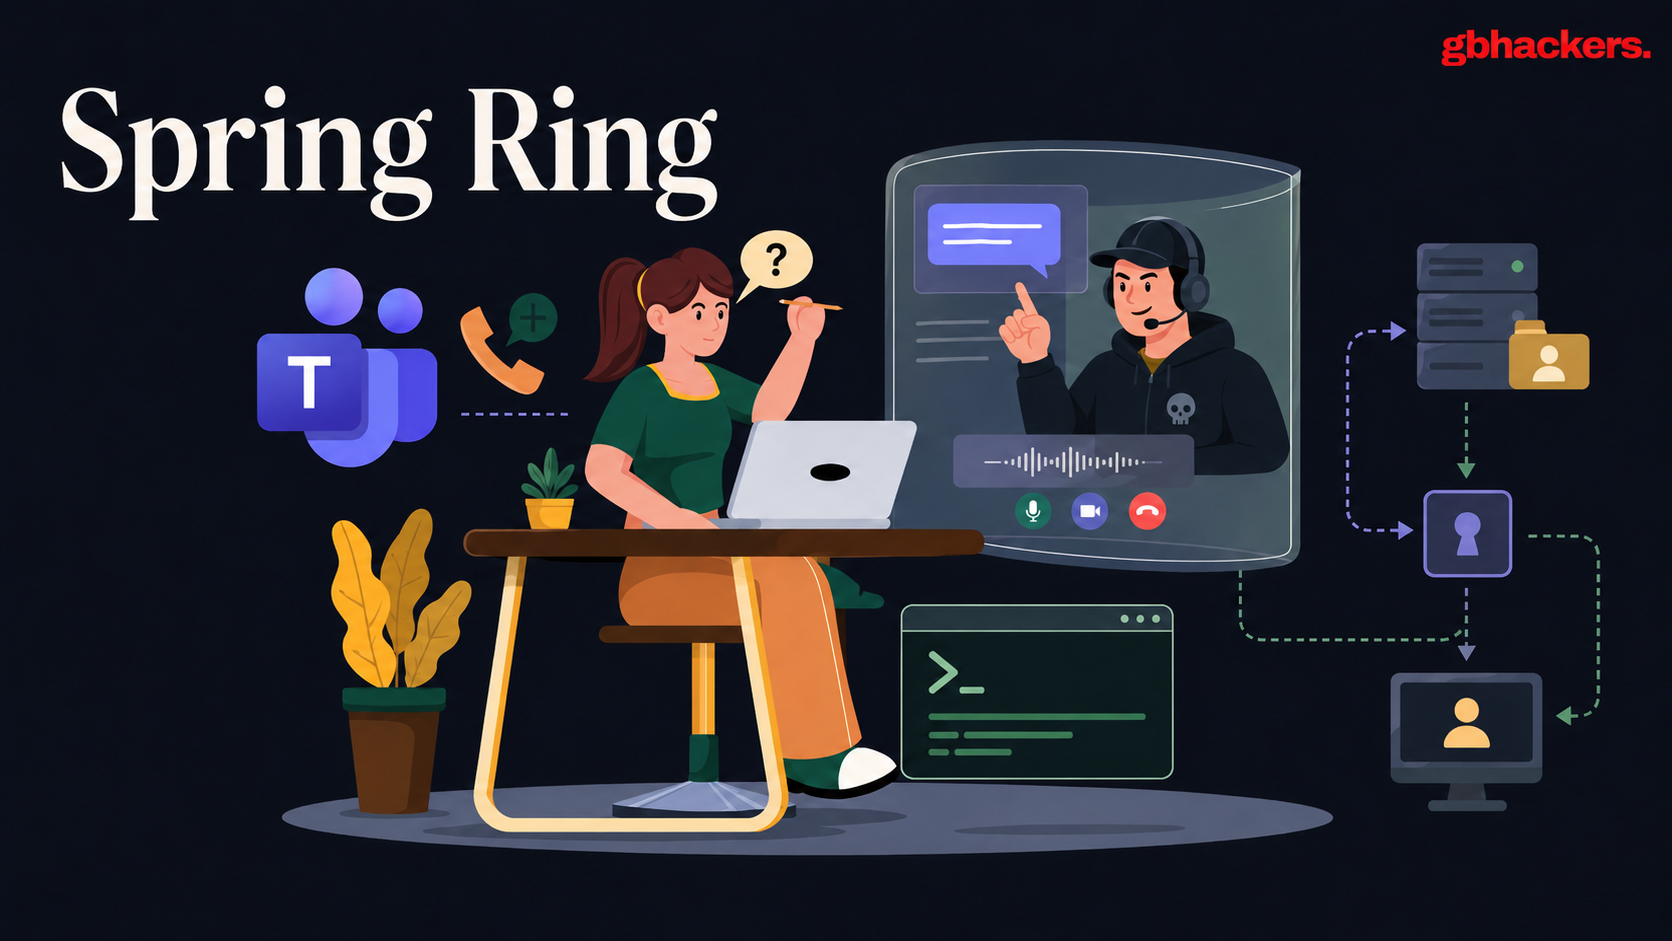
A coordinated social‑engineering operation dubbed "Spring Ring" leveraged Microsoft Teams external accounts to masquerade as corporate IT help desks, targeting more than 150 employees across at least ten organizations between January and April 2026.
The attackers began by creating legitimate‑looking Teams accounts that could be added as external participants to corporate groups. Once invited, the fraudsters initiated vishing calls—voice‑phishing conversations—in which they pretended to be support technicians, prompting victims to share credentials or install software under the guise of routine maintenance.
During the calls, the perpetrators delivered a PowerShell‑based remote access tool (RAT). The script, designed to run silently, established a foothold on the victim’s machine and enabled the use of NTLM relay attacks to capture hashed credentials when the user accessed internal resources. By relaying these hashes to other services, the attackers could move laterally within the compromised networks.
Security researchers who tracked the campaign observed that the victims spanned a variety of sectors, including finance, healthcare, and manufacturing. The operation’s timeline shows a steady flow of incidents over the four‑month period, suggesting a well‑orchestrated effort rather than isolated opportunistic attacks.
Detection came primarily through anomalous external account activity flagged by Microsoft’s security monitoring tools and by endpoint alerts triggered by the PowerShell payload. Organizations that responded quickly were able to isolate compromised accounts and revoke the malicious external identities, limiting further spread.
The Spring Ring campaign underscores a growing trend: threat actors are increasingly exploiting collaboration platforms that many enterprises trust for day‑to‑day communication. The ease with which external participants can be added to Teams channels creates a vector that, when combined with social engineering, can bypass traditional perimeter defenses.
Experts recommend several mitigations, including enforcing multi‑factor authentication for all external accounts, restricting the ability of external users to initiate calls or share files, and conducting regular phishing awareness training that specifically addresses voice‑based attacks. Network segmentation and strict monitoring of NTLM traffic can also reduce the impact of relay attempts.
Law enforcement and cybersecurity firms are monitoring the group for signs of escalation. As organizations continue to adopt cloud‑based collaboration tools, analysts expect similar campaigns to evolve, prompting a need for updated security policies that address both technical and human‑factor vulnerabilities.



Comments (0)
Be the first to comment.
Join the discussion