New “Relapse” Exploit Chains Browser Flaw and Kernel Race to Jailbreak PS5 Models
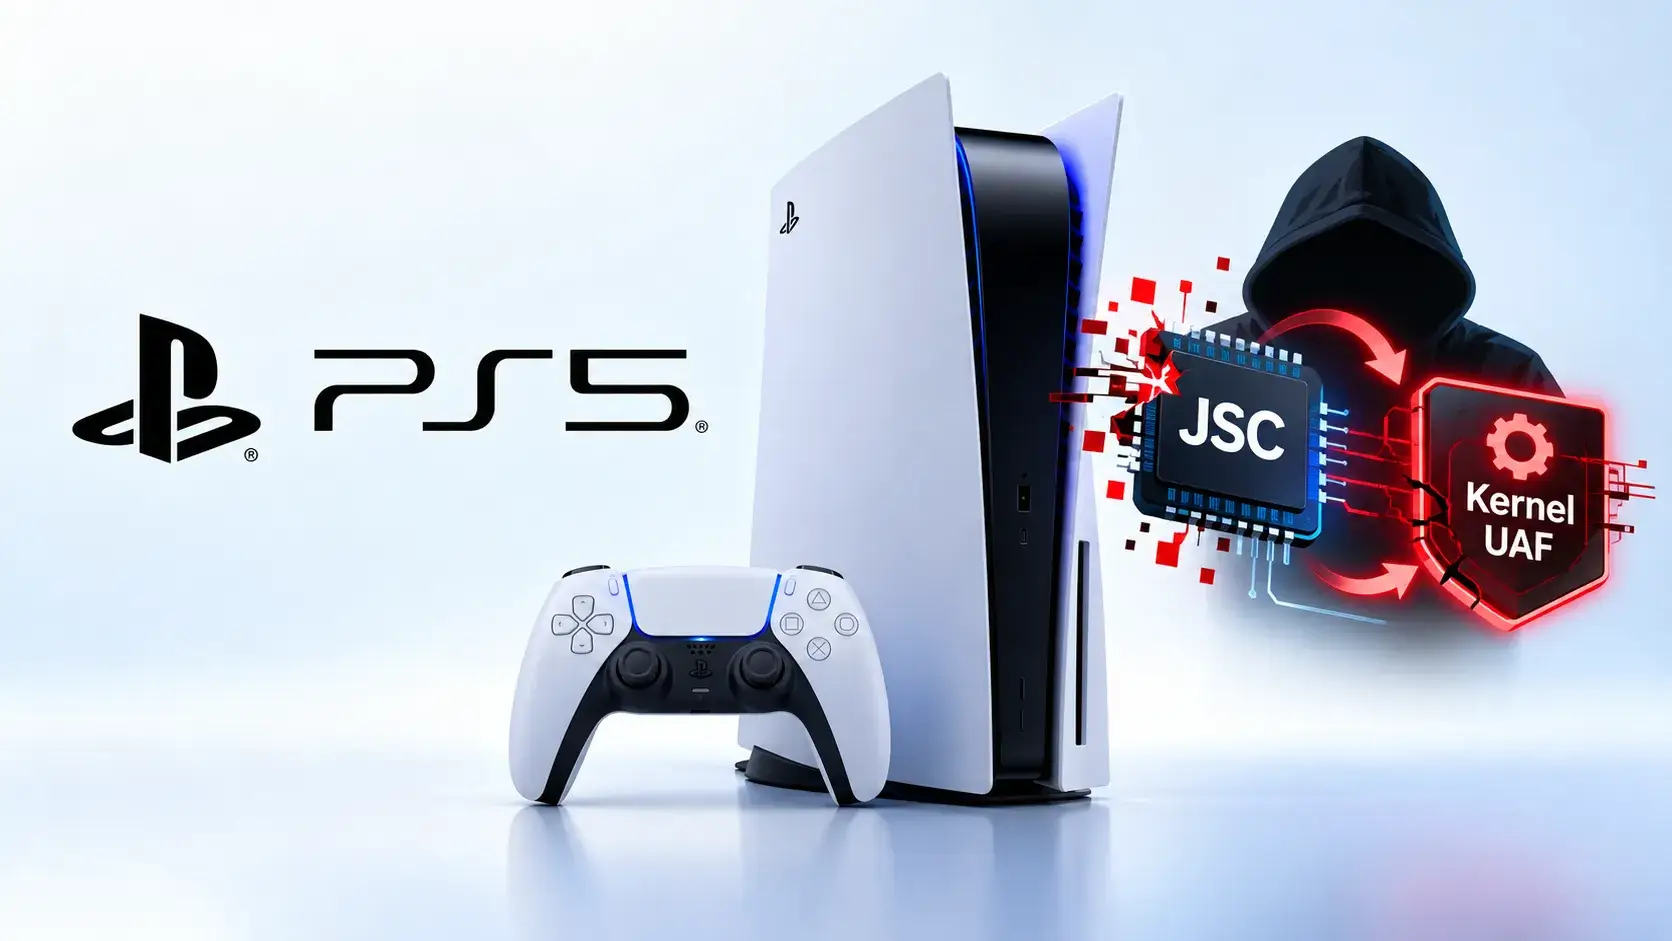
A fresh exploit named Relapse has been released that can bypass the security of both PlayStation 5 and PlayStation 5 Pro consoles running firmware from version 7.00 up through 13.60. The chain merges a browser‑based JavaScriptCore memory‑corruption bug with a kernel‑level use‑after‑free race, giving attackers full control of the system.
The first stage leverages JavaScriptCore, the engine that powers the console’s built‑in web browser. By feeding specially crafted script into a web page, the exploit corrupts the engine’s memory layout, allowing arbitrary code execution within the browser sandbox. This technique, previously seen only in limited PC exploits, is novel for the PlayStation environment.
Once code runs in the browser, the second stage triggers a race condition in the kernel’s memory management. A use‑after‑free (UAF) flaw is provoked, letting the attacker reuse freed kernel objects to execute code with kernel privileges. The combination of user‑space corruption and kernel‑level UAF creates a reliable path to a full system jailbreak.
Relapse marks a significant expansion over earlier PS5 jailbreaks, which were typically limited to narrow firmware windows or required hardware modifications. By covering versions 7.00 through 13.60, the exploit spans almost the entire lifespan of the console, which launched in late 2020. This broad reach means many owners who have not updated to the latest patches could be vulnerable.
The discovery has immediate implications for both the homebrew community and Sony’s security posture. While a jailbreak can enable custom applications, emulators and other user‑generated content, it also opens the door to piracy and potential exploitation of the console’s online services. Sony has not yet issued a public statement, but historically the company patches such vulnerabilities through firmware updates.
Security researchers and hobbyist groups are already analyzing Relapse’s code to understand its limitations and to develop countermeasures. Users are advised to keep their systems updated and to avoid visiting untrusted web pages on the console’s browser. The arms race between console manufacturers and the hacking community is likely to continue as new exploits surface and manufacturers respond with tighter defenses.

Comments (0)
Be the first to comment.
Join the discussion