ShinyHunters Breaches FBI Recruitment Site, Allegedly Exposes Data on Most Agents and Applicants
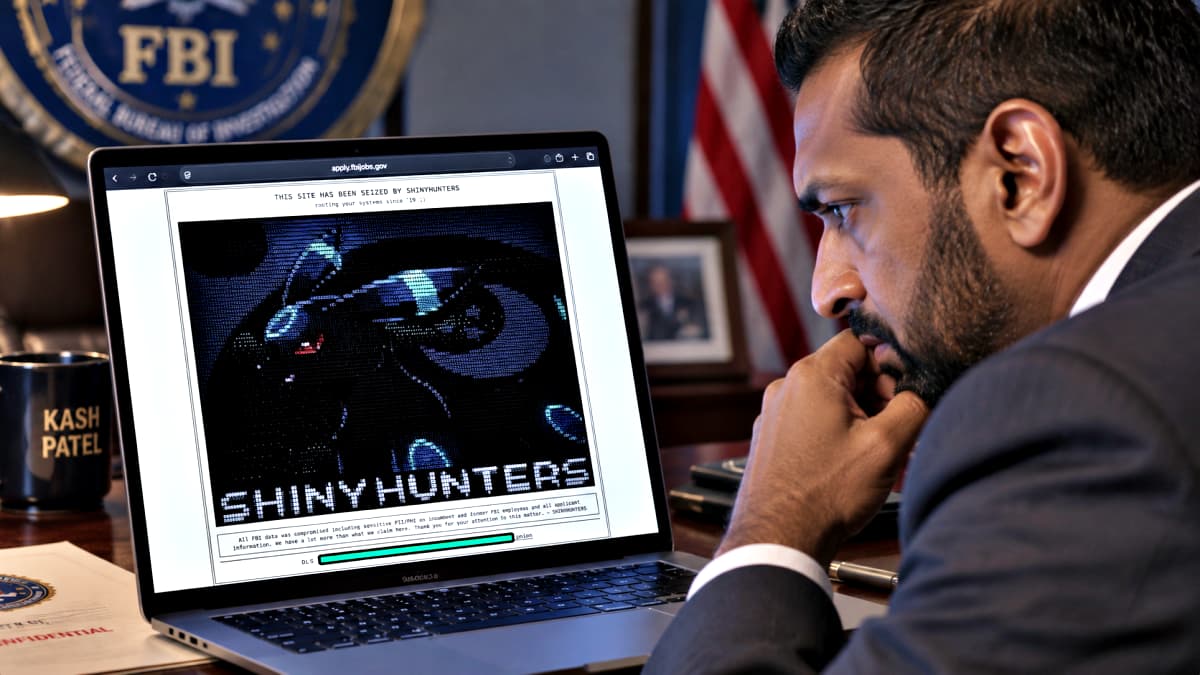
Cybercrime group ShinyHunters announced on Tuesday that it successfully infiltrated the Federal Bureau of Investigation's online jobs portal, claiming to have extracted personal information on nearly every current FBI employee and job seeker who had applied through the site.
The breach was revealed after the portal was temporarily taken offline for security maintenance. According to the hackers, the compromised data includes names, contact details, employment histories, and other identifiers that could be used to target individuals linked to the bureau.
ShinyHunters, a loosely organized collective known for high‑profile leaks of corporate and governmental databases, has previously targeted organizations ranging from video‑game companies to public utilities. Their modus operandi typically involves exploiting unpatched web applications to gain unauthorized access, followed by public disclosure of the stolen files to pressure victims into paying ransoms or to gain notoriety within the underground hacking community.
The potential fallout from the alleged exposure is significant. FBI agents and prospective hires could face heightened personal risk, including phishing attacks, identity theft, or even physical threats if the information falls into the hands of adversarial actors. Moreover, the breach raises concerns about the security of other government recruitment platforms that store sensitive personal data for large numbers of applicants.
Federal officials confirmed that the Jobs portal was taken down shortly after the intrusion was detected, and a multi‑agency task force has been mobilized to assess the scope of the compromise. While the FBI has not disclosed whether any classified information was accessed, it emphasized that the site’s architecture is separate from the agency’s core investigative systems, limiting the immediate operational impact.
Cybersecurity experts note that the incident underscores a broader trend of threat actors targeting government-facing web services, which often lag behind private‑sector counterparts in patch management and security hardening. The FBI has previously warned of increased attempts to exploit vulnerabilities in its public‑facing websites, prompting a series of internal reviews and upgrades to its defensive posture.
As investigators continue to piece together the full extent of the data leak, the agency has urged affected individuals to monitor their accounts for suspicious activity and to follow recommended steps for safeguarding personal information. The incident also serves as a reminder to all organizations that even seemingly low‑risk portals can become lucrative entry points for sophisticated cyber‑crime groups.



Comments (0)
Be the first to comment.
Join the discussion