Wildberries Blames DDoS Attack for Seller Payment Delays
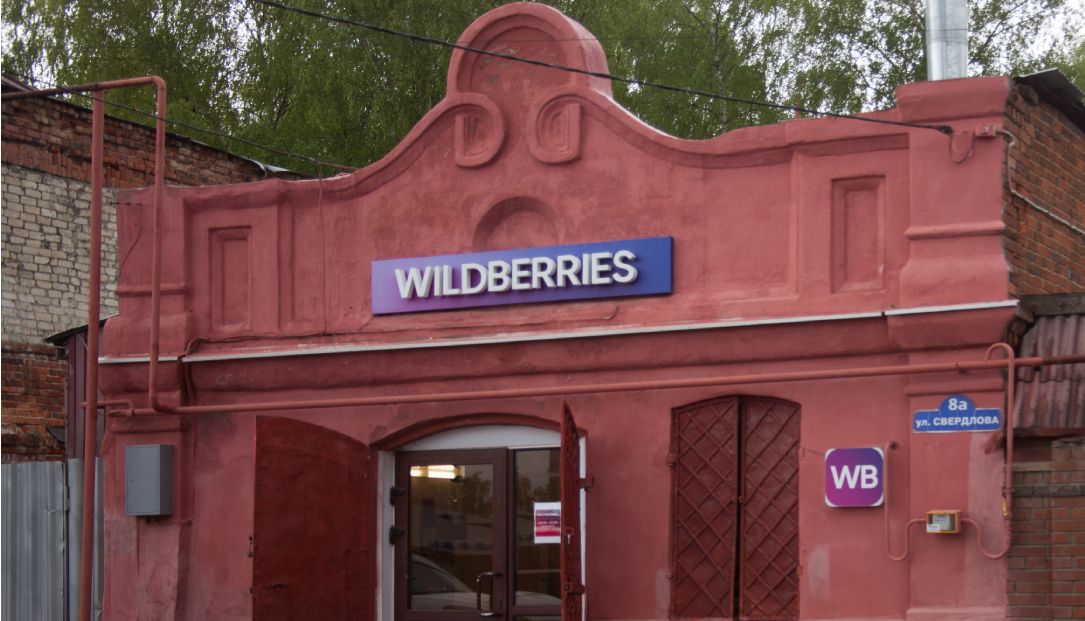
Russia's leading online retailer Wildberries announced that a recent distributed denial‑of‑service (DDoS) attack forced the company to implement emergency security protocols, which in turn postponed payouts to a number of its marketplace sellers.
The cyber assault targeted the internal platforms Wildberries uses to log sales and process withdrawals, overwhelming the servers and disrupting the flow of transaction data. By flooding the system with massive amounts of traffic, the attackers temporarily disabled the mechanisms that verify and release funds to merchants.
In statements to several Russian news outlets earlier this week, Wildberries said the company had to suspend normal payment operations while it fortified the affected infrastructure. The retailer emphasized that the security measures were necessary to protect both the platform and its users from further compromise, even though they resulted in a backlog of outstanding balances.
For many small and medium‑sized sellers who rely on timely payments to cover inventory and operating costs, the delay poses a tangible financial strain. Some merchants reported difficulty meeting supplier obligations and expressed concern about the uncertainty surrounding future disbursements.
Wildberries, which commands a significant share of Russia's e‑commerce market, has previously navigated regulatory and logistical challenges but has rarely faced a cyber‑security incident of this scale. The current episode underscores the growing vulnerability of large online marketplaces to coordinated attacks, especially as they become more integral to the national economy.
Industry analysts note that the incident may prompt tighter cybersecurity standards for Russian digital retailers and could lead to increased oversight from government agencies tasked with safeguarding critical commercial infrastructure. Wildberries has not disclosed a timeline for fully restoring the payment system, but it pledged to keep sellers informed as the situation evolves.

Comments (0)
Be the first to comment.
Join the discussion