Phishing Campaigns Pivot to Trusted Email Channels and Sophisticated URL Masking
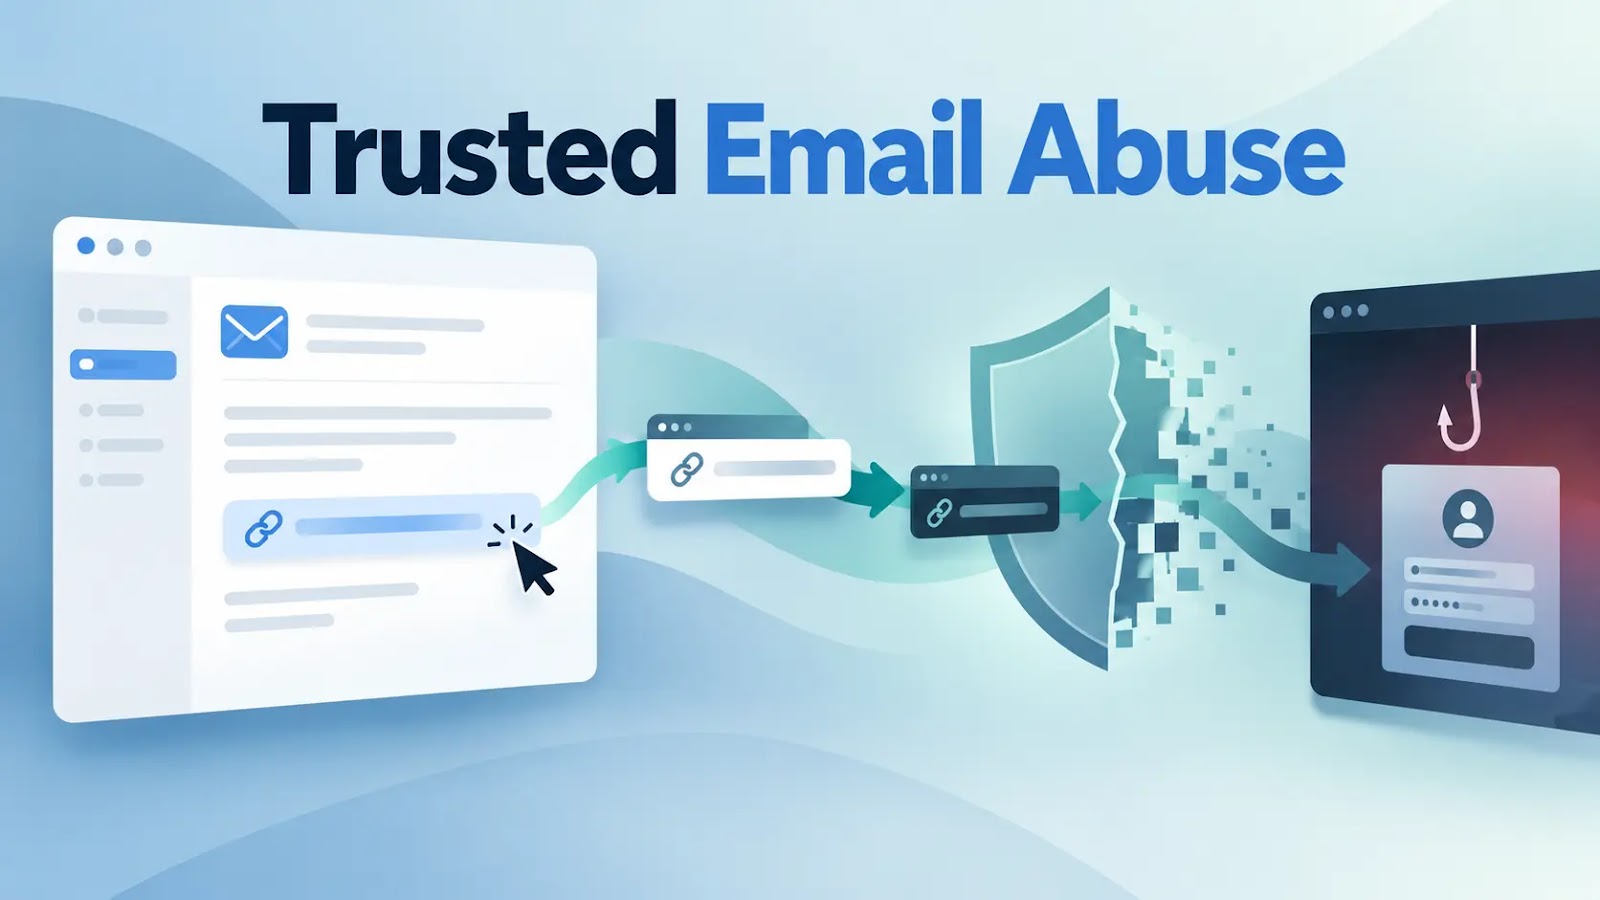
Cybercriminals are increasingly abandoning the use of malicious attachments in phishing emails, opting instead for delivery methods that leverage reputable email services and authenticated domains. This shift aims to slip past conventional security filters that focus on detecting dangerous file types.
Analysts monitoring the ongoing VBSpam comparative test have noted a steady rise in campaigns that employ multi‑stage URL cloaking. By routing victims through a chain of seemingly legitimate web addresses, attackers can mask the final malicious destination, making it harder for automated scanners to flag the content.
The strategy takes advantage of the trust placed in well‑known email infrastructure providers. When a phishing message originates from an authenticated domain hosted by a major service, many email gateways treat it with a lower level of suspicion, reducing the likelihood of quarantine or deletion.
Security researchers explain that this evolution reflects a broader trend in the threat landscape: attackers are focusing on social engineering tactics that exploit user expectations rather than relying on overt malware payloads. By presenting a familiar sender address and a clean attachment‑free message, they increase the chances that recipients will click on the embedded links.
Defenders are responding by enhancing URL reputation services and incorporating real‑time link analysis that can follow redirection chains. However, the sophistication of multi‑stage cloaking means that static blacklists often lag behind, prompting organizations to adopt behavior‑based detection and user education programs.
As the VBSpam test continues to track these developments, experts warn that the reliance on trusted delivery channels is likely to persist. Ongoing vigilance, combined with adaptive security controls, will be essential to mitigate the growing risk posed by phishing campaigns that blend legitimacy with deception.



Comments (0)
Be the first to comment.
Join the discussion