Python‑Based Malware Hijacks Credentials Across 17 Chromium Browsers and Firefox
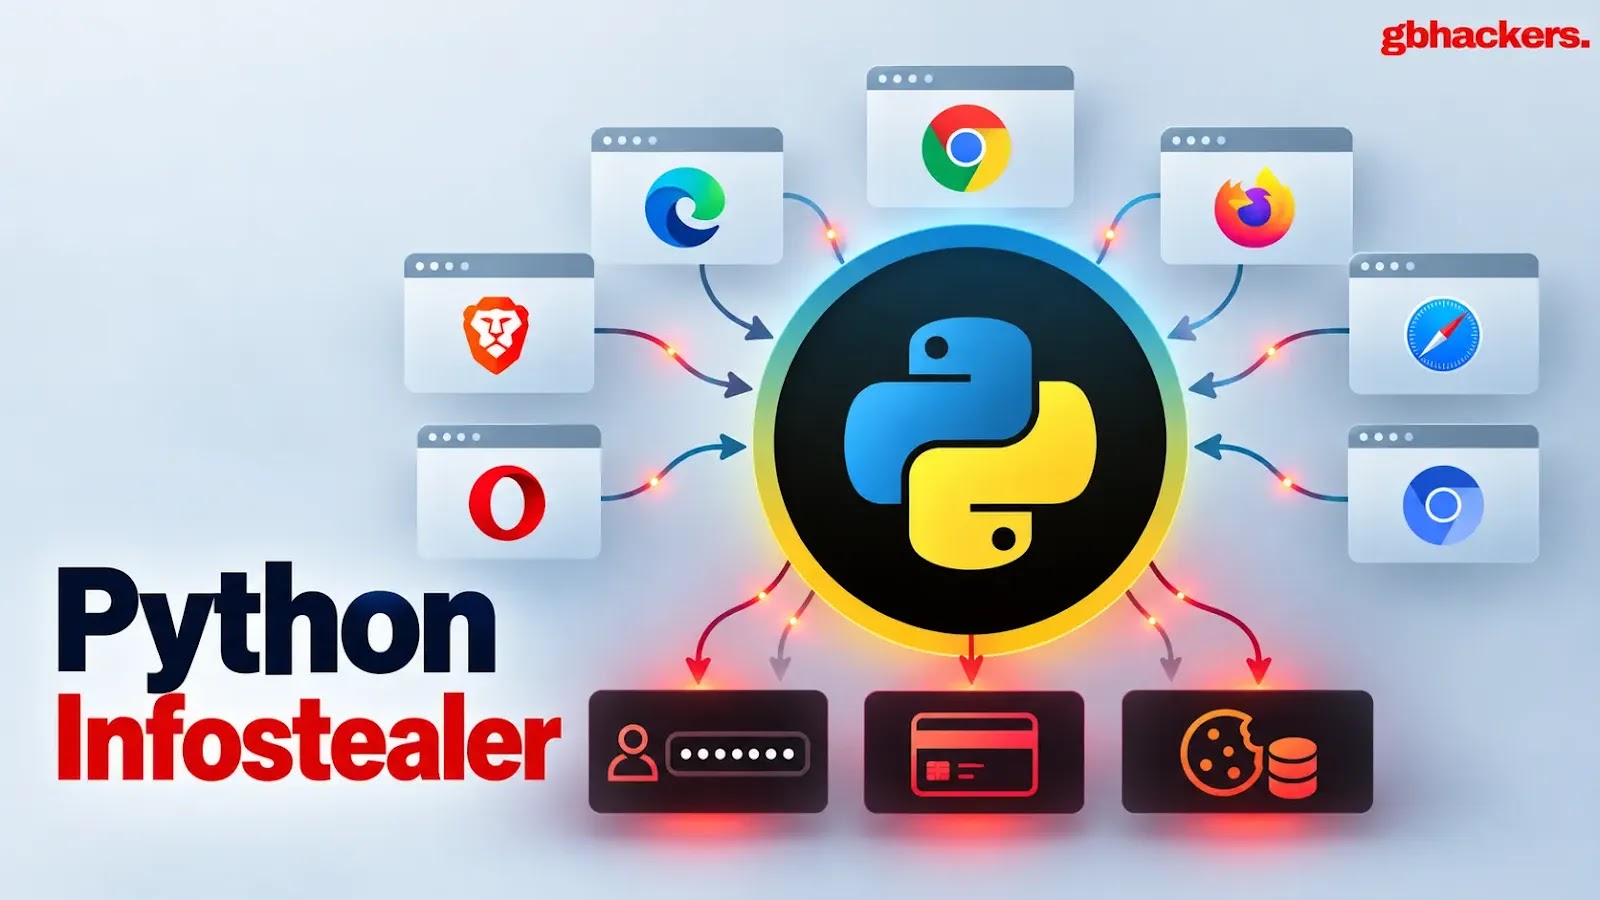
A new Python‑written information stealer has been identified that can exfiltrate saved passwords, payment‑card numbers, browsing histories, and active session cookies from a wide range of web browsers. Security researchers say the tool is capable of compromising 17 Chromium‑derived browsers in addition to Mozilla Firefox, giving cybercriminals a broad foothold on infected machines.
The malware is distributed via a modular builder framework that allows operators to customize payloads and delivery methods. By leveraging Python’s cross‑platform capabilities, the code can run on Windows, macOS, and Linux systems without major modifications, increasing its appeal to threat actors seeking a versatile instrument.
Analysis of the code reveals that it scans the local profile directories of each targeted browser, extracting encrypted credential stores, saved credit‑card information, and cookie files that maintain logged‑in sessions. The stolen data is then packaged and transmitted to command‑and‑control servers controlled by the attackers, where it can be sold on underground markets or used for direct financial fraud.
Cybersecurity experts note that the inclusion of so many Chromium variants—such as Brave, Vivaldi, Opera, and Microsoft Edge—represents a significant escalation in scope. Previously, most infostealers focused on a handful of popular browsers; this expansion increases the likelihood that everyday users will have at least one vulnerable application on their device.
The emergence of the Python‑based stealer underscores a broader trend of malware developers adopting high‑level languages to streamline development and evade detection. Python’s extensive libraries simplify tasks like encryption, network communication, and file system access, while also allowing rapid updates to bypass security tools. Analysts recommend that users keep browsers and extensions up to date, employ reputable password managers, and monitor for unexpected network traffic to mitigate the risk.
The threat was first reported by the GBHackers community, which flagged the builder framework as a service offered to affiliates. Law‑enforcement agencies are reportedly monitoring the infrastructure, but the distributed nature of the tool means that attribution and takedown may be challenging. Security firms advise organizations to implement layered defenses, including endpoint detection and response solutions, to identify the malicious activity before credentials are exfiltrated.



Comments (0)
Be the first to comment.
Join the discussion