Researchers Reveal AI Workflow Identity Hijacking Technique Threatening Corporate Data
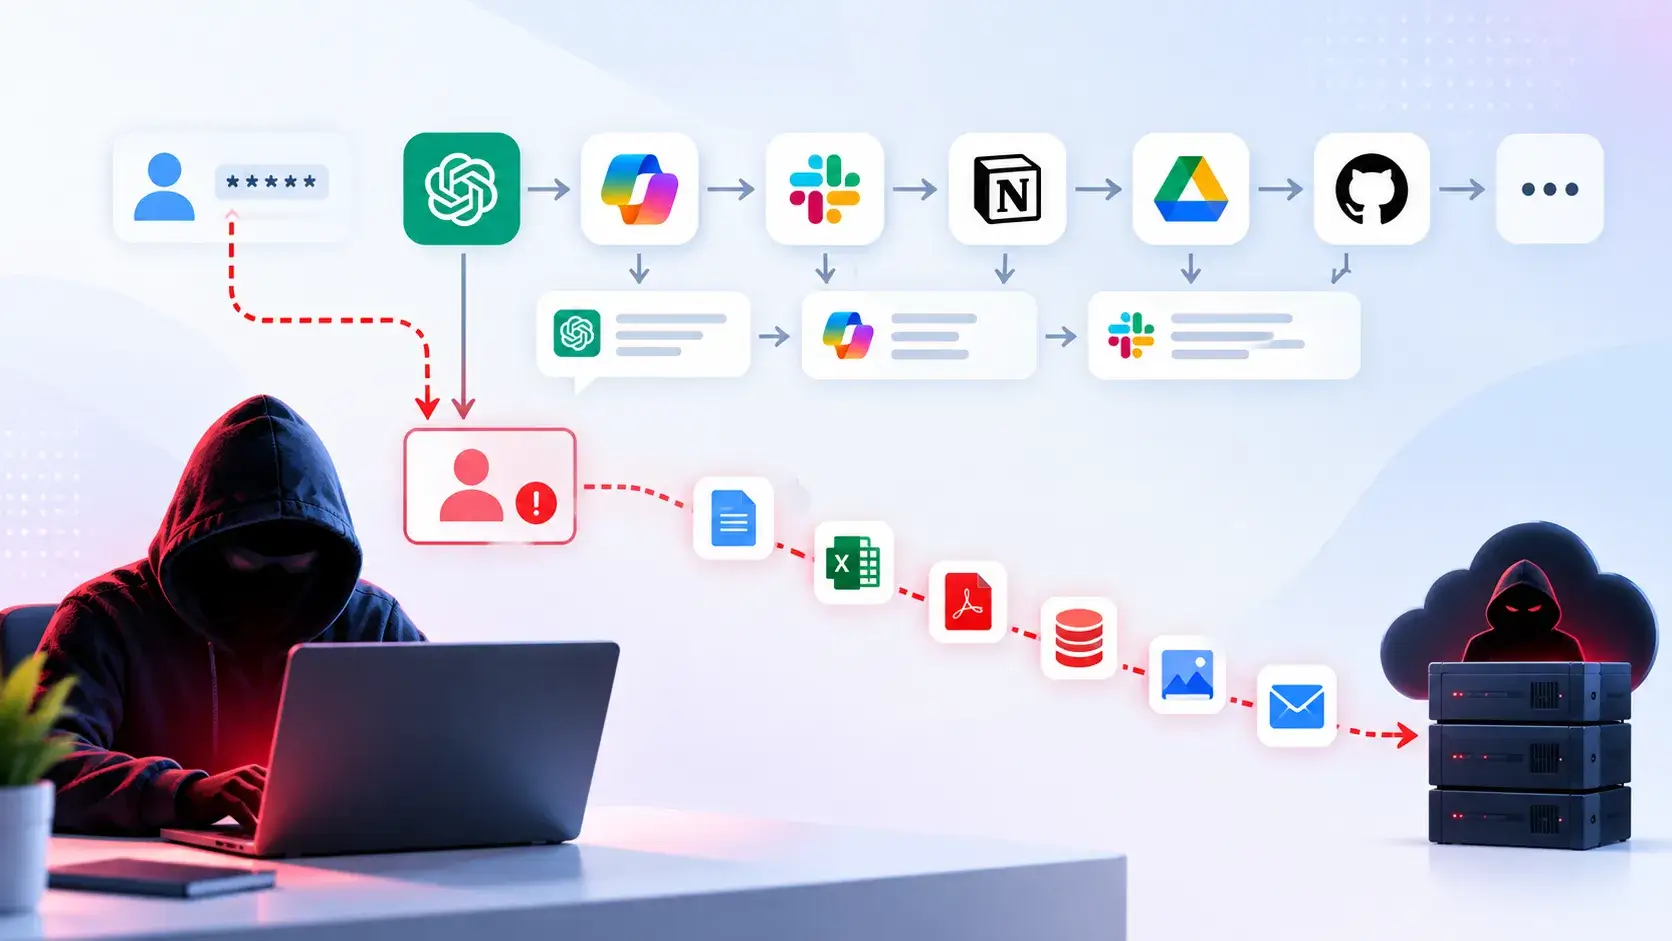
Security researchers have disclosed a novel attack vector dubbed “Workflow Identity Hijacking,” which allows external actors to siphon confidential corporate information by exploiting AI‑driven automation tools. The method leverages the trust that enterprise AI systems place in routine requests, turning seemingly innocuous inputs into a conduit for data exfiltration.
The hijacking process begins with an attacker crafting a request that mimics a legitimate workflow trigger—such as a routine data retrieval or report generation. Because the request originates from a trusted interface, the AI automation proceeds without additional verification, ultimately delivering the requested output to a location controlled by the adversary. In practice, the attack does not require the exploitation of software vulnerabilities; instead, it subverts the identity and authorization assumptions embedded in the workflow design.
AI‑powered automations have become integral to modern enterprises, streamlining tasks ranging from document processing to supply‑chain coordination. Organizations often integrate large language models and other generative AI services into internal pipelines, trusting them to interpret user commands, route information, and generate responses. This growing reliance creates a broad attack surface: any system that accepts external input and acts on behalf of a user can become a vector for identity hijacking if its authentication checks are insufficient.
The emergence of this technique raises immediate concerns for data security and compliance. Sensitive datasets—financial records, intellectual property, personal employee information—can be extracted without raising traditional alarms, as the AI system believes it is fulfilling a legitimate request. Regulators and auditors may find it harder to trace the breach, given that the malicious activity blends into normal workflow traffic. The potential for large‑scale data loss underscores the need for organizations to reassess how AI services are authorized and monitored.
Experts recommend a multi‑layered response, including stricter verification of workflow initiators, contextual anomaly detection, and audit trails that capture AI decision points. Vendors of AI automation platforms are also urged to embed granular permission controls and to provide visibility into request provenance. As the technique gains attention, further research is expected to refine detection methods and to develop best‑practice guidelines for securing AI‑enabled processes across industries.



Comments (0)
Be the first to comment.
Join the discussion