Researchers Uncover New Microsoft Entra Exploit That Hijacks MFA Prompts to Capture Credentials
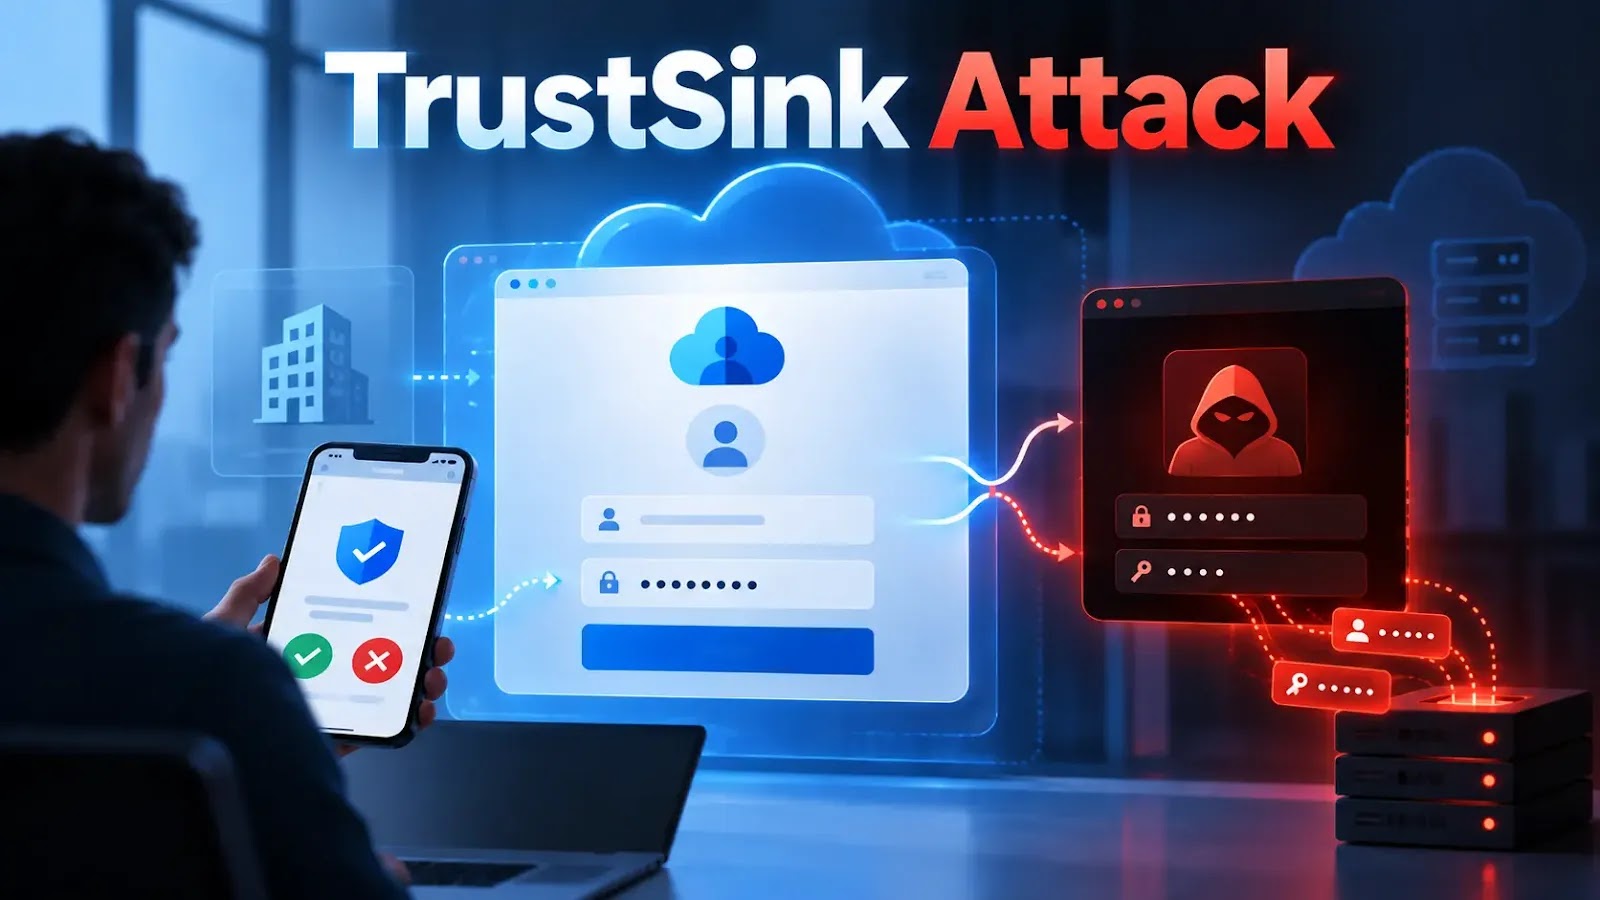
Security researchers have disclosed a novel credential‑phishing technique, dubbed TrustSink, that exploits Microsoft Entra's external authentication methods to embed a counterfeit password prompt within a genuine sign‑in experience, enabling attackers to steal user credentials.
The attack hinges on an adversary who has already obtained elevated privileges inside an organization’s Entra tenant. By registering a malicious third‑party multi‑factor authentication (MFA) provider through the External Authentication Methods (EAM) feature, the attacker can cause the rogue prompt to appear whenever a user attempts to log in, making the request appear indistinguishable from Microsoft’s native UI.
Microsoft Entra, the rebranded Azure Active Directory, supports integration with a variety of external MFA solutions to give enterprises flexibility in meeting compliance and usability requirements. While the EAM capability broadens authentication options, it also expands the attack surface, as the platform trusts any provider that an administrator adds.
TrustSink is classified as a post‑compromise method: it assumes the attacker has already breached the tenant, often through phishing, credential stuffing, or other initial access techniques. Once inside, the rogue MFA provider becomes a conduit for harvesting additional high‑value credentials, including those of privileged users, thereby amplifying the impact of the original breach.
Microsoft has responded by issuing guidance that urges administrators to audit all external authentication providers, enforce least‑privilege admin roles, and enable monitoring for unusual provider registrations. The company also indicated that future updates will incorporate detection signals for the TrustSink pattern into its security logs and alerting mechanisms.
Industry experts recommend that organizations regularly review their MFA configurations, limit the use of third‑party providers through conditional access policies, and consider moving toward password‑less authentication where feasible. The emergence of TrustSink highlights the growing trend of attackers weaponizing native cloud identity features, reinforcing the need for continuous vigilance and robust identity governance.



Comments (0)
Be the first to comment.
Join the discussion