Infostealer Trio Exploits Developer Workstations to Harvest Cloud Credentials
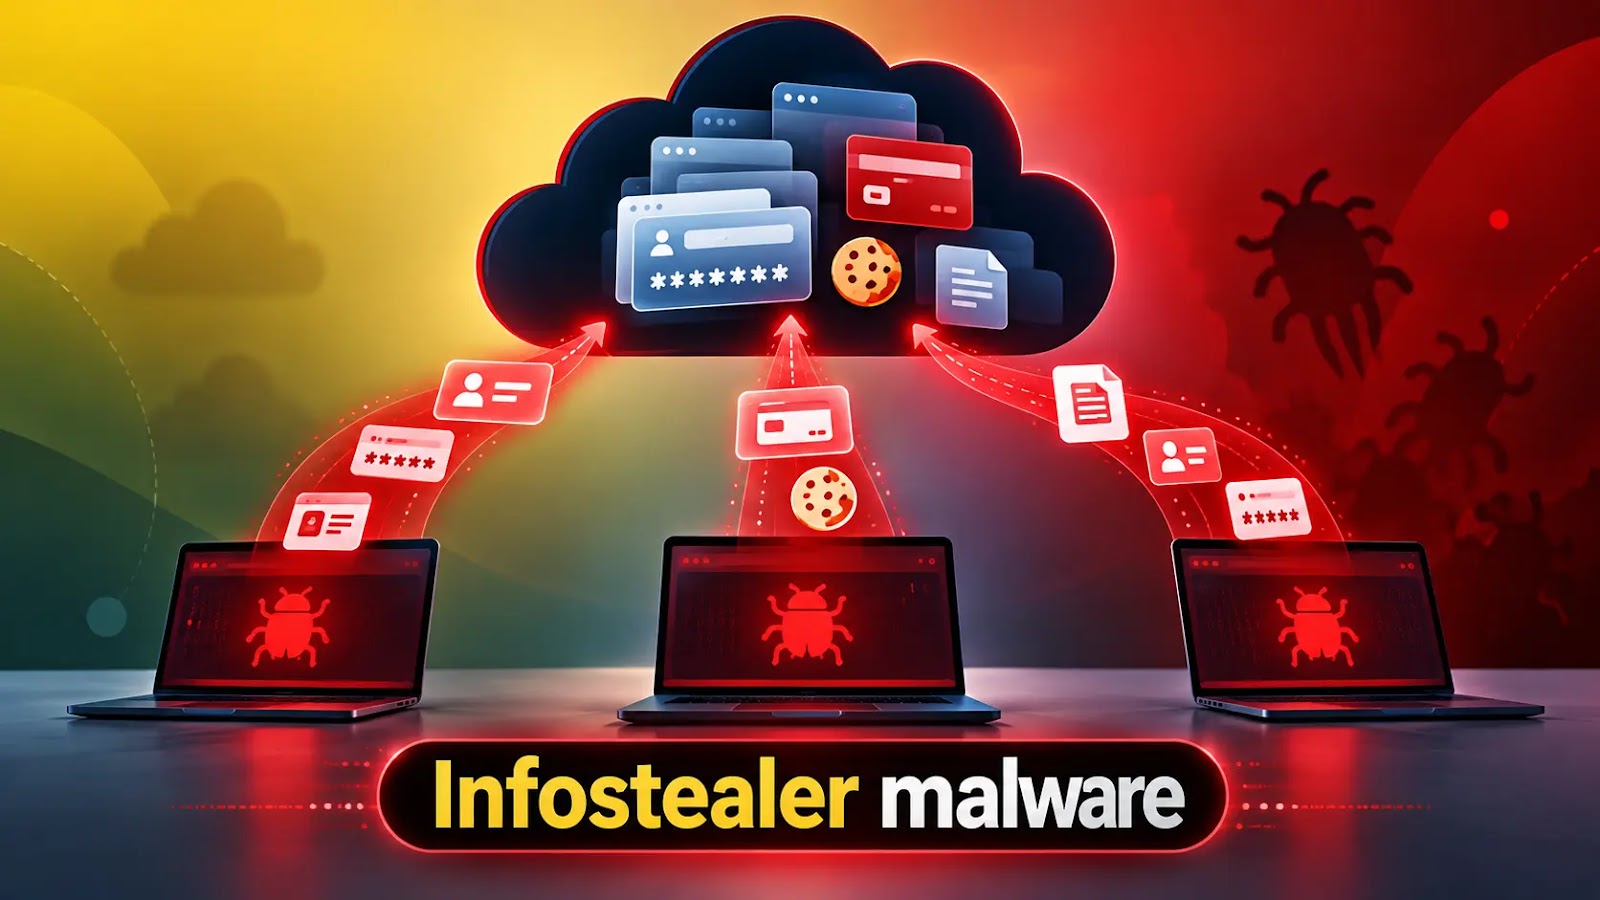
Security researchers have identified a growing trend in which sophisticated infostealer malware is being used as a conduit to extract cloud access data from compromised developer machines. The campaign, observed across multiple threat actors, centers on three primary families—Lumma, RedLine and Vidar—each capable of siphoning API keys, authentication tokens and active browser sessions that grant entry to corporate cloud environments.
Unlike traditional ransomware or spyware that focus on financial gain through direct extortion, these infostealers target identity artifacts that enable persistent, low‑profile access to cloud services. By infiltrating a developer's workstation, the malware can locate stored credentials in configuration files, environment variables, and browser caches, then relay them to remote command‑and‑control servers for later exploitation.
The shift toward cloud‑centric attacks reflects the broader migration of enterprise workloads to platforms such as Amazon Web Services, Microsoft Azure and Google Cloud. As organizations increasingly rely on API‑driven automation, the value of stolen keys and tokens has risen sharply, offering attackers the ability to spin up resources, exfiltrate data or move laterally within a network without triggering conventional detection mechanisms.
Analysts note that Lumma, RedLine and Vidar share a modular architecture that allows them to adapt to different development environments and operating systems. Each variant incorporates routines to scan for popular IDEs, version‑control directories and credential‑management tools, increasing the likelihood of locating valuable secrets. The malware also harvests active session cookies from browsers, enabling attackers to impersonate legitimate users in real time.
Industry observers stress that the emphasis on identity theft rather than direct data breach underscores a strategic pivot. By securing footholds within cloud accounts, threat actors can conduct prolonged espionage, siphon proprietary code, or leverage compromised resources for cryptocurrency mining and other illicit activities.
Defenders are urged to adopt a multi‑layered approach, including the use of hardware‑based authentication, regular rotation of API secrets, and rigorous monitoring of anomalous cloud activity. Implementing least‑privilege principles for developer access and employing secret‑scanning tools in code repositories can also reduce the attack surface.
While the exact scale of the Lumma, RedLine and Vidar campaigns remains under investigation, the emergence of these infostealers highlights the need for heightened vigilance around credential hygiene in development workflows. As cloud adoption continues to expand, security teams must prioritize the protection of identity assets to thwart the next wave of credential‑focused intrusions.



Comments (0)
Be the first to comment.
Join the discussion