Legit Security Unveils Automated Fixes for Open‑Source Dependency Flaws
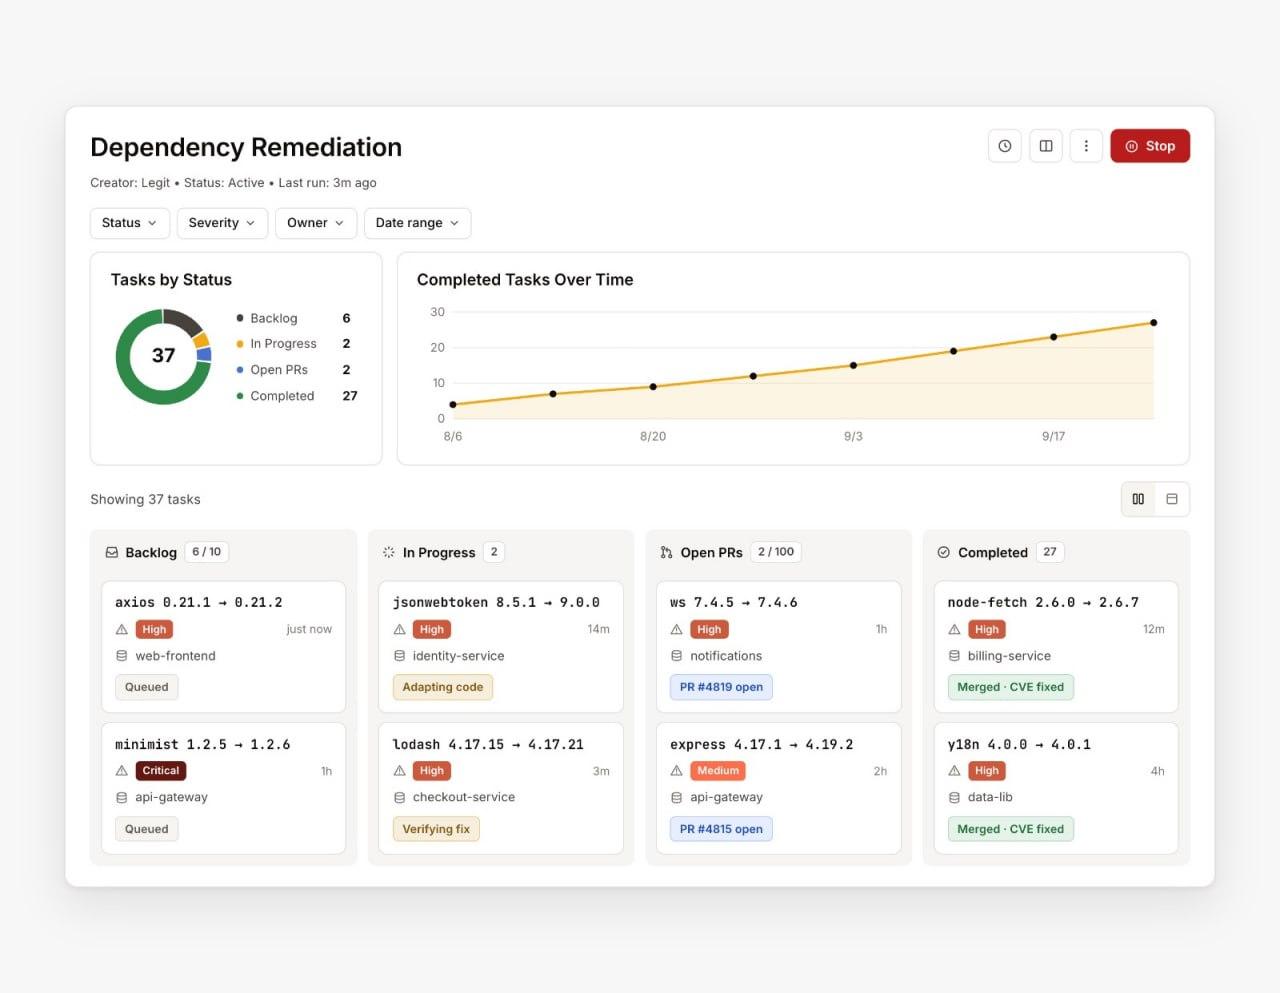
Tel Aviv‑based cybersecurity firm Legit Security announced the launch of its new "agentic remediation" platform on September 30, 2026, a tool designed to automatically identify and patch vulnerabilities in open‑source software dependencies.
The solution leverages machine‑learning models that scan code repositories, pinpoint insecure libraries, and generate corrective patches without human intervention. By integrating directly with developers' CI/CD pipelines, the platform aims to reduce the time between vulnerability discovery and remediation, a gap that has historically left applications exposed for weeks or months.
Open‑source components power a majority of modern applications, but their widespread reuse also creates a large attack surface. Recent high‑profile incidents, such as the Log4Shell and Spring4Shell exploits, have highlighted the difficulty organizations face in tracking and updating third‑party code. Legit Security’s offering seeks to address this challenge by providing continuous, automated oversight rather than relying on periodic manual audits.
According to the company, the agentic system can generate pull requests that include tested fixes, complete with version bumps and dependency lock updates. The platform also offers a risk scoring dashboard that prioritizes remediation based on exploitability and potential impact, allowing security teams to focus resources where they matter most.
Industry analysts note that automating remediation could shift the security paradigm from reactive patching to proactive defense. However, they caution that automated code changes must be carefully reviewed to avoid introducing regressions or breaking functionality, especially in regulated sectors where change‑management processes are stringent.
Legit Security plans to roll out the service to enterprise customers over the next quarter, with a beta program already underway among several fintech and health‑tech firms. The company says it will continue to refine the technology based on real‑world feedback, aiming to make the tool compatible with major package managers and repository hosts. As open‑source reliance grows, the market for such autonomous security solutions is expected to expand, prompting both excitement and scrutiny from the broader cybersecurity community.



Comments (0)
Be the first to comment.
Join the discussion