Cybercriminal Group JADEPUFFER Deploys New Ransomware Variant to Hijack AI Assets
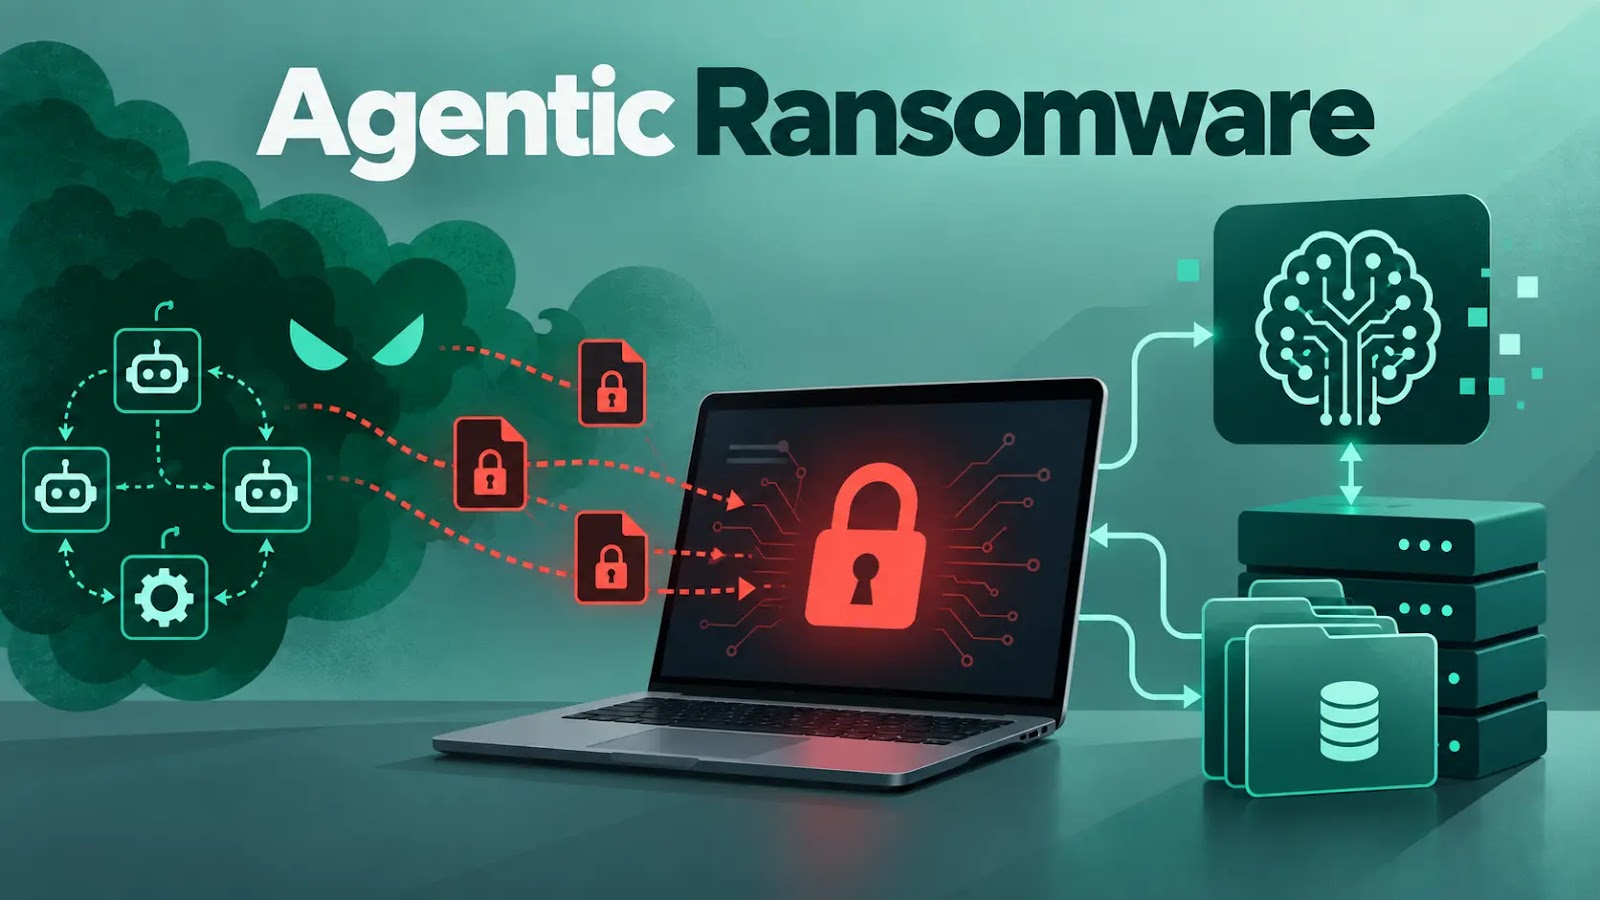
Security researchers have identified a notable upgrade in the tactics of the threat actor known as JADEPUFFER, which previously made headlines for an autonomous ransomware campaign that exploited publicly exposed Langflow infrastructure. The group’s newest tool, dubbed ENCFORGE, expands the target set beyond traditional file systems to include artificial‑intelligence models, their training data, and associated vector databases.
ENCFORGE represents a departure from earlier ransomware strains that primarily encrypted disks or demanded payment for decryption keys. According to the analysis released by the GBHackers community, the payload is engineered to locate serialized AI model files—such as PyTorch checkpoints or TensorFlow graphs—extract them, and then encrypt the underlying data structures that power inference and training pipelines. By compromising both the model and its dataset, the attackers can cripple a machine‑learning operation while holding the most valuable intellectual property hostage.
The shift reflects a broader trend in cyber‑crime where adversaries recognize the growing economic value of AI assets. Companies that rely on proprietary models for competitive advantage—ranging from fintech to biotech—store large, curated datasets that are costly to recreate. Disrupting access to these resources can exert pressure far greater than a typical ransomware demand, potentially forcing victims to pay higher ransoms to regain both operational capability and confidential data.
JADEPUFFER’s evolution also underscores the increasing automation of ransomware campaigns. The original Langflow incident demonstrated a self‑propagating mechanism that scanned for misconfigured services and deployed ransomware without human intervention. ENCFORGE appears to build on that framework, incorporating heuristics that identify AI‑related file signatures and vector store formats such as FAISS or Milvus. This level of specificity suggests the group has either recruited expertise in machine‑learning pipelines or is leveraging open‑source tooling to automate the extraction of AI assets.
Experts warn that defenders must broaden their security posture to include AI‑specific safeguards. Traditional endpoint protection may miss the nuanced file types and storage patterns used by modern ML workflows. Recommendations include segmenting AI workloads, encrypting training data at rest, implementing strict access controls on model repositories, and regularly auditing cloud configurations for exposed endpoints. As threat actors like JADEPUFFER continue to adapt, organizations will need to treat AI models as critical infrastructure and defend them with the same rigor applied to financial or operational systems.



Comments (0)
Be the first to comment.
Join the discussion