New Phishing Toolkits Target Microsoft 365 Sessions, Researchers Reveal
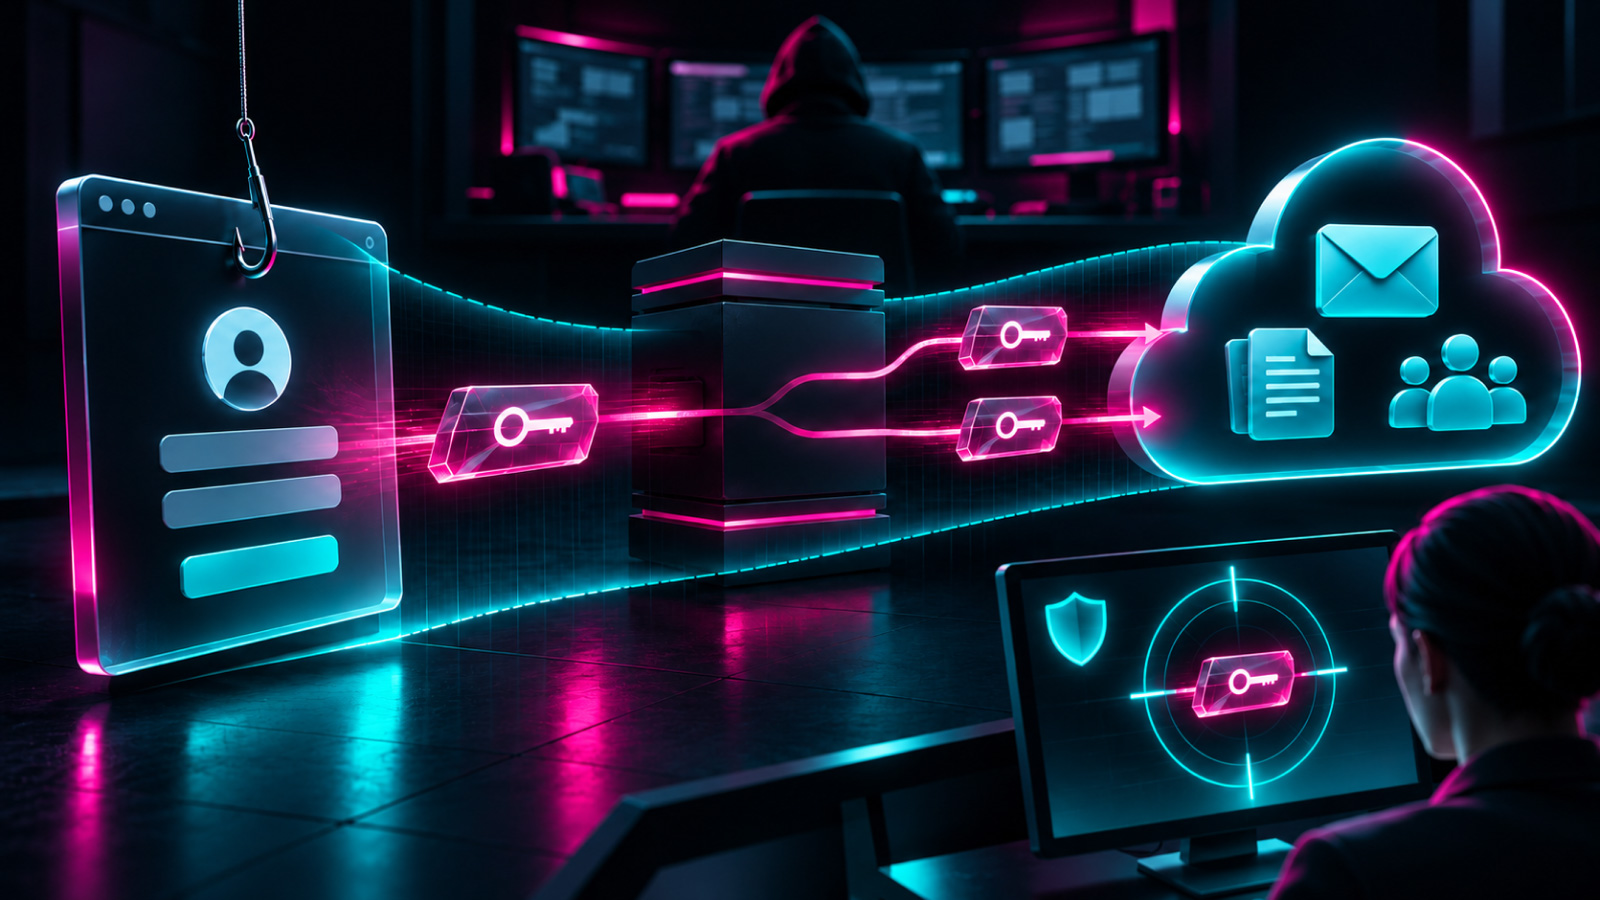
Security researchers at Huntress have dissected three recently observed phishing kits—EvilTokens, Knight Office and Kali365—that are designed to harvest Microsoft 365 authentication tokens and replay them to gain unauthorized access to corporate accounts.
Microsoft 365 relies on short‑lived access tokens rather than static passwords, allowing users to stay signed in across devices. While this improves convenience, the tokens become valuable loot for attackers because they can be used to act as the legitimate user until they expire.
The three kits employ distinct approaches to capture those tokens. EvilTokens injects malicious JavaScript through a crafted email attachment, prompting the victim's browser to dump cached tokens from the local storage. Knight Office embeds a rogue Office add‑in that runs when a user opens a seemingly benign document, siphoning tokens directly from the Office client. Kali365 creates a counterfeit Microsoft login page that forwards entered credentials to a backend server, which then harvests the resulting session token.
Once a token is obtained, the kits transmit it to a command‑and‑control server where it can be replayed against Microsoft’s APIs. Because the token is already validated, the attacker can read emails, download files, or even modify settings without triggering password‑based alerts, effectively bypassing multi‑factor authentication that is tied to the original sign‑in event.
Defenders are advised to look for signs of token misuse, such as sign‑ins from geographically impossible locations, rapid succession of logins from multiple IPs, or the appearance of unfamiliar device identifiers in Azure AD sign‑in logs. Deploying conditional access policies that require re‑authentication for high‑risk actions, enforcing strict MFA, and monitoring for the known indicators of the three kits can help limit exposure.
The emergence of modular phishing kits that focus on token theft underscores a shift in threat actor tactics. As these tools become more widely available, security teams will need to rely on behavior‑based detection and rapid response playbooks to contain compromised sessions before attackers can leverage them for broader intrusion.

Comments (0)
Be the first to comment.
Join the discussion