HTML-Rendered QR Codes Bypass Traditional Email Phishing Defenses
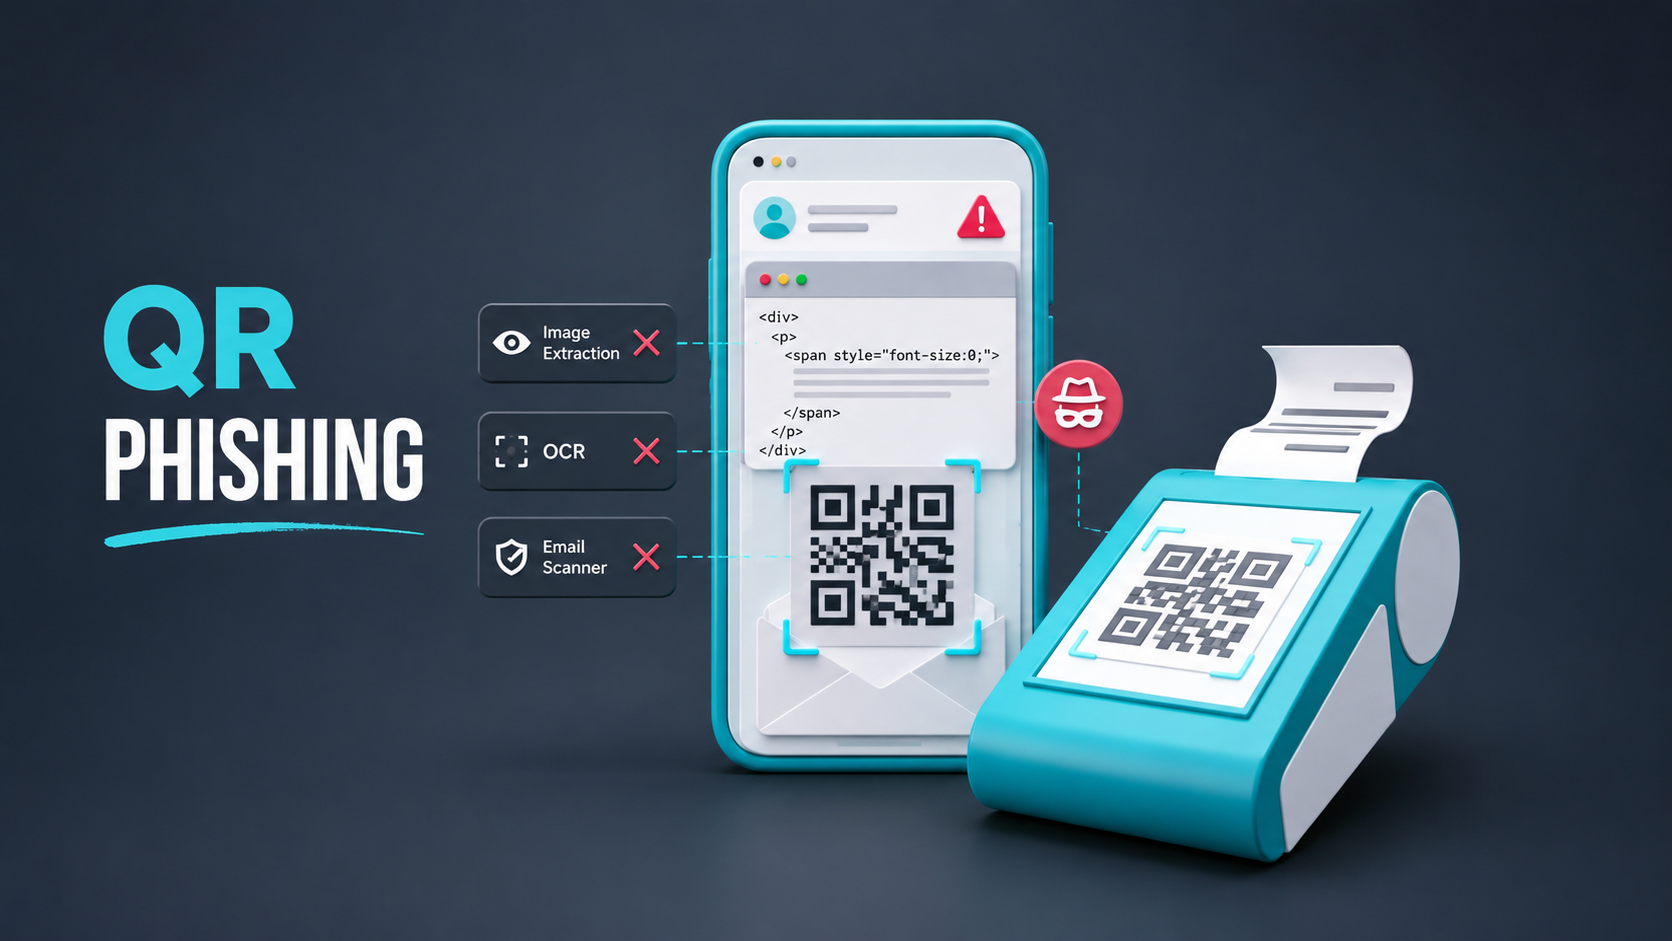
Security researchers have identified a new twist in QR-code phishing, or "quishing," where attackers embed scannable codes directly into the HTML of an email rather than attaching image files. By generating QR symbols from table cells or plain text strings within the message body, the malicious links evade detection tools that rely on image extraction or optical character recognition (OCR) to flag suspicious content.
The technique was first documented by the GBHackers community, which noted that the absence of tags or bitmap attachments leaves conventional email scanners without a visual element to analyze. Instead, the QR code is constructed on the fly by the recipient's email client rendering the HTML, allowing the code to be displayed and scanned without ever existing as a separate file. This approach sidesteps security products that flag known phishing image hashes or scan embedded pictures for hidden URLs.
Experts say the shift reflects a broader trend of attackers adapting to the increasingly sophisticated anti‑phishing measures deployed by enterprises. Modern email gateways employ OCR to read text inside images and compare it against known malicious patterns. By moving the payload into the HTML layer, threat actors exploit the fact that many security solutions treat rendered HTML as trusted content, assuming that any visual element originates from a legitimate source.
While the method is technically more complex, it does not require advanced infrastructure. Attackers can generate QR codes using open‑source libraries that output SVG or CSS‑based graphics, then embed the code within a table layout that mimics the appearance of a regular email. Recipients who scan the QR code with a smartphone are directed to phishing sites that harvest credentials, install malware, or prompt the download of additional payloads. The lack of an image file also reduces the chance of the email being flagged by size‑based heuristics or attachment filters.
Defenders are now looking to update detection strategies by analyzing HTML structures for patterns associated with QR generation, such as repetitive data‑URI strings or specific CSS classes. Some email security vendors are experimenting with rendering the HTML in a sandboxed environment to capture any dynamically created QR symbols for further inspection. As the arms race continues, organizations are advised to educate users about the risks of scanning QR codes from unsolicited messages and to treat any unexpected QR prompt with caution, regardless of its visual origin.



Comments (0)
Be the first to comment.
Join the discussion