Governments Deploy Technical Tactics to Spot VPN Traffic Despite Encryption
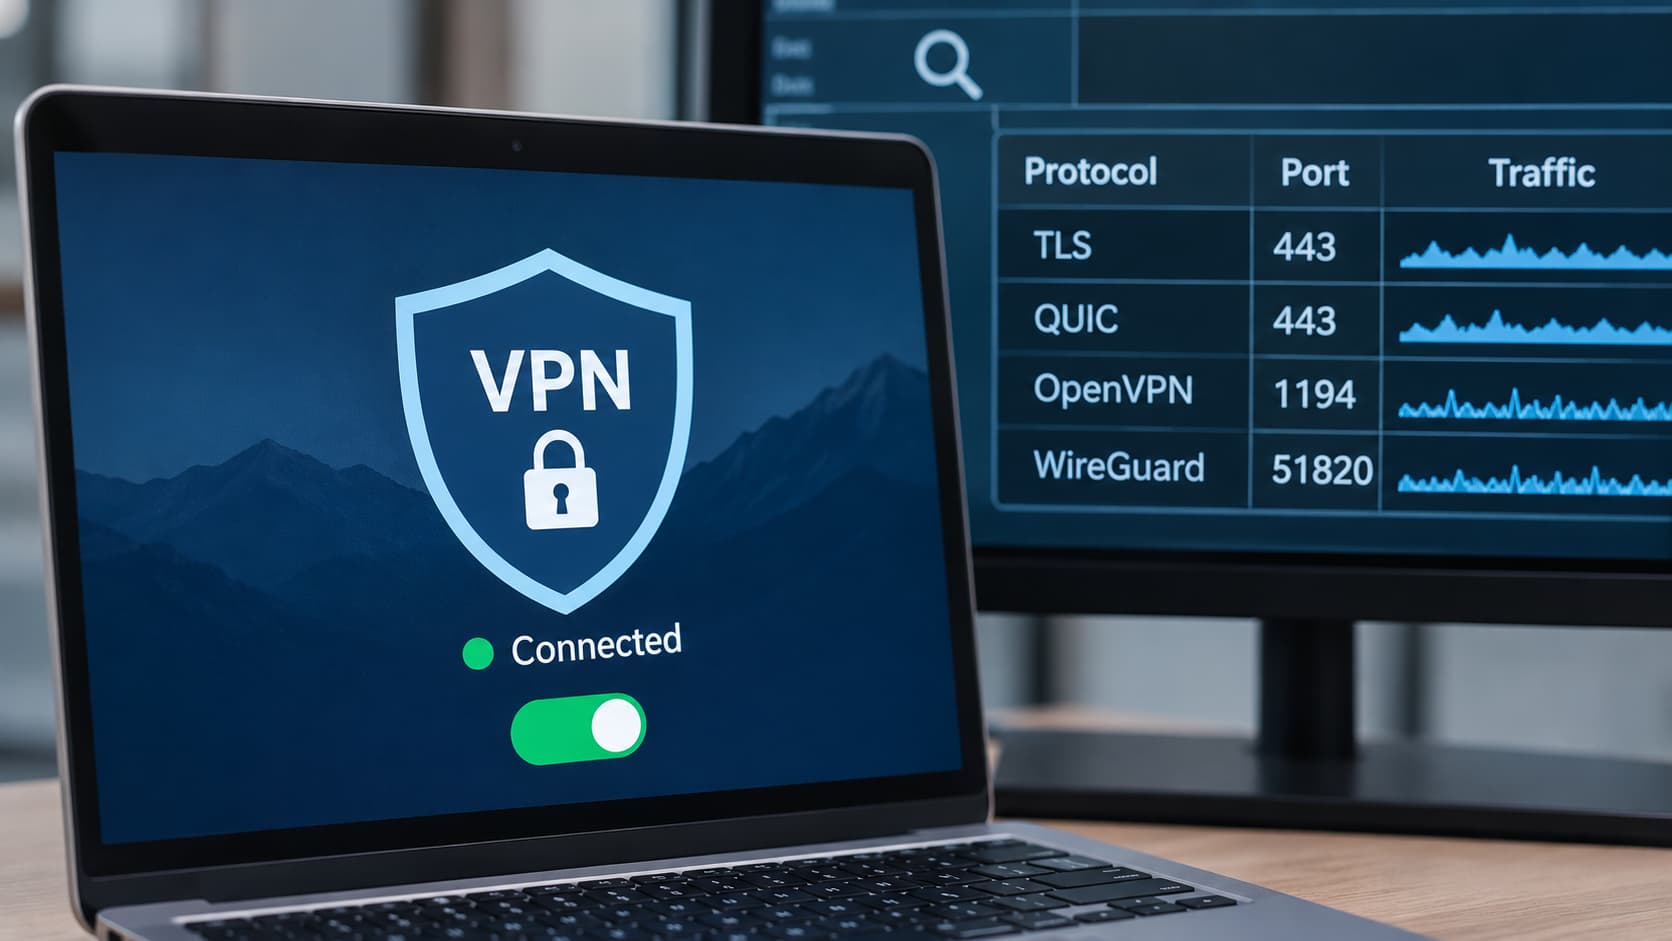
Authorities around the world are sharpening their ability to single out virtual private network (VPN) connections, even though the data they carry is encrypted. By combining network‑level clues with targeted probes, regulators can identify and block VPN use, undermining the common belief that encryption alone guarantees anonymity.
One of the first steps in the detection process involves scrutinizing IP addresses. Many VPN providers operate a limited set of server endpoints that can be catalogued and shared among law‑enforcement agencies. When a user’s traffic originates from an address that appears on a known VPN list, it raises a flag that prompts further investigation or outright blocking.
Beyond simple IP matching, governments examine the technical “fingerprint” of the traffic itself. Different VPN protocols—such as OpenVPN, WireGuard, or IPSec—exhibit distinctive packet sizes, timing patterns and handshake sequences. Sophisticated monitoring tools can match these signatures against a database of known behaviors, allowing analysts to infer the presence of a VPN even when the payload remains encrypted.
In more aggressive cases, agencies employ active probing. By sending crafted packets to a suspect endpoint and observing the response, they can confirm whether the host is running VPN software and sometimes even identify the specific client or configuration in use. This approach turns the VPN server into a test subject, revealing details that passive observation alone would miss.
The ability to detect VPN traffic has practical consequences for users seeking privacy or to bypass geo‑restrictions. Encryption protects the contents of a communication, but it does not hide the fact that a VPN is being used, making it vulnerable to blocking or legal scrutiny. As governments continue to refine these detection methods, VPN providers are forced to rotate IPs, obfuscate protocol signatures, or adopt new stealth techniques, while users must stay informed about the limits of encryption as a shield against surveillance.



Comments (0)
Be the first to comment.
Join the discussion