South Korean Megachurches Probe Data Breach Threatening Hundreds of Thousands of Members
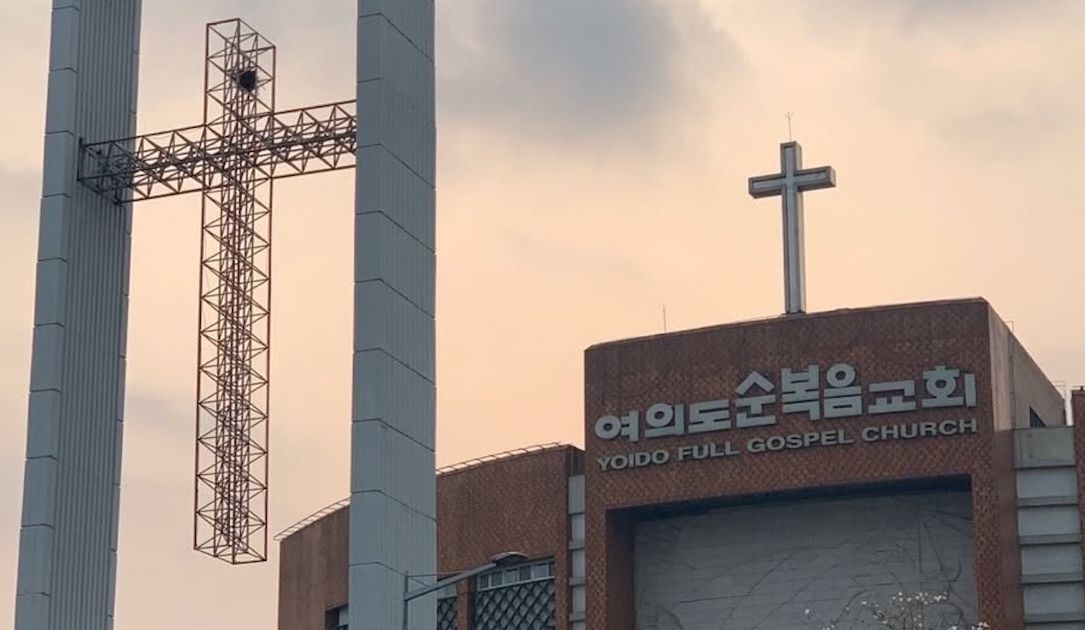
Two of South Korea's biggest Protestant megachurches have launched investigations after cyber attackers reportedly accessed internal systems, raising fears that personal and financial details of a vast congregation could have been exposed. The incidents, first reported by The Record, involve networks that manage member registries, donation records and internal communications, potentially affecting hundreds of thousands of worshippers.
Preliminary findings suggest that the breach may have yielded names, contact information, resident registration numbers, and contribution histories. In addition, confidential documents outlining church governance and strategic plans appear to have been retrieved. While the full scope of the compromise remains unclear, church officials acknowledge that the data could be used for identity theft, fraud, or targeted phishing campaigns.
South Korea's religious landscape includes several megachurches whose membership numbers rival those of small cities. These institutions rely heavily on digital platforms to coordinate services, manage donations and maintain member outreach, making them attractive targets for cybercriminals seeking rich troves of personal data. Past incidents in the region have shown that religious organizations can be vulnerable to ransomware and data‑theft attacks, prompting calls for stronger cybersecurity frameworks.
Authorities have been alerted, and the churches are cooperating with law‑enforcement agencies to trace the source of the intrusion. Legal experts note that South Korean privacy law imposes strict obligations on entities that handle sensitive personal information, and failure to protect such data can result in substantial penalties. Church leaders have publicly apologized to congregants, pledged to enhance security measures, and urged members to monitor their accounts for suspicious activity.
The ongoing investigations are expected to culminate in a detailed forensic report, after which the churches plan to roll out multi‑factor authentication, regular security audits and staff training. The incidents underscore a broader trend of cyber threats targeting non‑profit and religious sectors worldwide, prompting industry observers to recommend a coordinated response that includes government guidance, sector‑specific best practices and heightened awareness among members.



Comments (0)
Be the first to comment.
Join the discussion