Hackers Leverage TanStack Supply Chain Breach to Access Hundreds of CrowdSec Private Repos
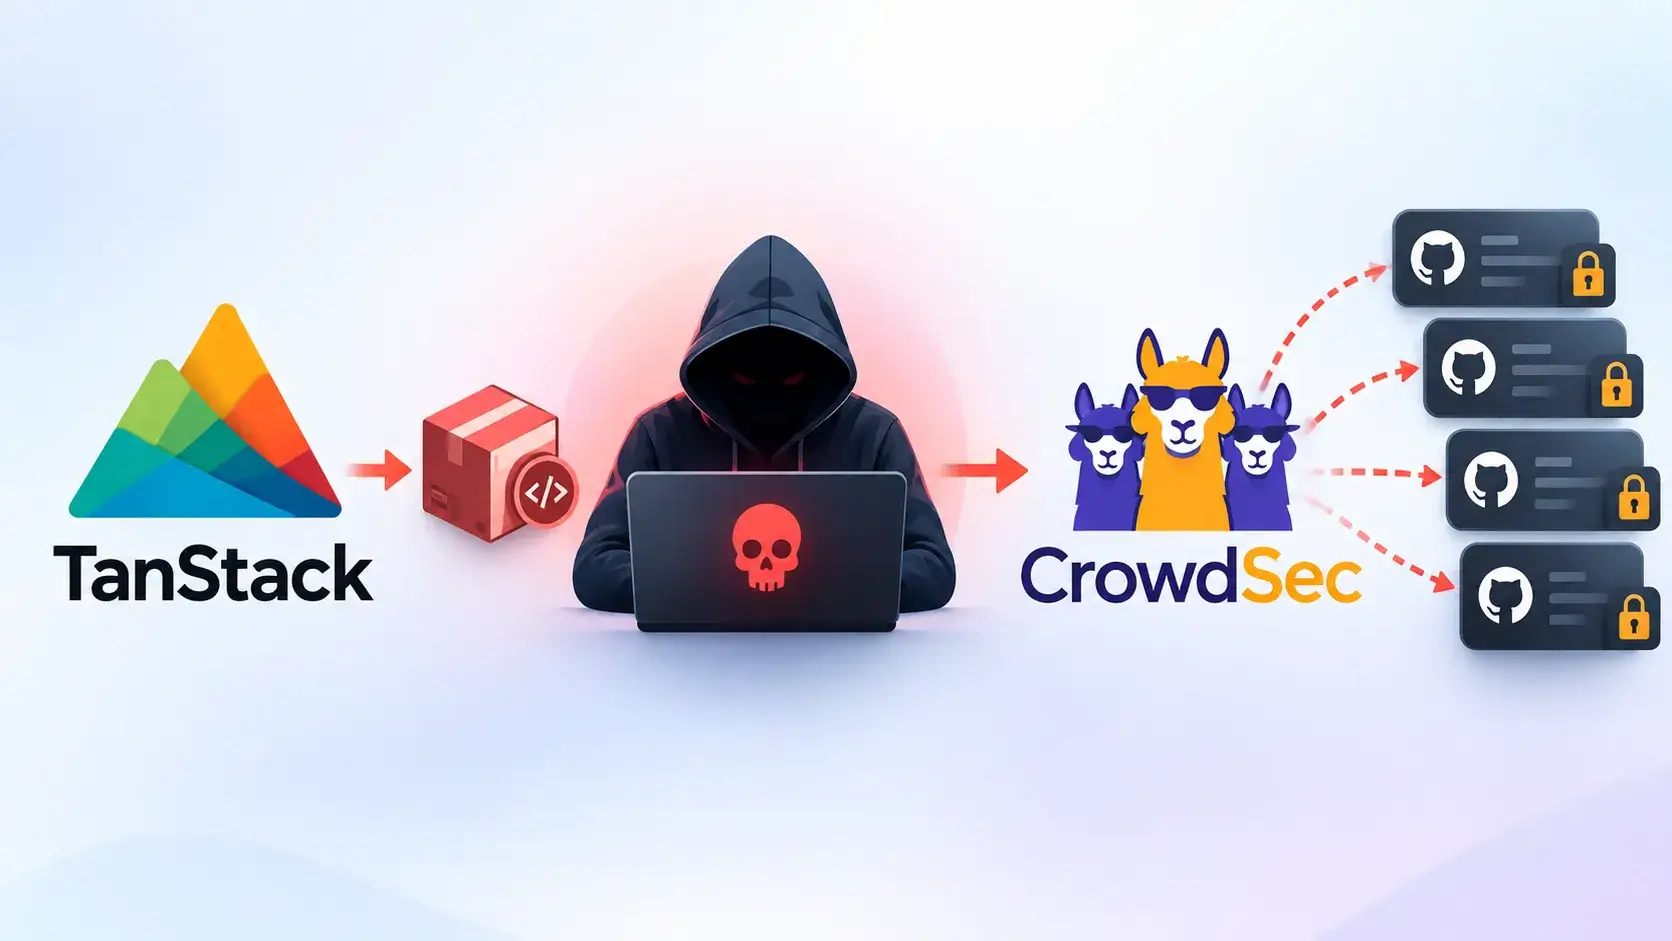
Security researchers have confirmed that threat actors exploiting a recent supply‑chain compromise in the TanStack npm package used a stolen GitHub OAuth token to duplicate roughly 170 private repositories belonging to CrowdSec, an open‑source threat‑intelligence platform.
The intrusion was uncovered after CrowdSec detected unusual cloning activity on its GitHub organization. Investigators traced the activity back to an OAuth credential that appeared to have been harvested during the TanStack supply‑chain attack, a separate incident that involved malicious code injected into a widely used JavaScript library. By leveraging the token, the attackers were able to bypass standard authentication checks and pull down private codebases, limited contact details, and a constrained AWS notification credential used for internal alerts.
CrowdSec, which provides a community‑driven approach to detecting and mitigating cyber threats, confirmed that the exposed assets did not include any production secrets such as API keys or customer data. However, the source code and the AWS credential, albeit restricted, could give adversaries insight into the company’s detection logic and potentially aid in crafting more targeted attacks against its users.
The incident underscores the growing risk of supply‑chain vulnerabilities, where a compromised component in a popular development ecosystem can cascade into multiple downstream victims. Experts note that the TanStack compromise, first reported by GBHackers, highlights how attackers can move laterally across ecosystems by exploiting trusted developer tools. Organizations are being urged to rotate OAuth tokens regularly, enforce least‑privilege access, and monitor for anomalous repository activity.
While CrowdSec has not disclosed any immediate operational impact, it is working with GitHub and its own security team to remediate the breach, revoke the compromised token, and audit all related credentials. The company also plans to publish additional guidance for its community on securing third‑party dependencies and managing access tokens. The broader security community continues to watch the fallout from the TanStack incident, emphasizing that supply‑chain hygiene is now a critical component of any robust cybersecurity strategy.



Comments (0)
Be the first to comment.
Join the discussion