French Supermarkets Hit by Remote Defrosting Cyberattack on Refrigeration Systems
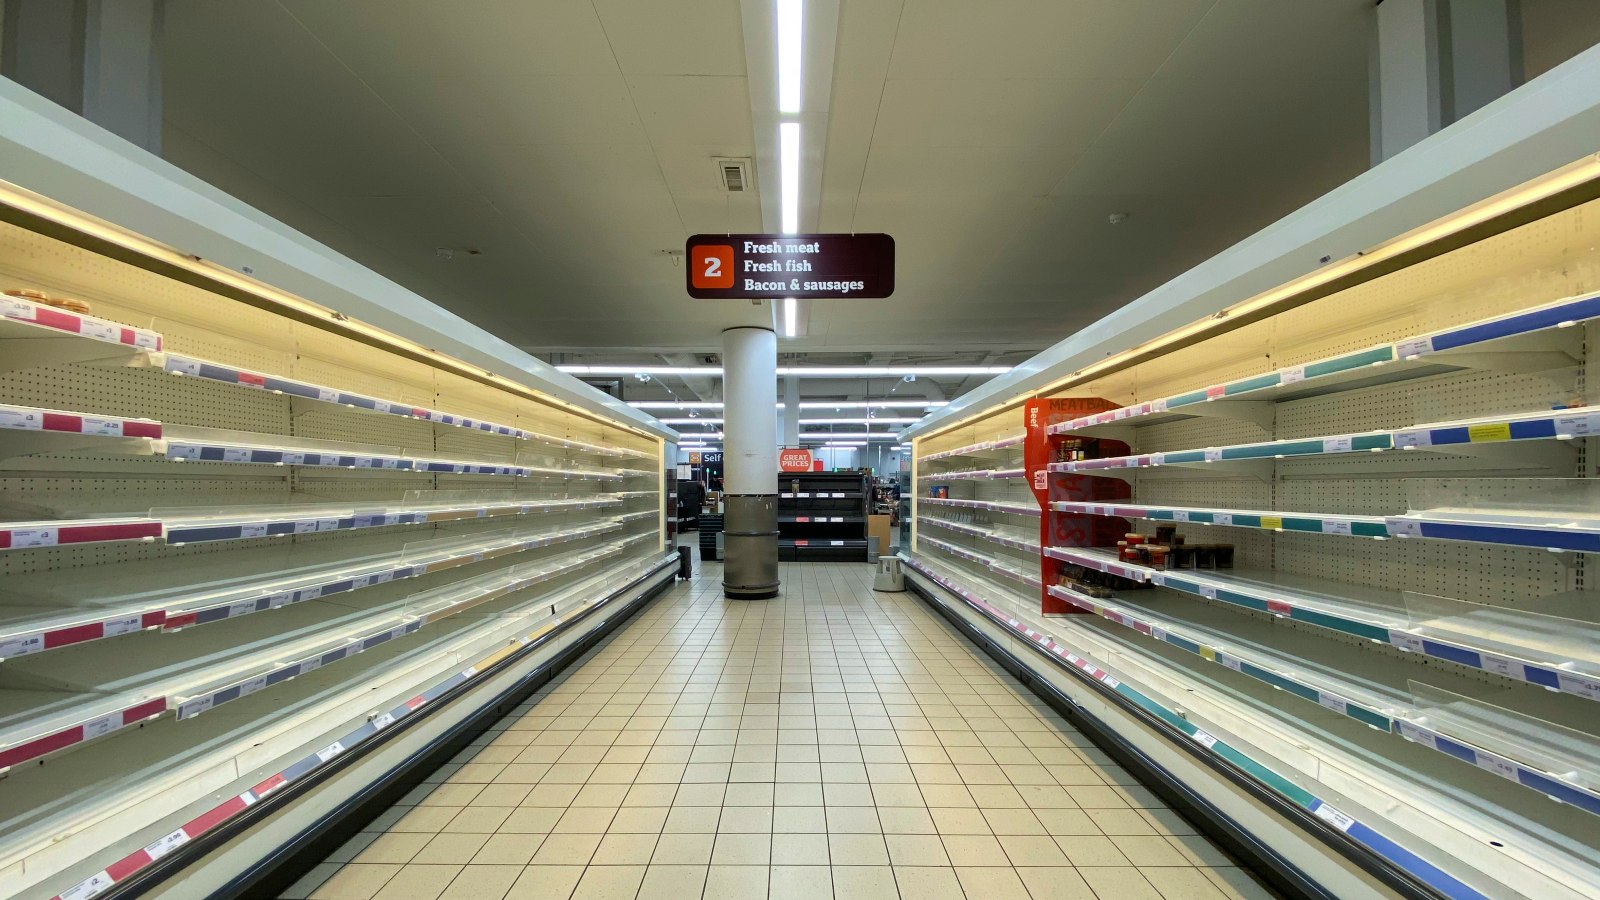
Overnight, a coordinated cyber intrusion caused the refrigeration units in several French supermarket chains to malfunction, leading to an unexpected defrosting of stored goods. The incident, first reported by security outlet BleepingComputer, appears to have targeted Danfoss‑manufactured refrigeration controllers that manage temperature across the stores' cold‑storage equipment.
According to preliminary technical analysis, the attackers gained remote access to the Danfoss controllers and issued commands that disabled the cooling cycles, effectively raising internal temperatures to ambient levels. The breach was discovered when store personnel noticed a sudden loss of cold in display freezers and walk‑in coolers, prompting an immediate shutdown of affected units to prevent further damage.
The disruption forced multiple supermarkets to remove perishable items from shelves, discard spoiled products, and temporarily suspend sales of temperature‑sensitive goods such as dairy, meat, and frozen foods. While the exact financial impact has not been disclosed, industry analysts note that even short‑term loss of refrigeration can result in significant waste and operational setbacks for retailers that rely on just‑in‑time inventory turnover.
Incidents targeting industrial control systems have risen in recent years, with hackers increasingly exploiting vulnerabilities in equipment that was originally designed for operational efficiency rather than cybersecurity. Danfoss, a global supplier of HVAC and refrigeration components, has previously warned of potential threats to its devices, emphasizing the need for robust patch management and network segmentation. This latest event underscores the broader risk that legacy control hardware poses to critical supply‑chain infrastructure.
In response, Danfoss issued an advisory urging customers to review security configurations and apply the latest firmware updates. The affected supermarket chains have launched internal investigations, coordinated with French cyber‑security authorities, and temporarily reverted to backup cooling solutions where possible. Law‑enforcement agencies are reportedly examining the attack for links to known threat actors, though no group has claimed responsibility at this stage.
Experts say the episode may accelerate a shift toward more secure, IoT‑ready refrigeration platforms and reinforce regulatory scrutiny of cyber‑risk management in the food‑retail sector. As investigations continue, retailers are expected to bolster monitoring of their control networks and consider redundancy measures to mitigate the impact of any future breaches.



Comments (0)
Be the first to comment.
Join the discussion