Fake Crypto Wallet App Serves New macOS PamStealer Variant to Harvest User Secrets
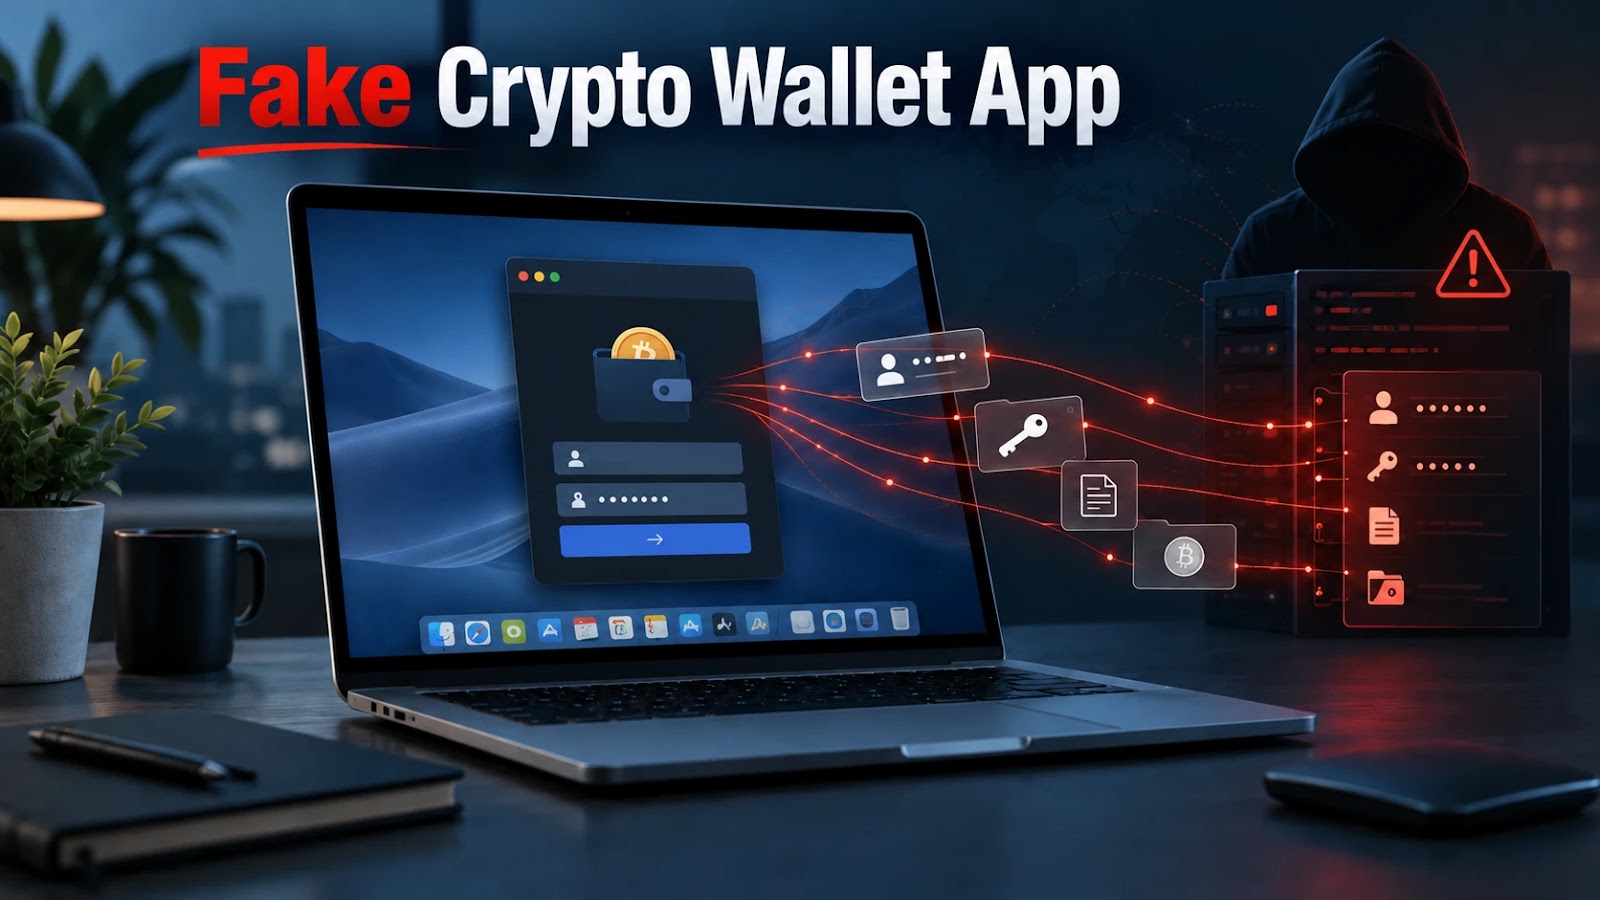
Security researchers have identified a fresh macOS‑focused infostealer that is being distributed through a counterfeit cryptocurrency wallet application, marking the latest evolution of the PamStealer malware family.
The malicious program, described as a new variant of PamStealer, employs a server‑assisted decryption chain and a Swift‑based payload to bypass macOS defenses. Once the fake wallet is installed, the payload contacts a remote server to retrieve encrypted components, which are then decrypted on the victim’s machine before execution.
After activation, the malware scans the system for a range of sensitive items. It extracts saved passwords from browsers, harvests credentials stored in Apple’s Keychain, and copies files that may contain personal or financial information. The stolen data is then packaged and transmitted back to the attacker’s command‑and‑control infrastructure.
The campaign targets users who are actively seeking cryptocurrency management tools, exploiting the high‑value perception of crypto wallets to increase download rates. By masquerading as a legitimate wallet, the app gains the trust of users who may already be handling valuable digital assets, making the stolen credentials especially lucrative for threat actors.
PamStealer first emerged in the wild as a Windows‑only infostealer in 2022, and its migration to macOS reflects a broader trend of malware authors expanding their toolkits to cover Apple’s desktop platform. The use of Swift for the payload indicates a shift toward native macOS development techniques, which can make detection more challenging for traditional antivirus solutions that are tuned to older, cross‑platform code bases.
Experts advise macOS users to download software exclusively from the official App Store or verified vendor sites, and to verify digital signatures before installation. Keeping the operating system and security tools up to date can also mitigate the risk of such attacks. Researchers will continue to monitor the distribution network for additional indicators of compromise, and Apple’s security team is expected to review the findings for possible mitigations in future updates.



Comments (0)
Be the first to comment.
Join the discussion